Pricing
Plans from Starter to Ultimate, try it free for 30 days.
An ISMS to ISO/IEC 27001 can be run with Word and Excel, until approvals, due dates and evidence are scattered across many files. Varmo brings the standard and the workflow together: every requirement has its place, every person their tasks.
The standard does not prescribe a tool. It requires documented information, traceable decisions and a cycle of plan, do, check and act. A tool helps when the evidence is created as part of the workflow instead of being collected before the audit.
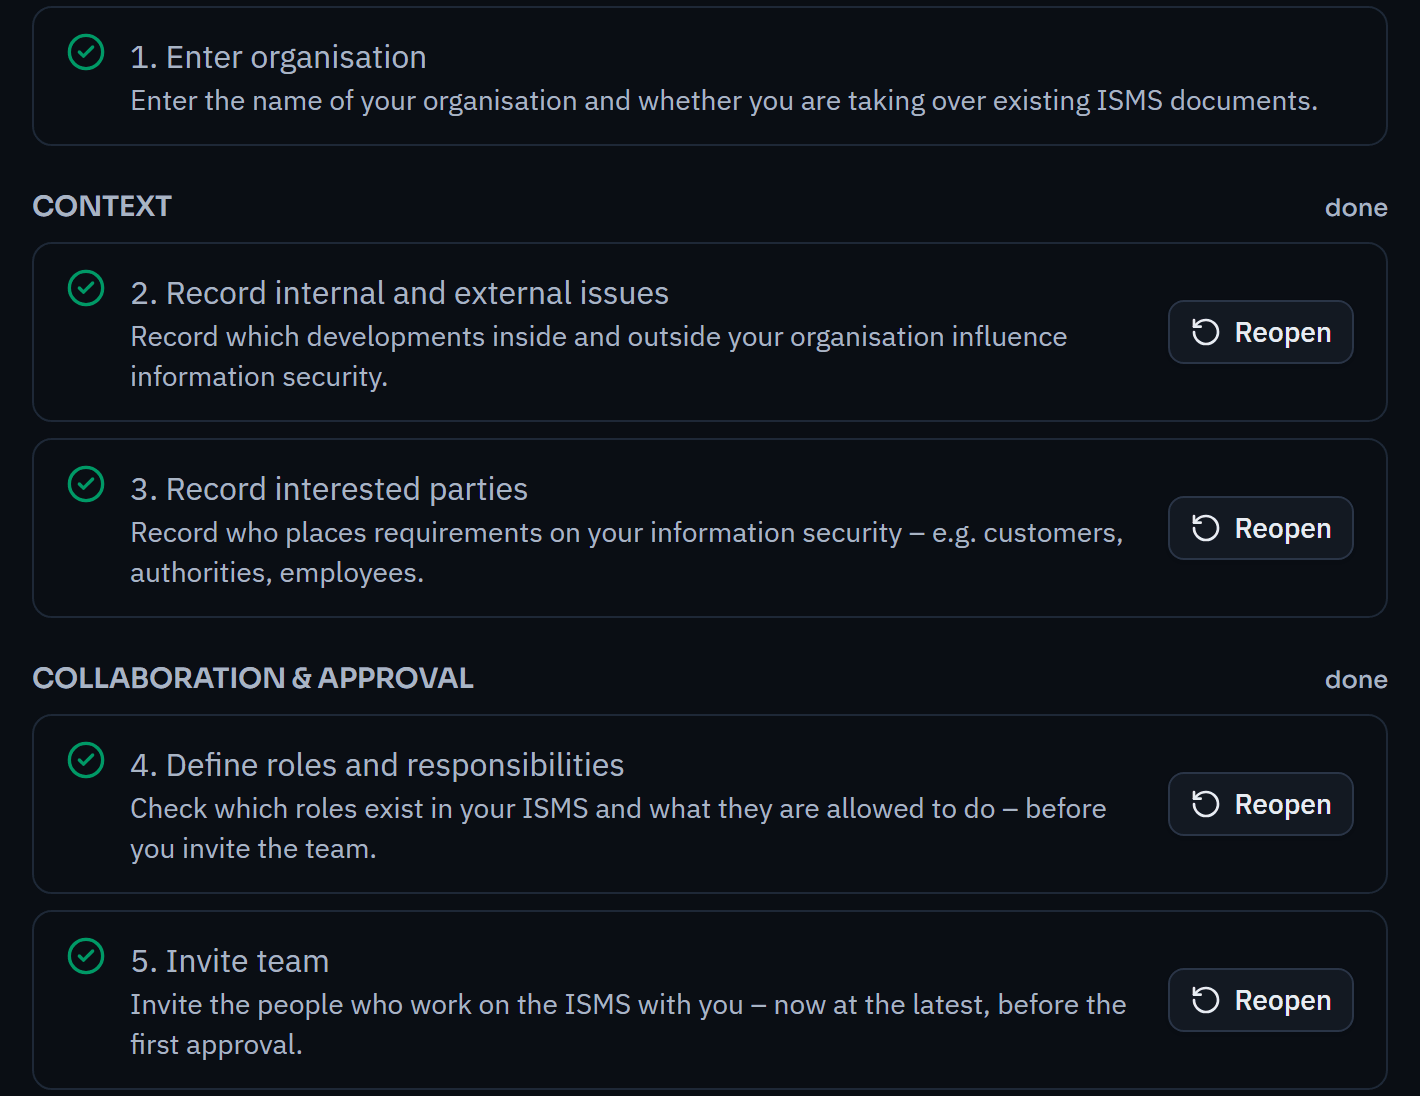
The setup assistant takes you through the build in 22 steps: organisation, context, approvals, risk methodology, frameworks, assets, incidents, internal audit and management review. Every step explains what it is about and why.
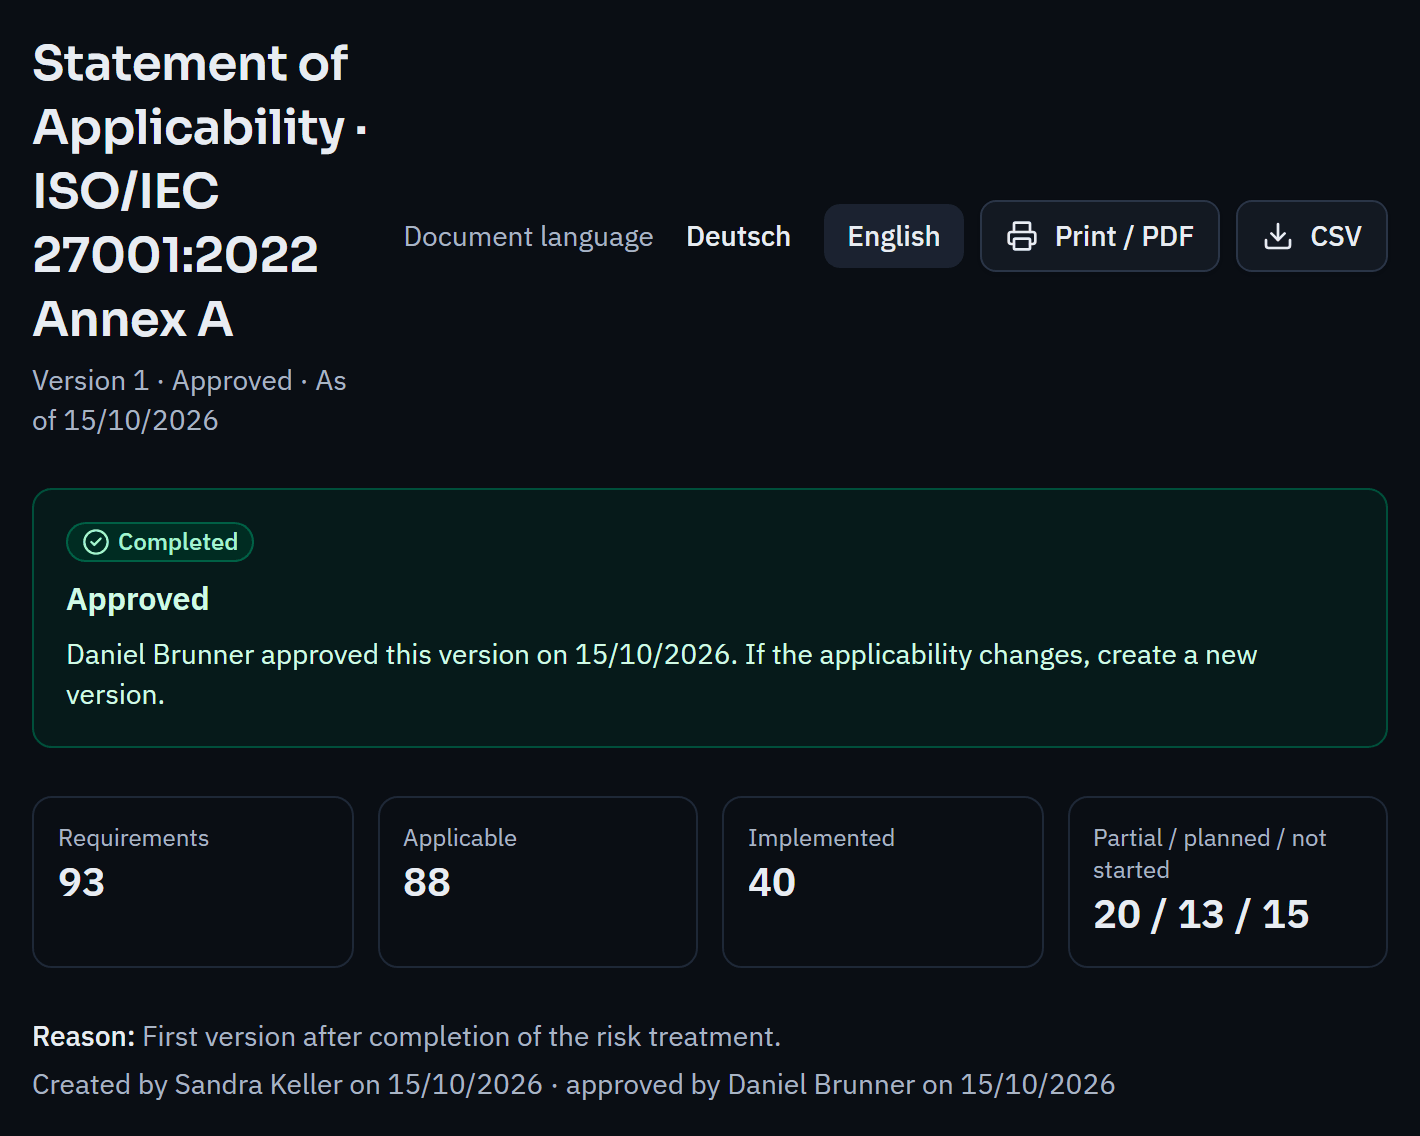
You assess risks according to BSI Standard 200-3 or your own matrix and decide on treatment. You select the Annex A requirements through the risk treatment; this produces the Statement of Applicability, which you approve, print and export as CSV.
Everyone sees what they need to do: implement a measure, perform a control, acknowledge a policy, review a risk. The “What happens next?” notice shows in every workflow who is up next.
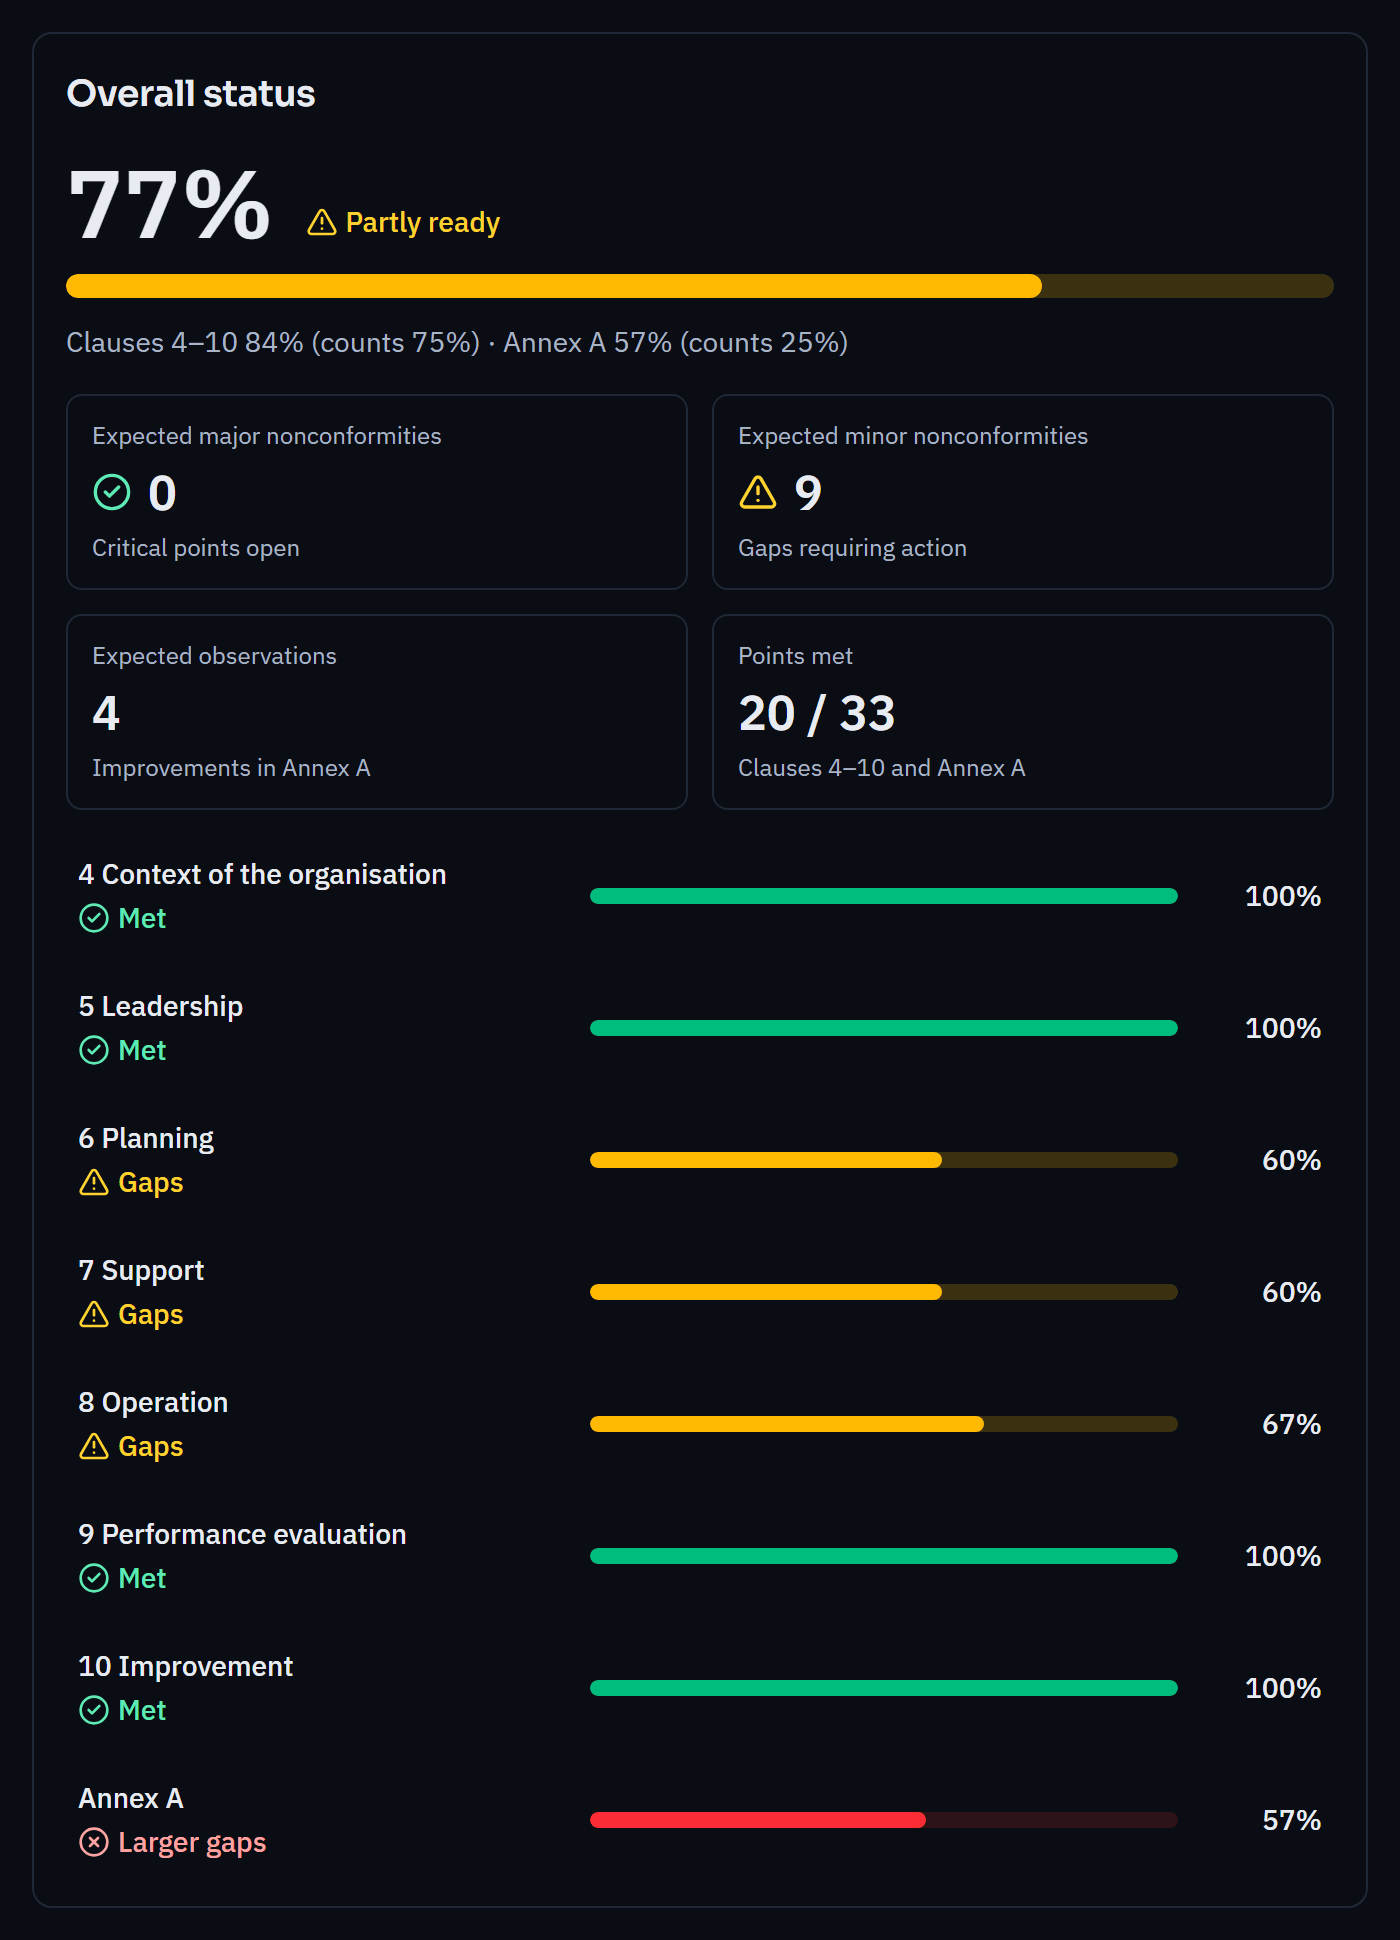
In all plans, the readiness check uses your data to assess 26 points on clauses 4 to 10 and up to 7 on Annex A, and records each status as a report. The certificate itself is granted by an accredited certification body.
From the Business plan, the software maps equivalent requirements of other frameworks to each other, such as NIS2, the Swiss ICT baseline protection or BSI Grundschutz++; NIST, FINMA Circular 2023/1 and DORA are added with the Pro plan. Implement once, evidence many times.
Starter, Business and Pro are priced by the number of active people; Ultimate is available on request. The trial lasts 30 days, is free and includes every feature. Afterwards you choose a plan; without a purchase the account is frozen, and you can still read and export.
Plans from Starter to Ultimate, try it free for 30 days.
The way to the external audit.
Free, in about 5 minutes.
Excel and Word, a document store, a GRC suite or Varmo.
In substance, none. Both terms mean software with which you build and run an ISMS to ISO/IEC 27001. What matters is whether the tool covers the whole standard, from clauses 4 to 10 to Annex A, or only part of it, such as risks or documents.
No. The standard does not prescribe a tool. Software mainly saves time keeping due dates, approvals and evidence up to date, and shows before the audit where gaps remain.
Yes. The trial lasts 30 days, is free and includes every feature. The free self-assessment on the website gives a first impression of where your ISMS stands.
How close are you to ISO/IEC 27001?
Try it free for 30 days with every feature, no credit card required. Or let us show you the way to the readiness report in a personal demo, with no obligation.