Security and data protection at Varmo
Varmo stores your data in Switzerland, separates organisations in the database and gives us as the operator time-limited, read-only access only with your approval. Every uploaded file is scanned for malware before it is stored.
Varmo holds how your organisation runs information security – risks, vulnerabilities, incidents. We protect this data the way we expect an ISMS to. This page sets out what we actually do.
Data location: Your ISMS data stays in Switzerland
Your data – content, accounts, files and backups – is stored exclusively in a data centre in Switzerland. The provider is a Swiss company whose voting majority is held by a foundation; there is no parent company in the US. We operate the database, sign-in, malware scanning and error tracking ourselves on our own servers, without cloud services from US providers.12
Built on proven open-source technology, operated by us in Switzerland. This keeps us independent of individual providers: we can change hosting provider without changing the software.
Data sovereignty, the US CLOUD Act and every service involved- Note 1: Exception for card payments: if you pay by credit card, our payment service provider Stripe (Stripe Payments Europe Ltd., Ireland, part of a US group) receives your billing details, never your ISMS content. If you pay by invoice, no data goes to Stripe.
- Note 2: Integrations that you switch on yourself (e.g. Microsoft Entra ID, Teams, Intune, JIRA, ServiceNow, calendar subscription) connect Varmo with the respective provider; that provider’s terms apply.
Strict separation of organisations
Each organisation sees only its own data. The database itself enforces the separation (row-level access rules for every table), and the application checks it as well. With every change to the product, several hundred automated security tests run, including attempts to access another organisation’s data. A structural test checks every table and every database function to ensure it enforces the separation.
No access by us without your approval
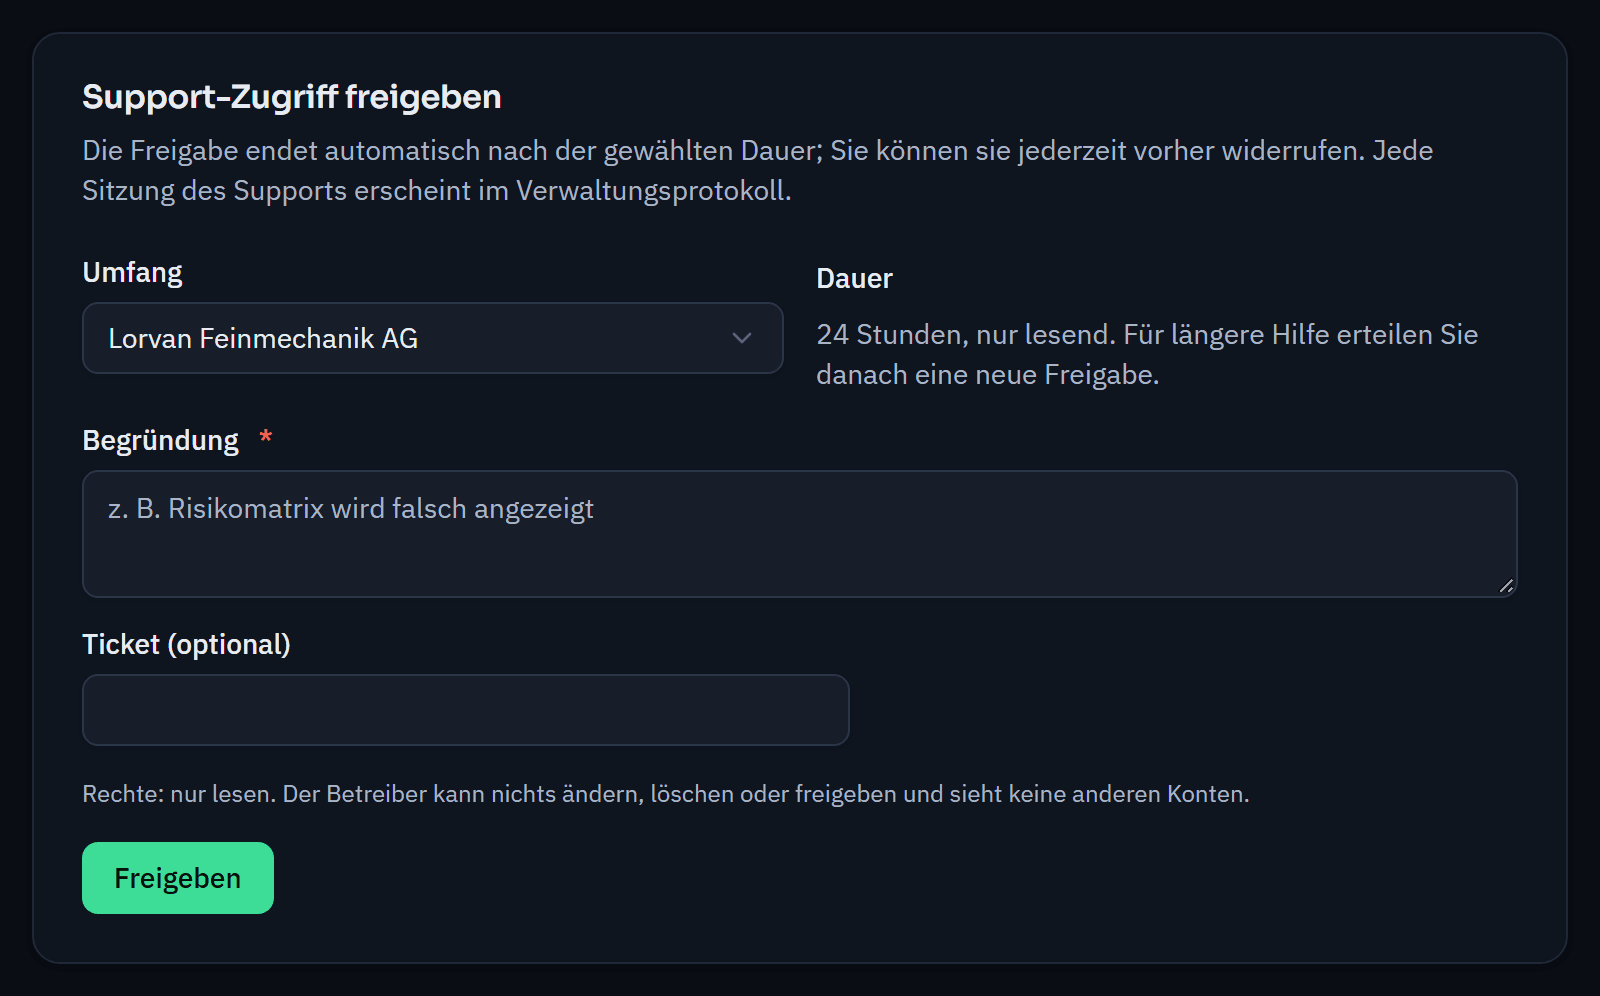
As the operator, we have no access to your organisation’s content. If we need to look at something for support, an administrator in your organisation grants this explicitly – limited to no more than 24 hours and read-only; every access is recorded in the organisation’s log. During this time the database prevents any change. Approval, start and end are recorded in your administration log.
Permissions on a need-to-know basis
People receive only the permissions of their functional roles and, beyond that, see only what they are responsible for. Your organisation’s administrators manage people and access and run the ISMS; they see the change log only with a separate permission. Segregation of duties and the four-eyes principle for approvals (e.g. risk acceptance, policies) are anchored in the database.
Secure sign-in
- Passwords with at least 12 characters; new accounts on the Free plan only after the email address has been confirmed.
- Second factor with an authenticator app or security key, or sign-in with a passkey – on all plans.
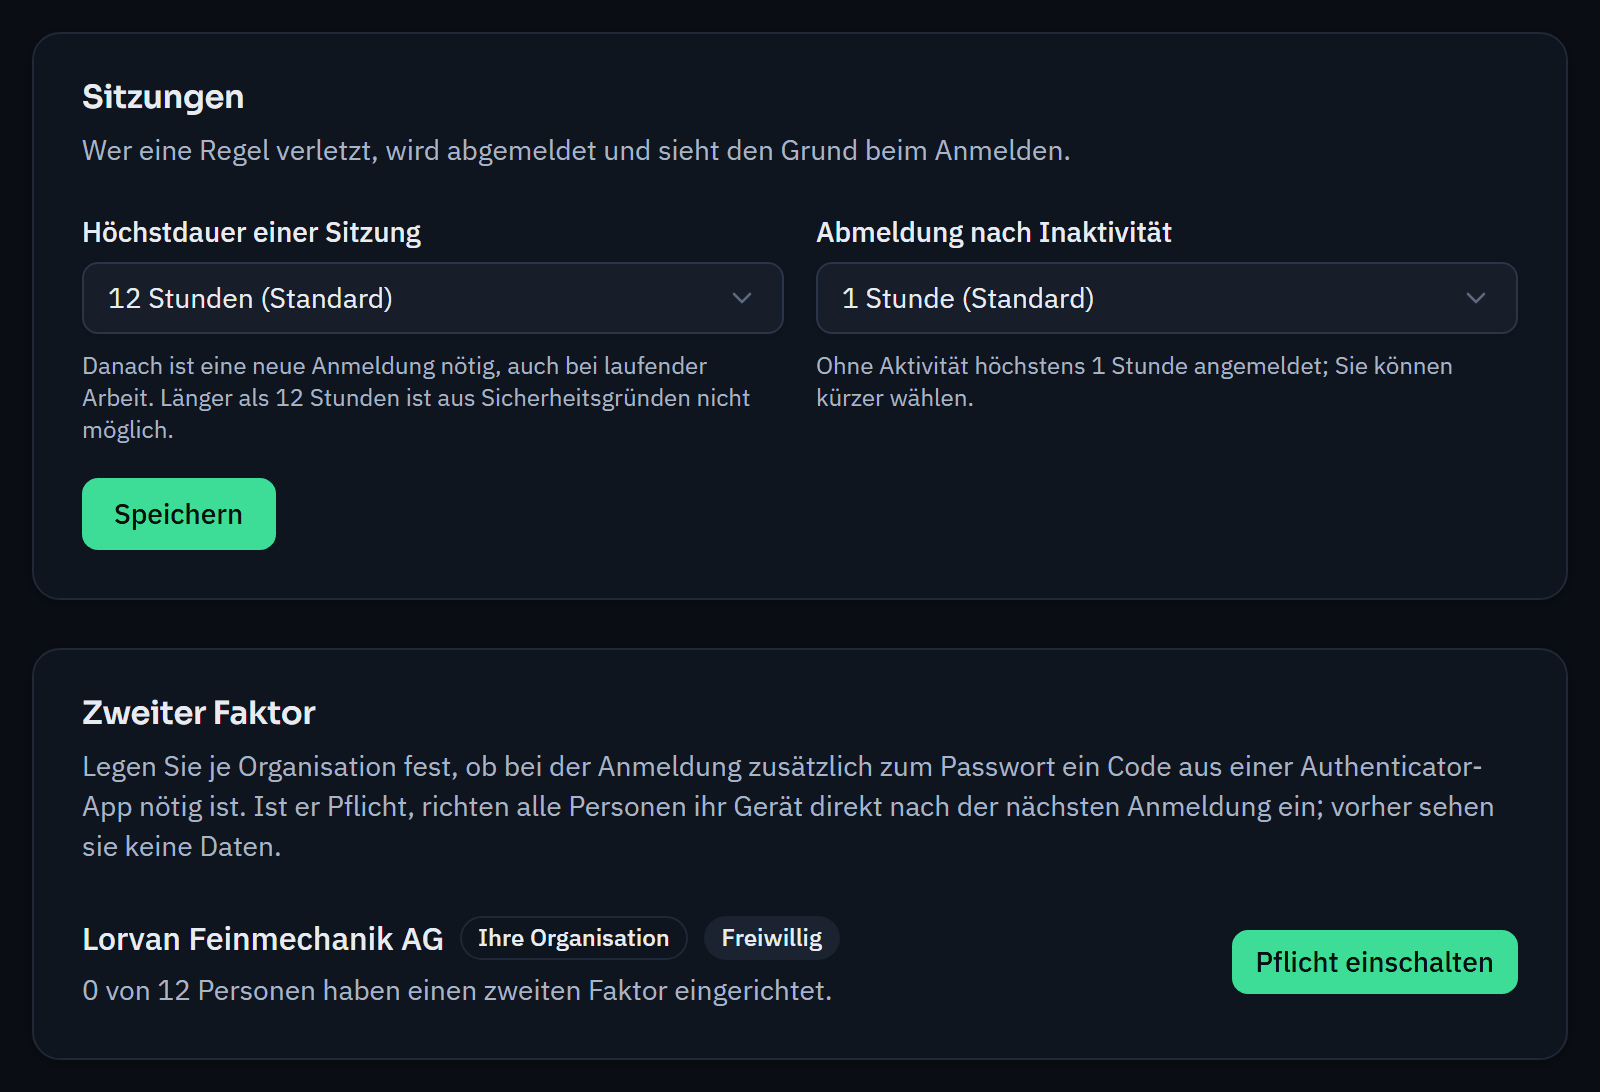
- Your organisation can make the second factor mandatory for everyone; the requirement applies from the next sign-in.
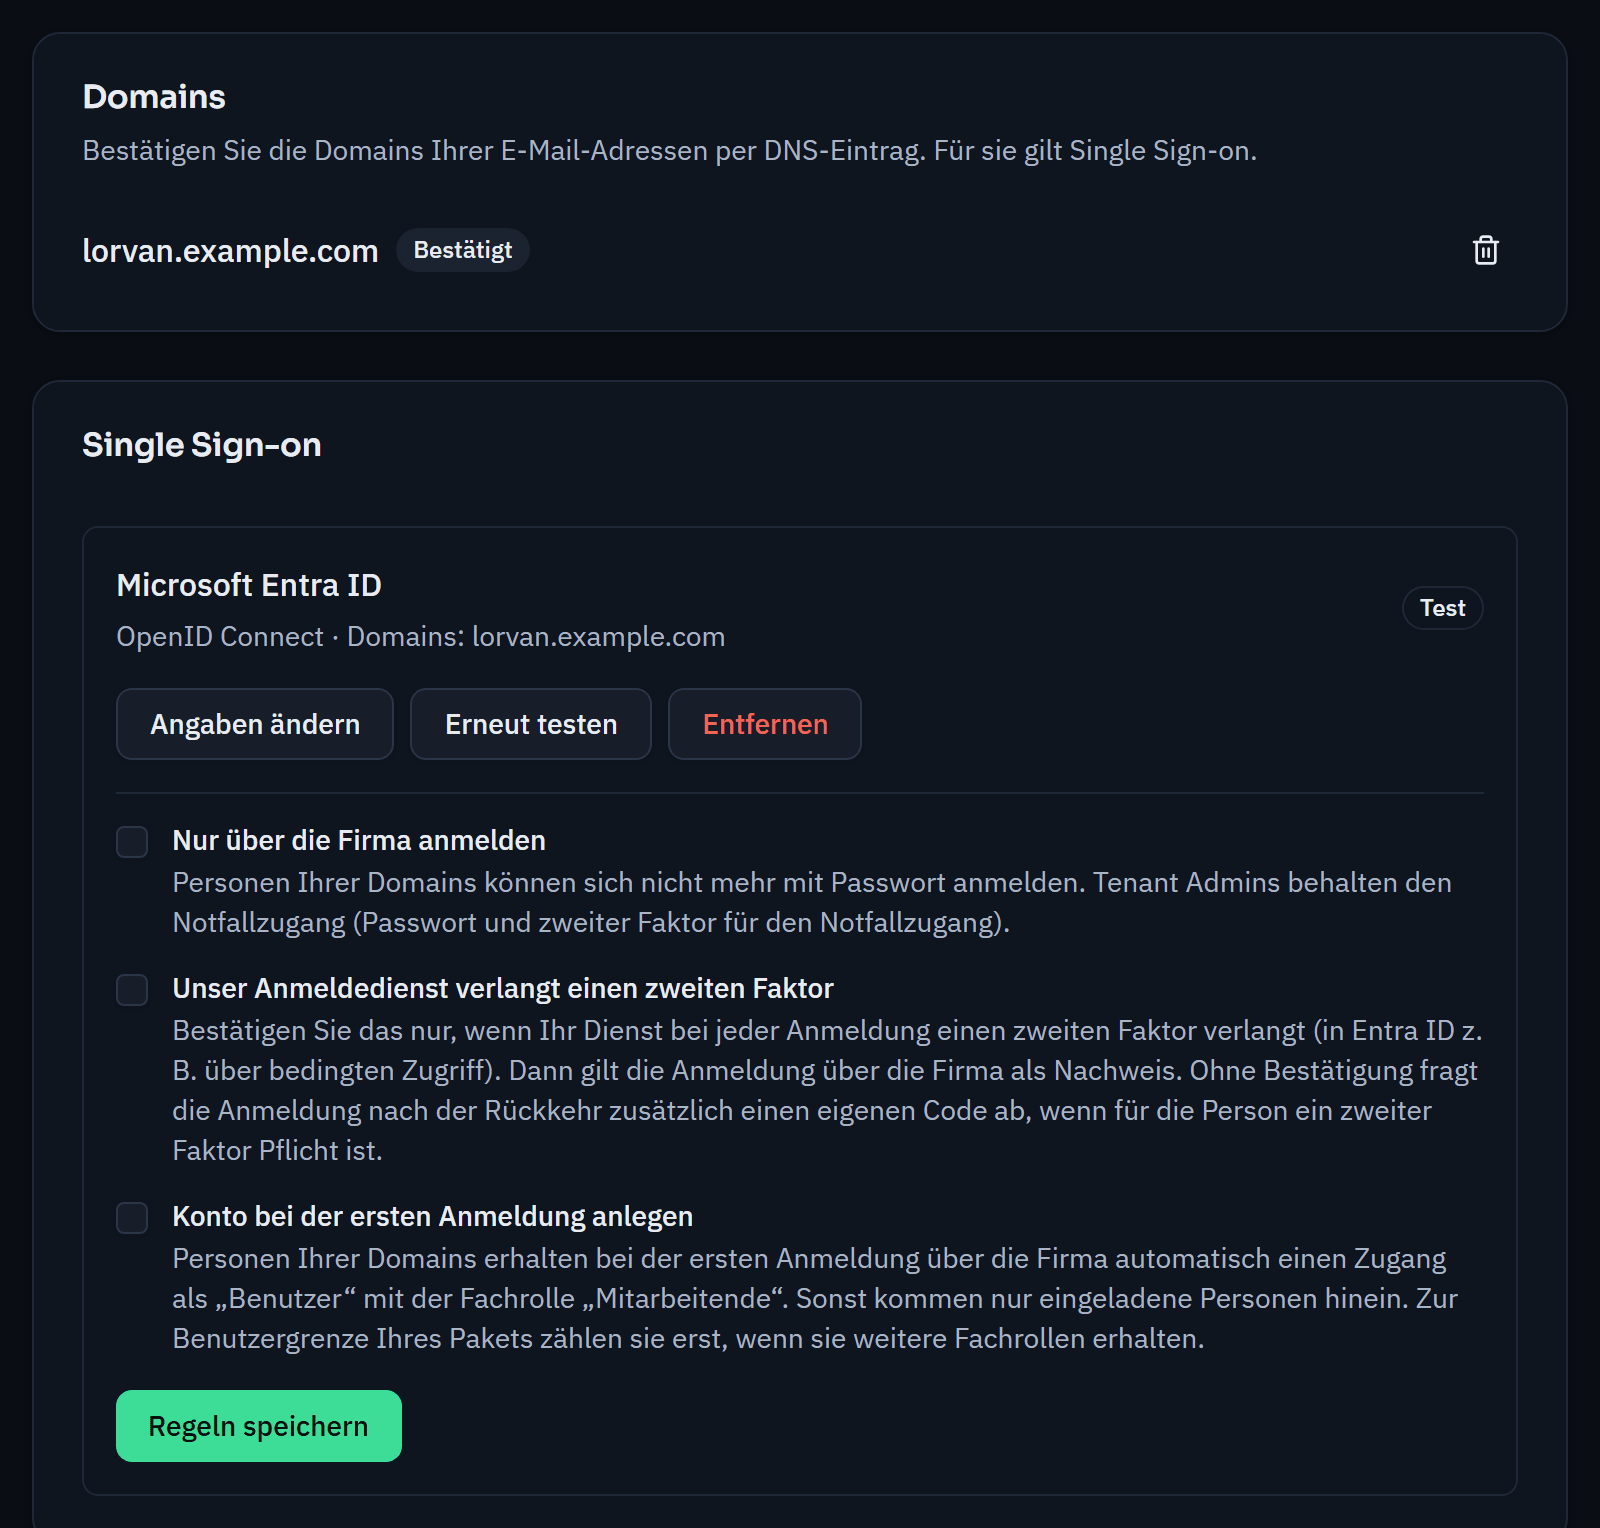
- Single sign-on through your company’s identity provider, e.g. Microsoft Entra ID, from the Pro plan.
- Lockout after repeated failed sign-in attempts.
- Maximum session length and sign-out after inactivity, configurable per account; access can be deactivated immediately or limited in time.
Traceability
Changes to data are recorded with the person, the time and the old and new value in an immutable log – not even we as the operator can change it afterwards. Your administrators see sign-ins and administrative actions in the administration log.
Transmission, files and operations
- Encrypted transmission (TLS), strict security headers and a Content Security Policy in the browser.
- All requests reach Varmo only through an upstream web application firewall. Sign-in runs through a dedicated sign-in service with lockout after failed attempts.
- A virus scanner checks every uploaded file before Varmo stores it. File lists show the note “scanned for malware”. Varmo rescans stored files with current signatures; a finding appears as a notification in your organisation.
- The server also checks type and size; file types that the browser would execute as a page are not permitted.
- Where the data is stored and the services involved: see data location.
- Regular backups of the database and files; retention 7 days (daily backup on the server and a daily copy of the data storage at the hosting provider, both in Switzerland).
- Error tracking on our own systems, without cookies, request content or personal details.
- Dependencies are checked automatically for known vulnerabilities.
Your data stays your data
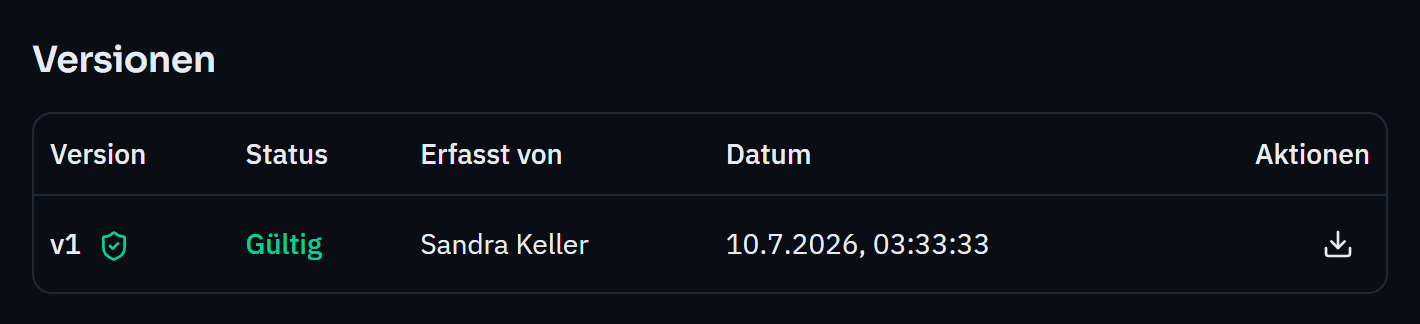
You can export the data of each organisation in full as a ZIP file at any time, including uploaded files. An export requires confirmation by your organisation’s ISMS manager; if there are several, the person who requested it never confirms it. After cancellation, all data is permanently deleted once the agreed deletion period has expired, including uploaded files. How we process personal data is set out in the privacy policy.
Found a vulnerability?
Please report it confidentially to info@varmo.ch and not publicly. We will confirm receipt and keep you informed about the fix.
Last updated: 27 October 2026