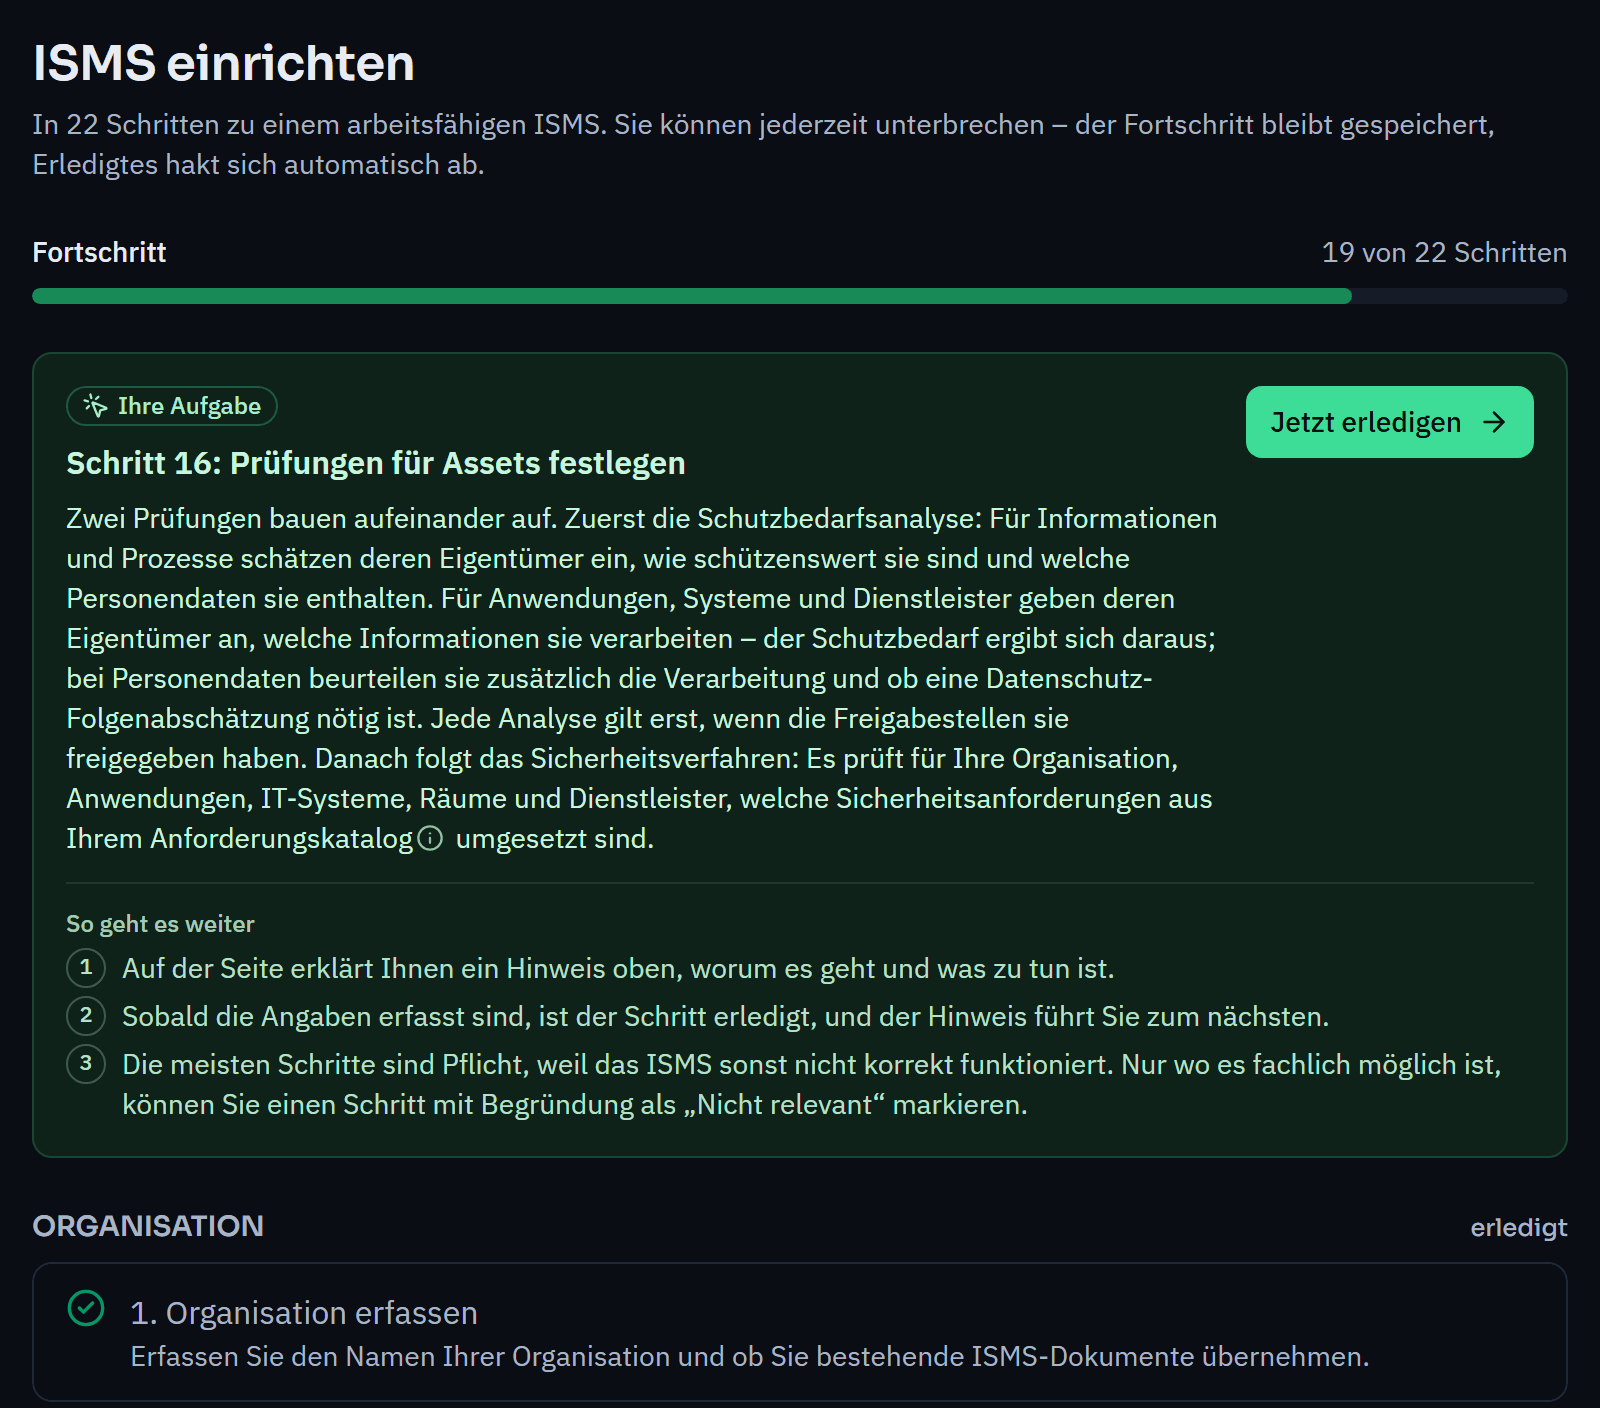
Guided setup & tasks
A setup assistant with 22 steps along ISO/IEC 27001, tasks for every person and “What happens next?” in every workflow.
Varmo supports the whole lifecycle of an ISMS under ISO/IEC 27001: build it, assess risks, implement, review and improve. The modules work hand in hand: a risk knows its asset, a measure its requirement, an exception its risk.
A setup assistant with 22 steps along ISO/IEC 27001, tasks for every person and “What happens next?” in every workflow.
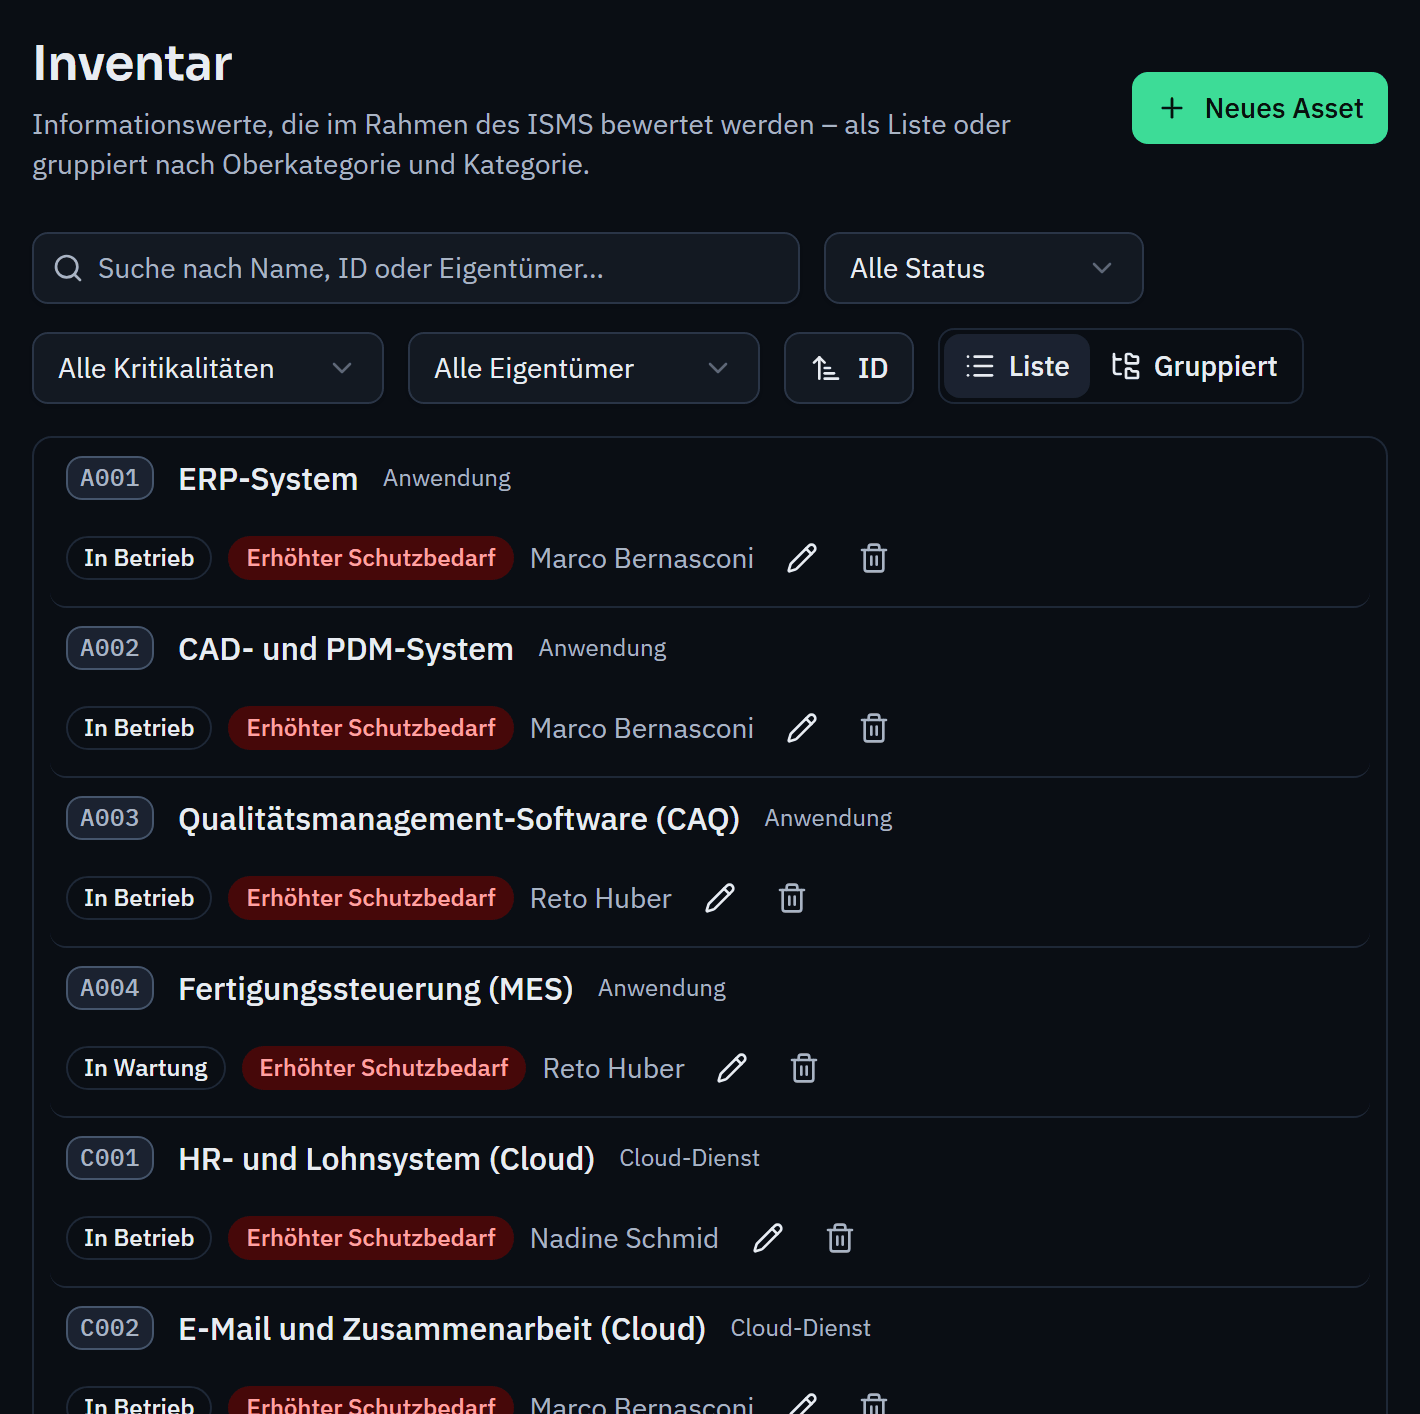
An inventory with owners, protection requirements analysis with approval and a baseline check per system that matches its protection requirements.
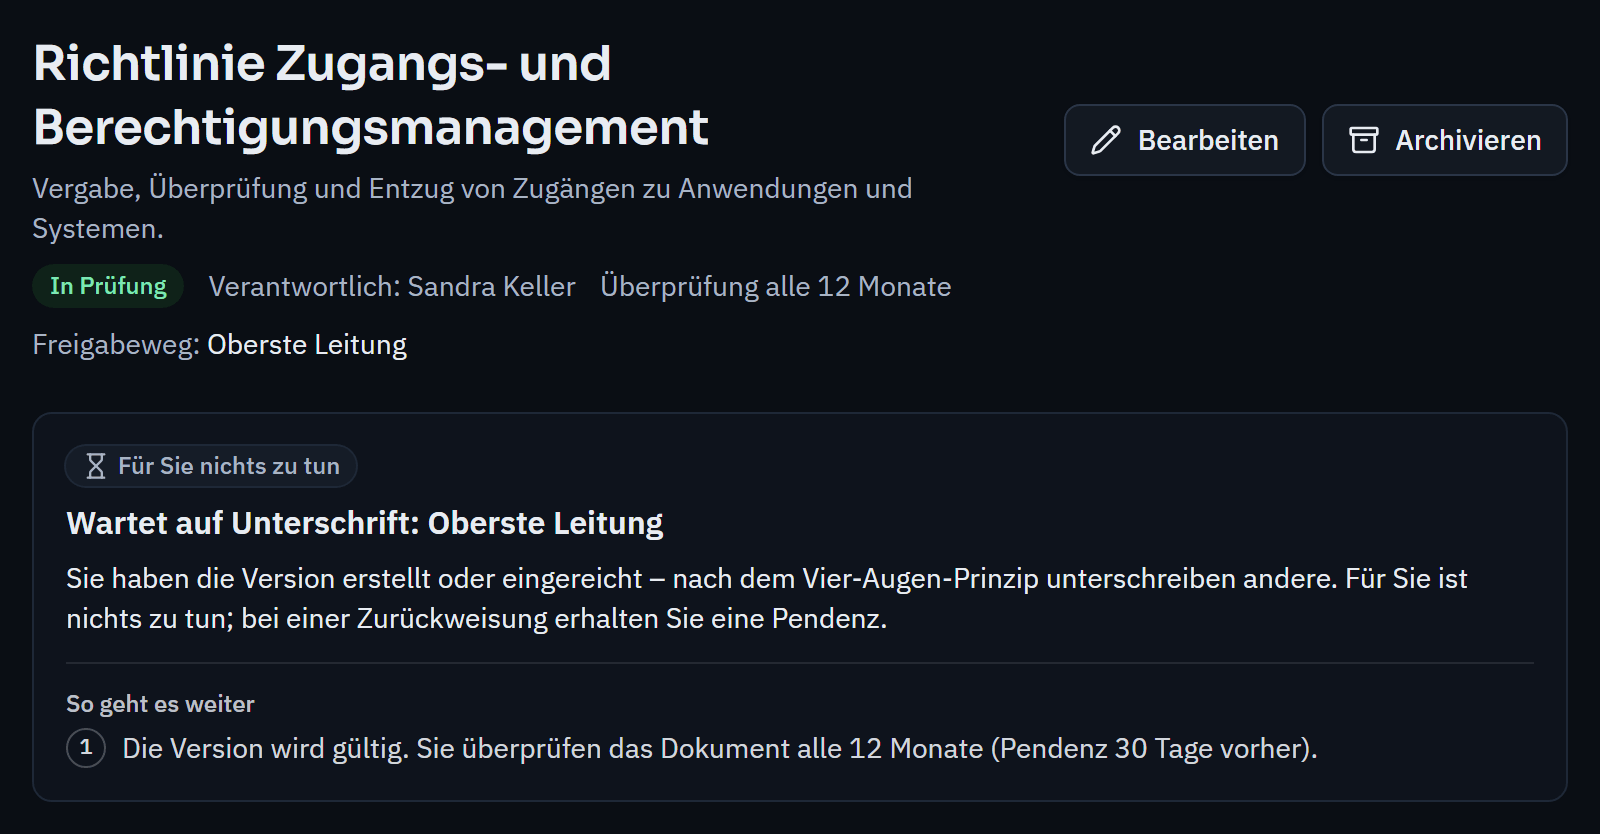
Policies with approval workflow, versions and acknowledgement; documents and evidence with versions and four-eyes approval.
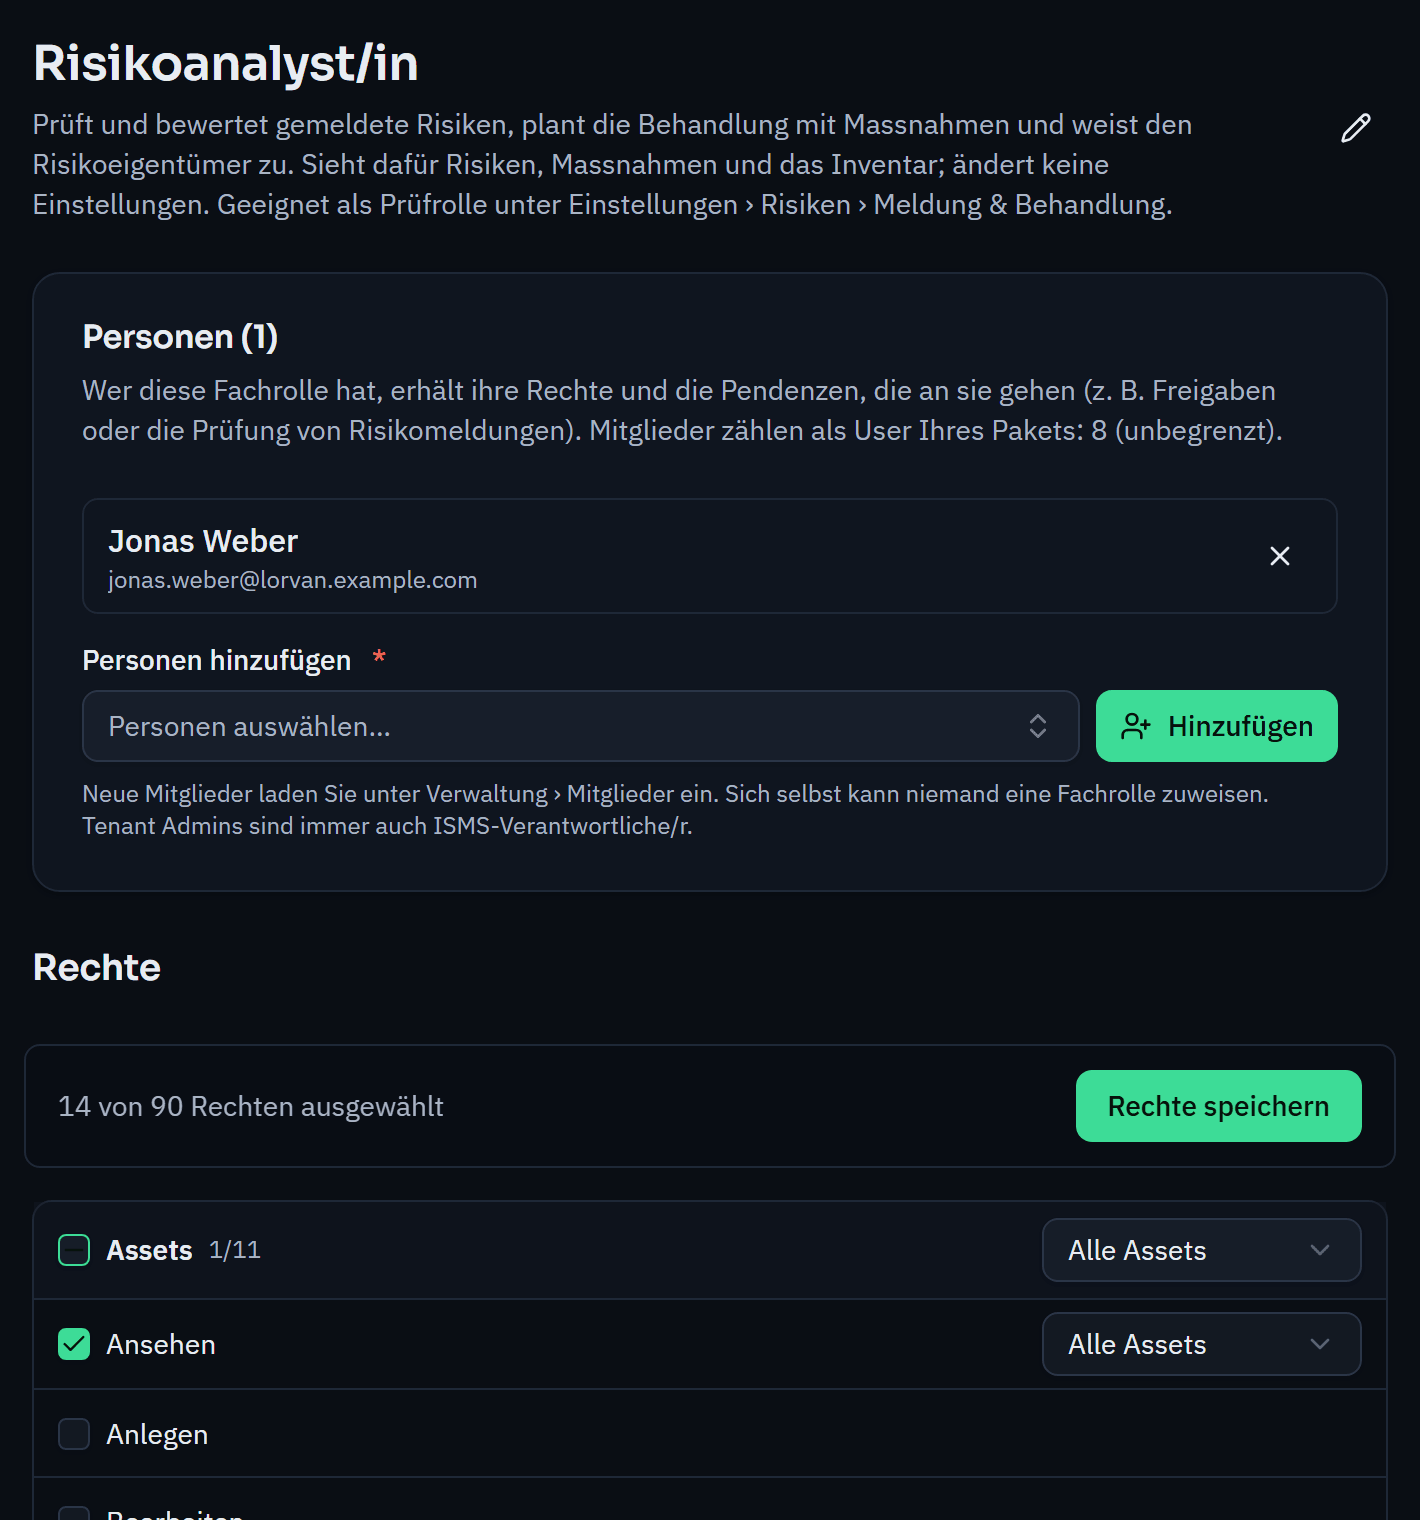
Functional roles with fine-grained permissions, four-eyes approvals without exception, segregation of duties and several organisations per account (from Pro).
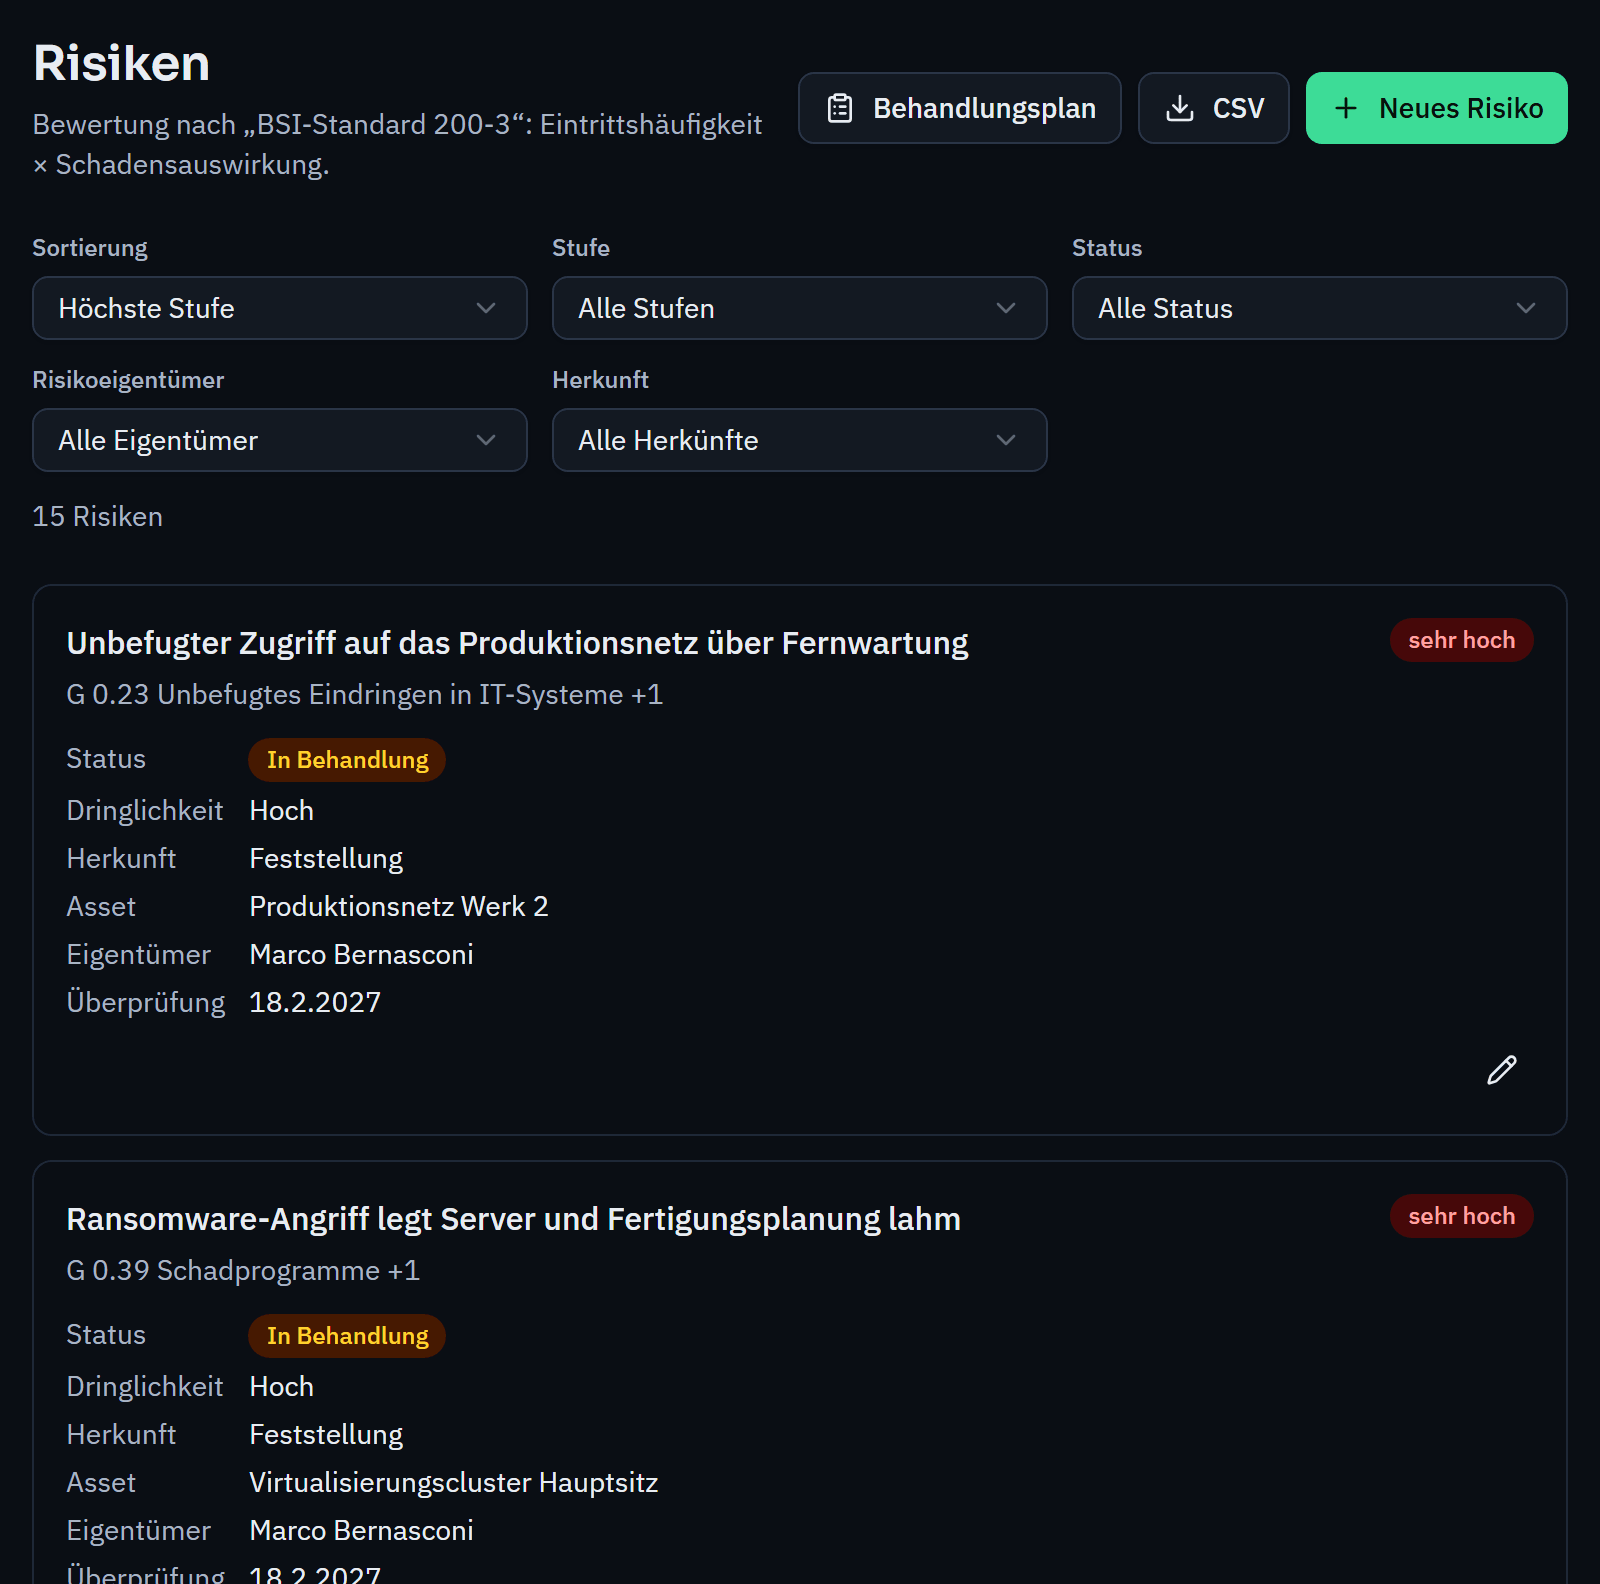
Report risks, assess them with your methodology, treat them and accept them against defined criteria, with a risk treatment plan.
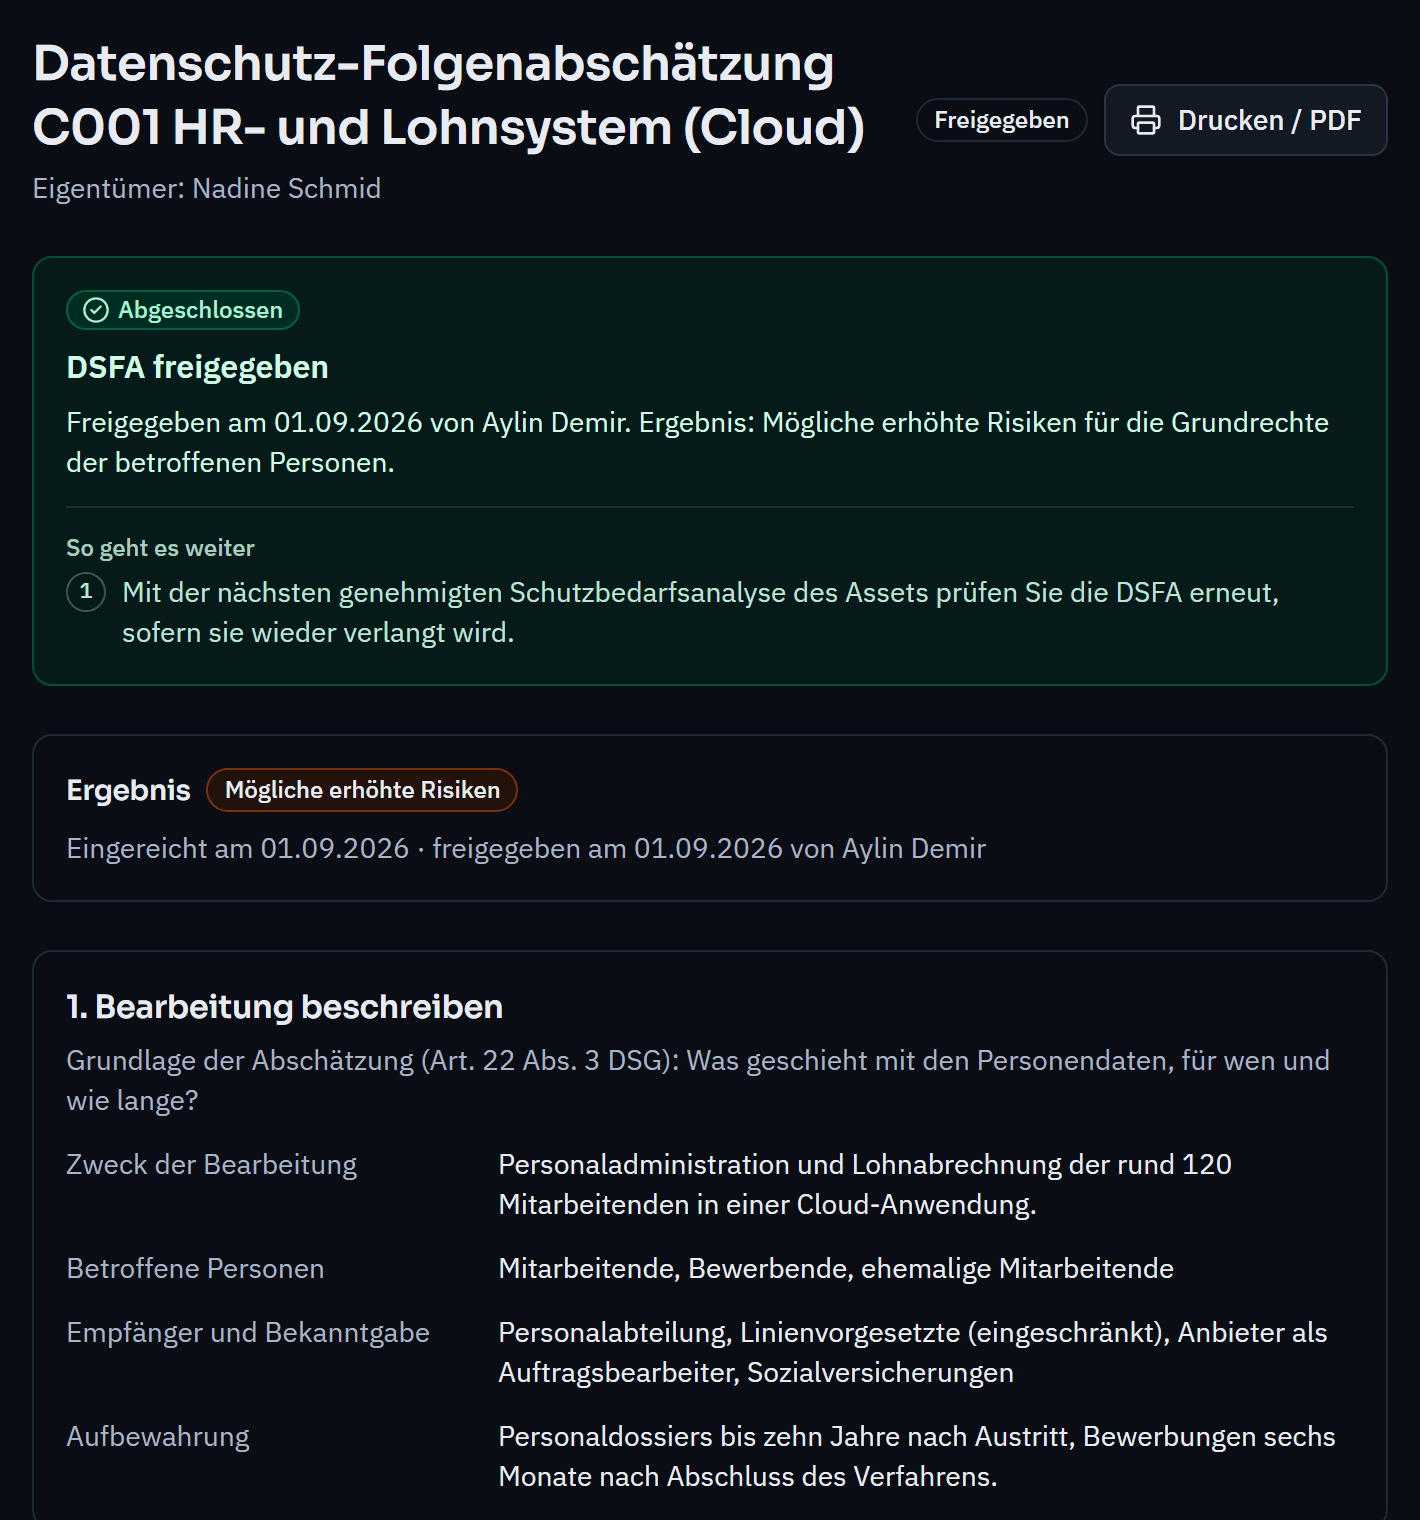
Record personal data per system, check whether a DPIA is required under the Swiss FADP and create the data protection impact assessment directly in Varmo.
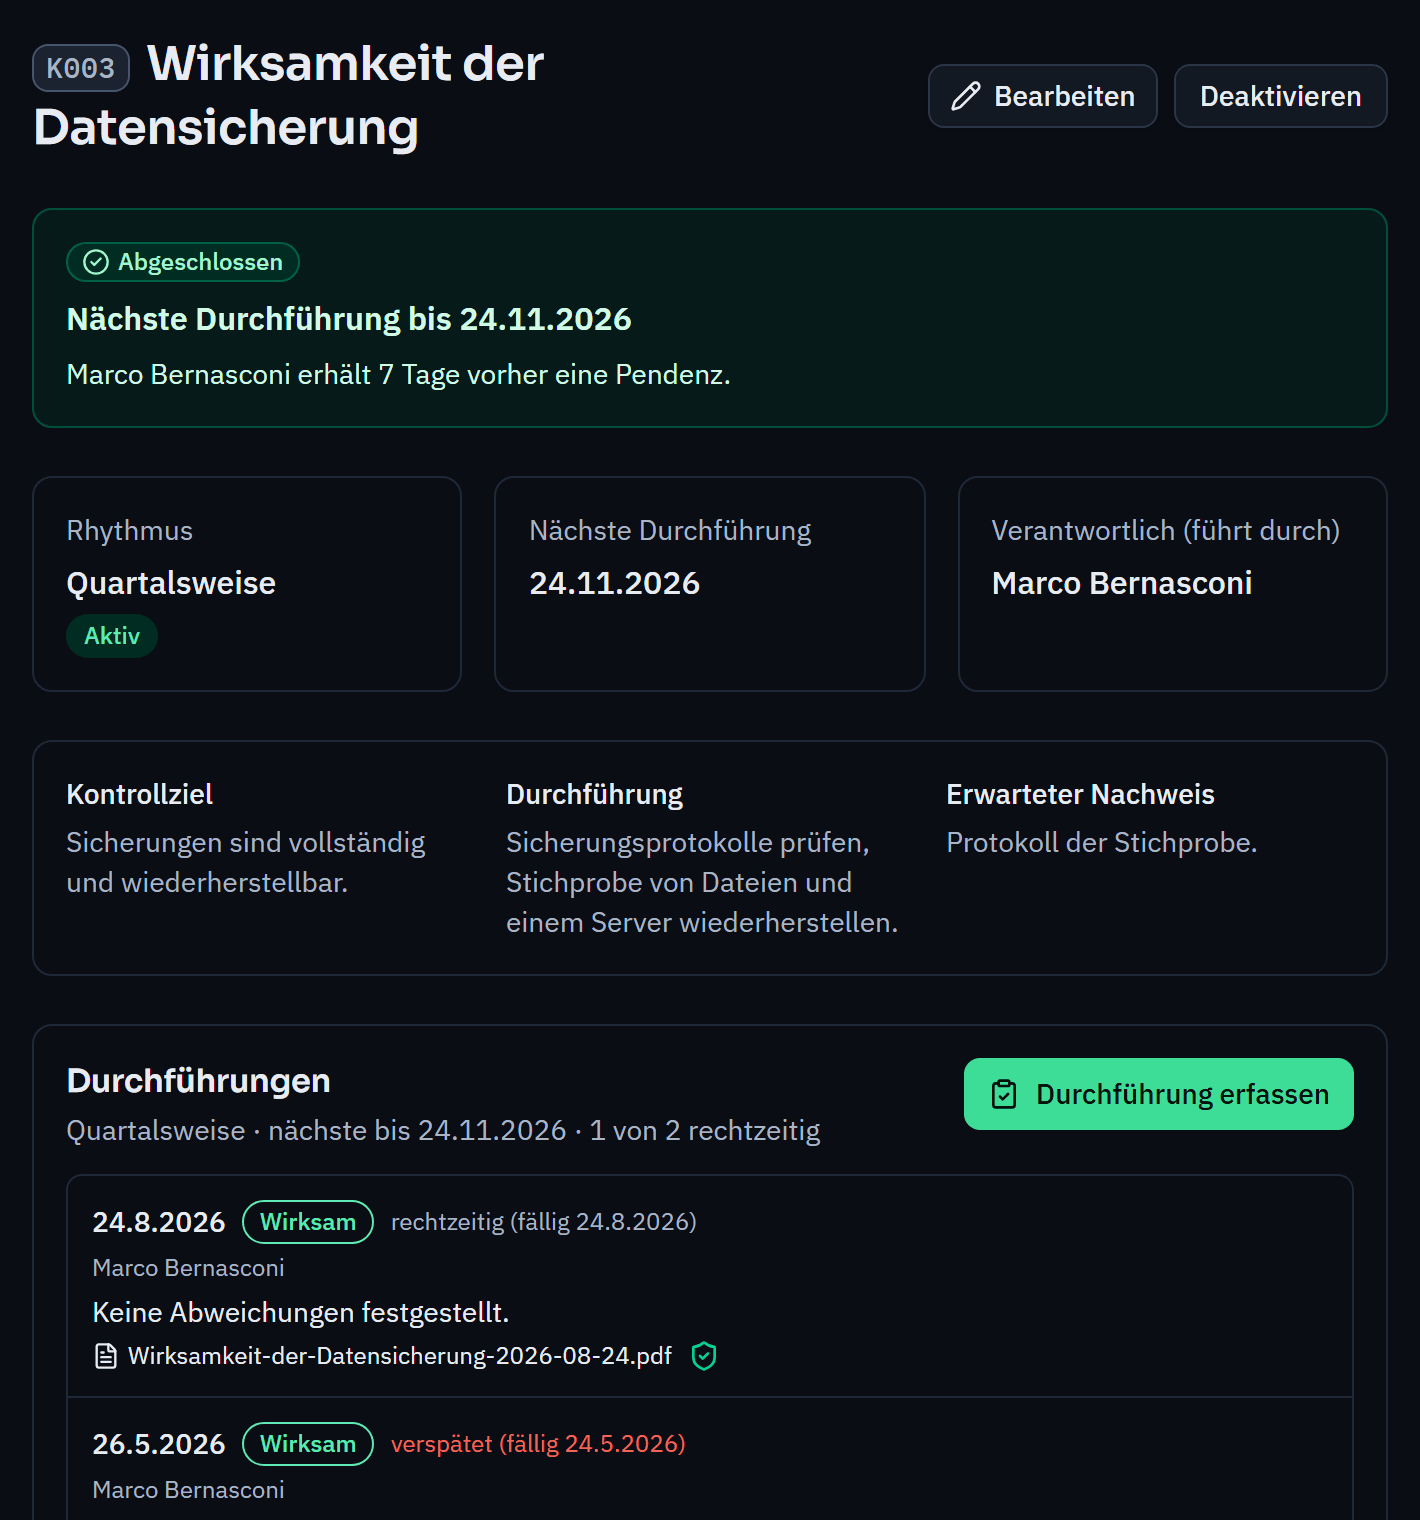
Implement measures, carry out recurring measures and internal controls with evidence, and approve time-limited exceptions through an approval workflow.
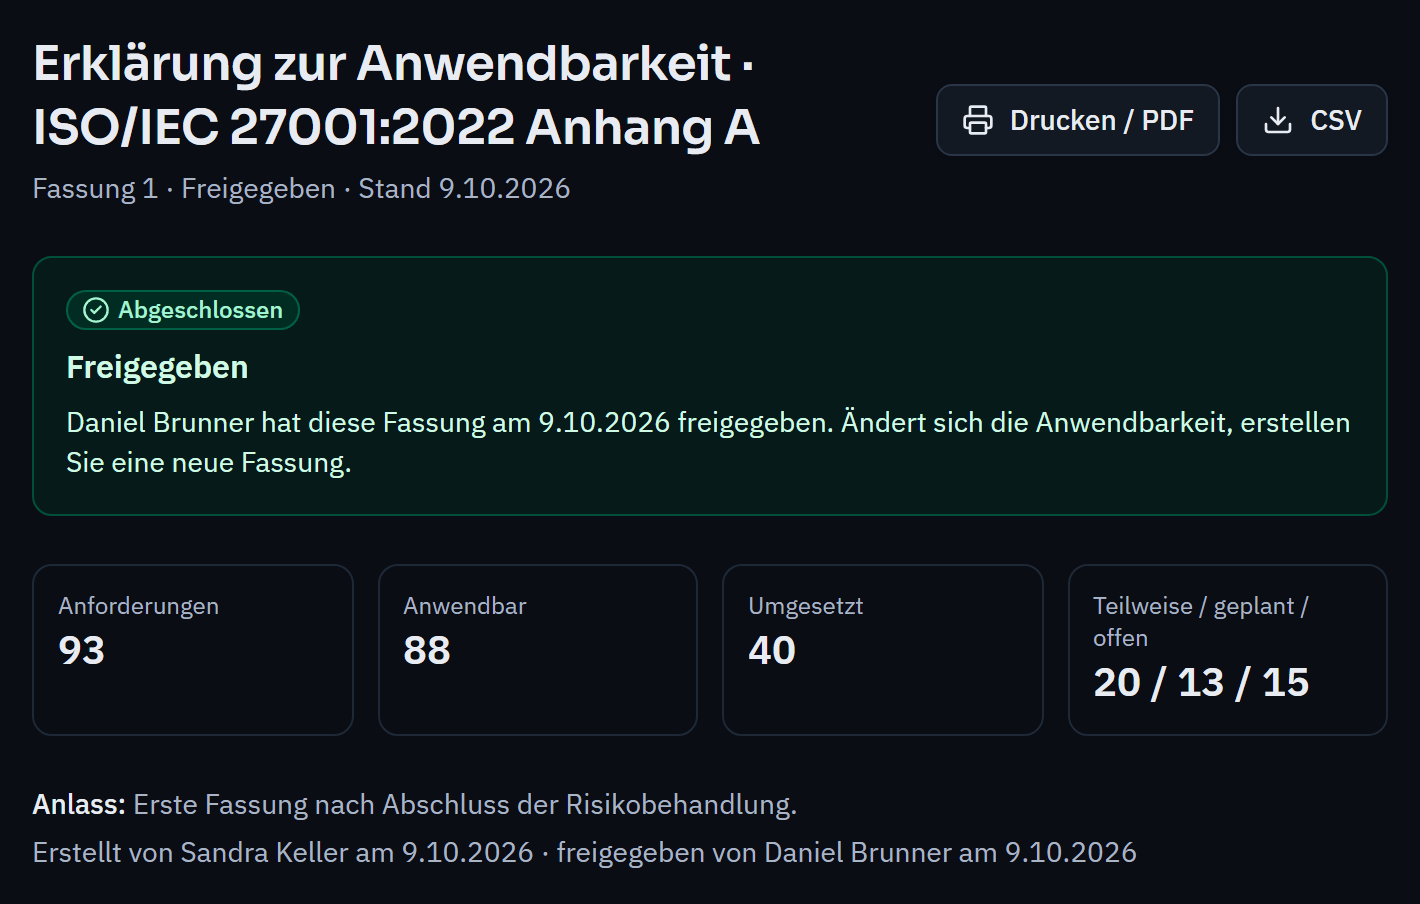
Adopt frameworks, justify applicability, evidence implementation and version your Statement of Applicability (SoA) with approval.
Custom catalogues in all plans · standard catalogues from Starter · cross-check and coverage from ProCalendar feed, evidence links, import from CSV, Jira and ServiceNow, Microsoft 365 (Entra ID, Teams, Intune), REST API and webhooks – each with a guide.
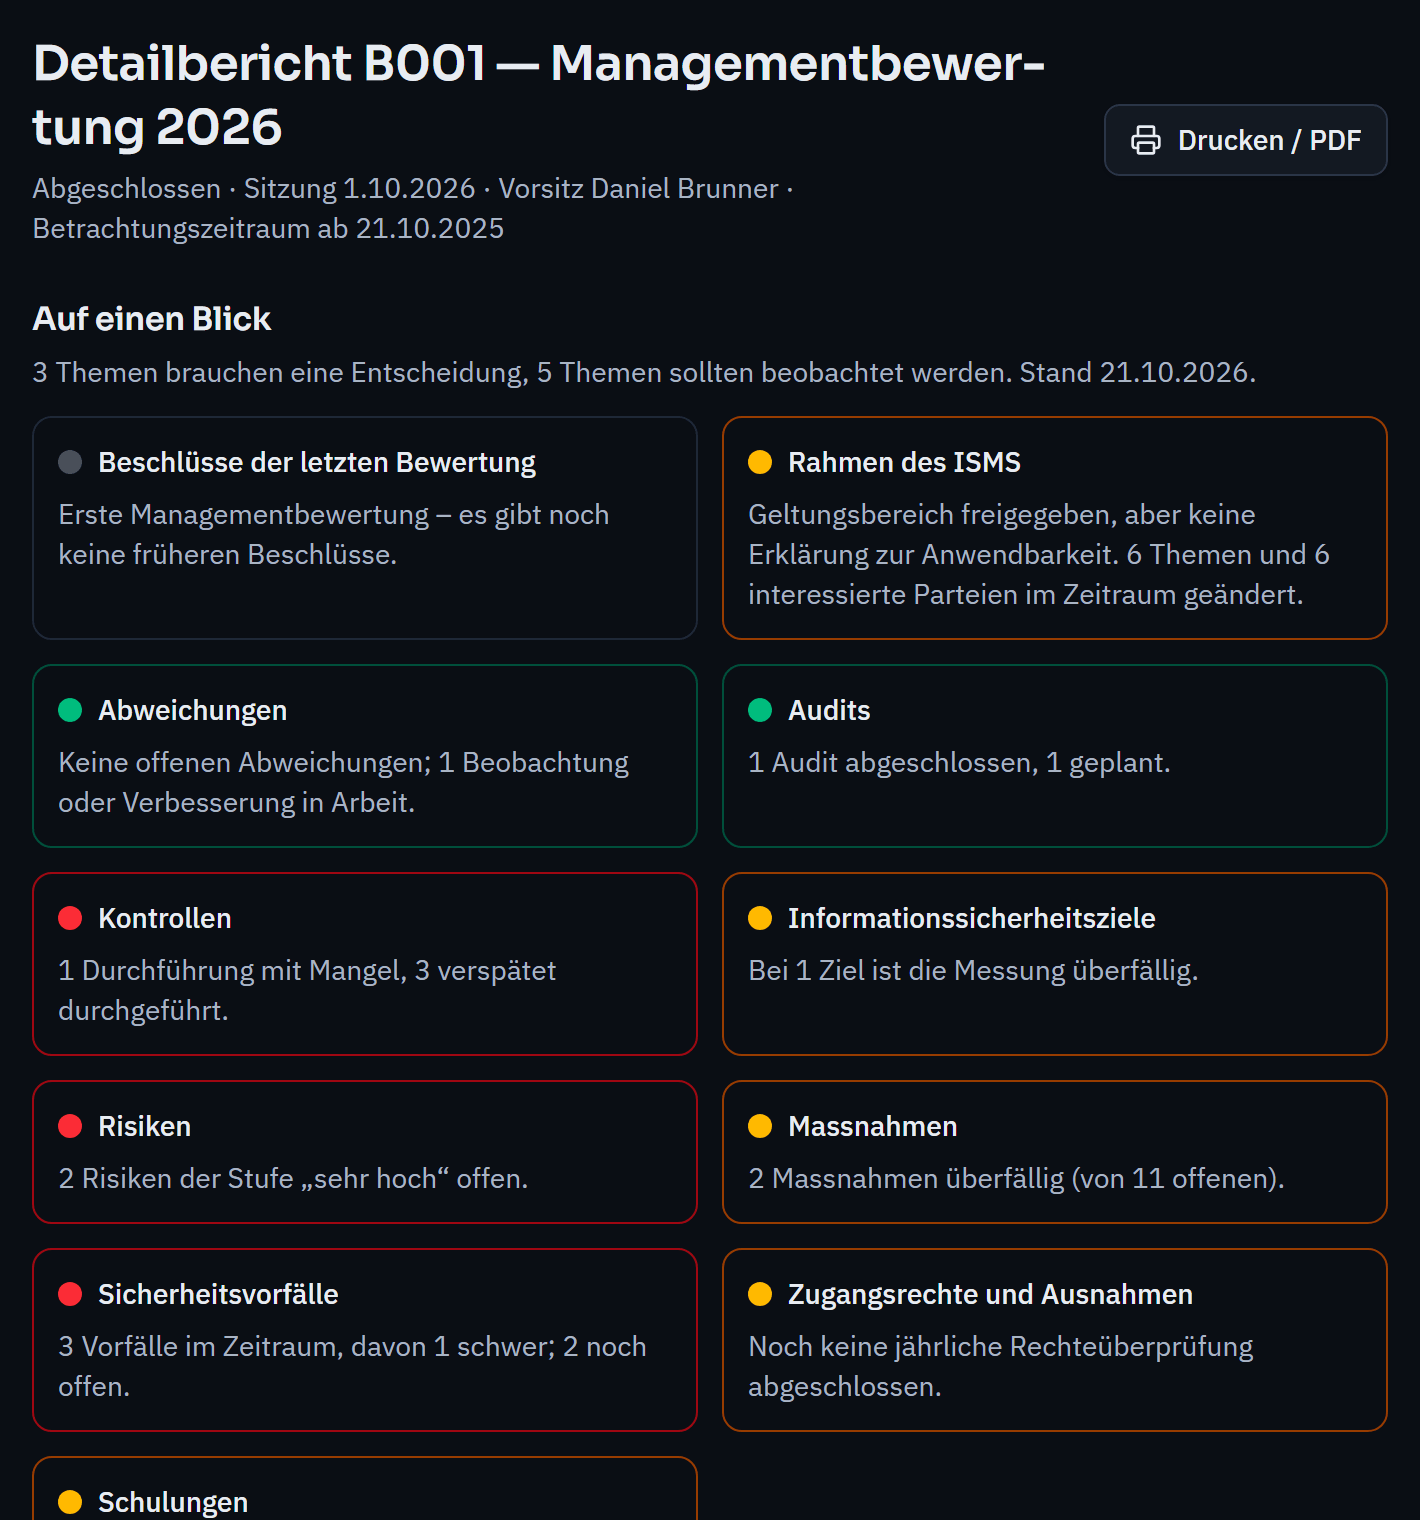
Context, objectives, training, internal audit, findings with effectiveness review and management review under ISO/IEC 27001 9.3.
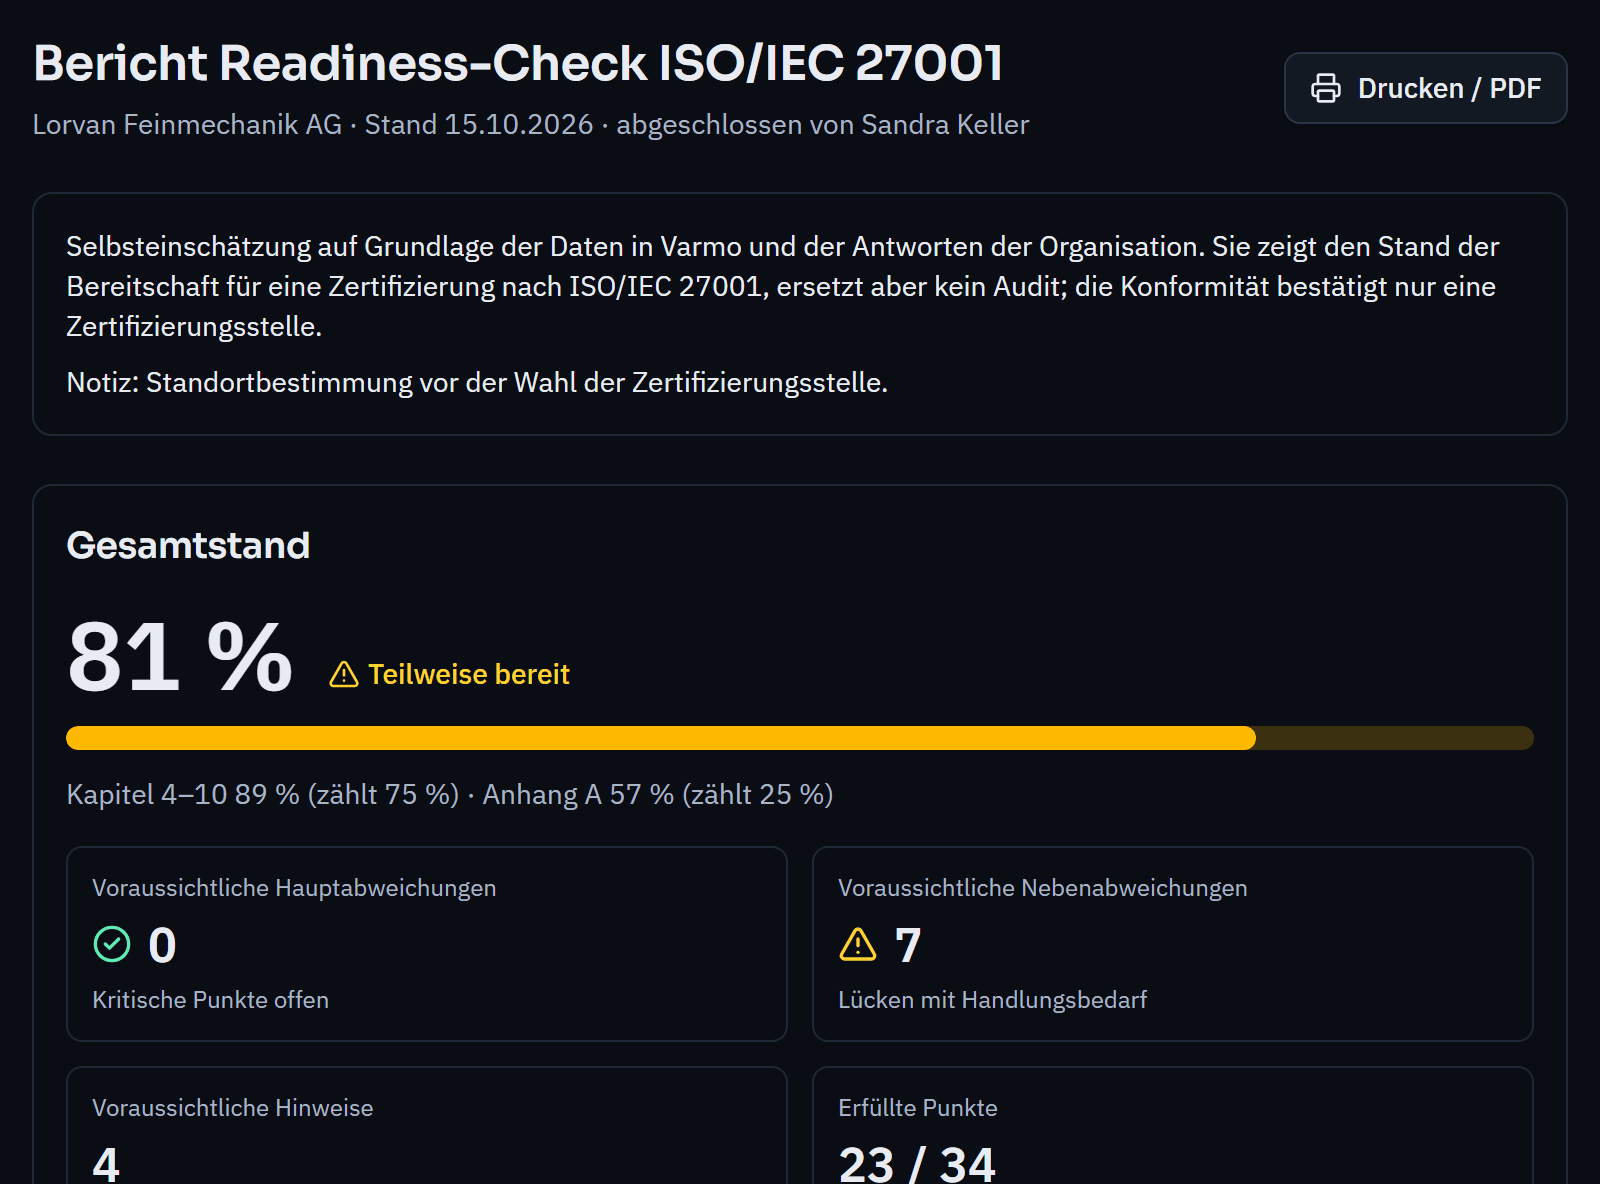
How close are you to certification? Checks clauses 4 to 10 and Annex A, with a traffic light per clause, likely findings and a report. From Starter.
Included from the Starter plan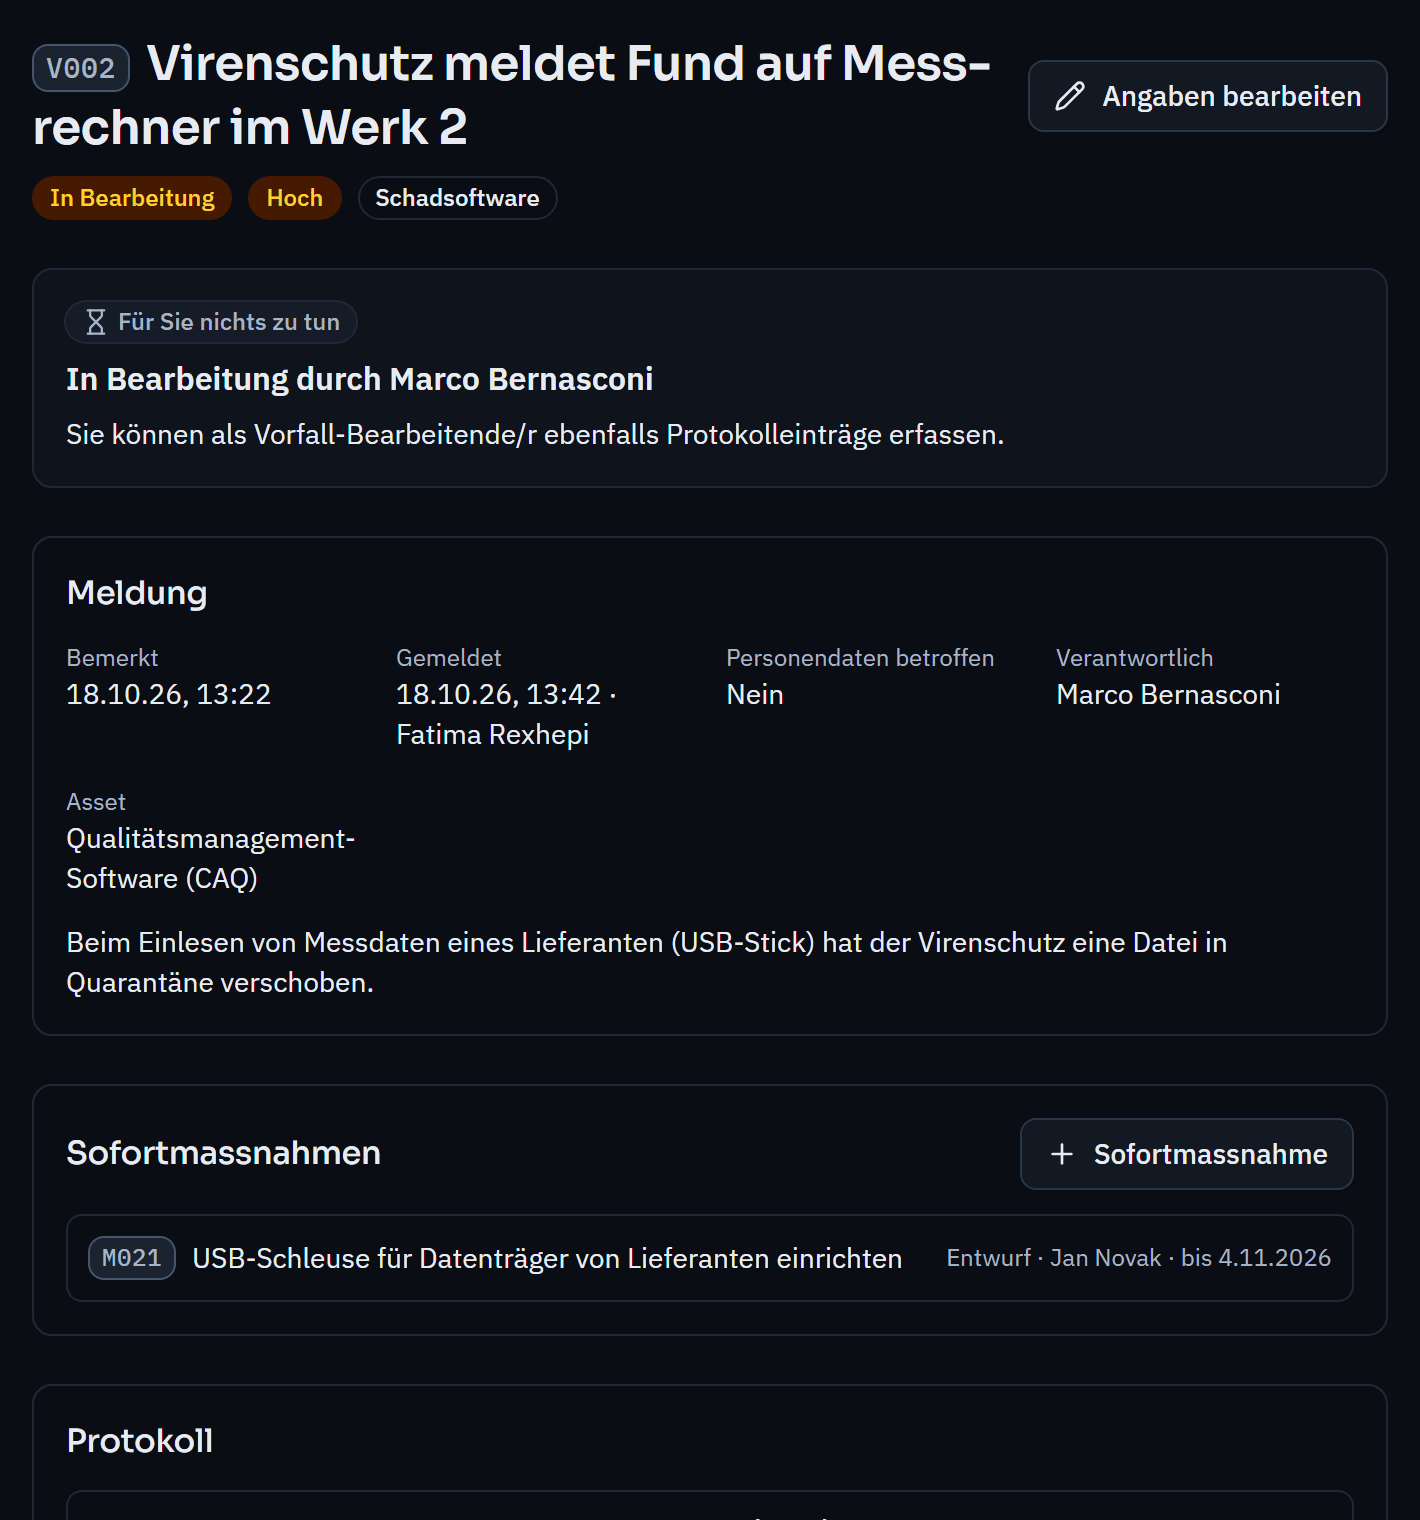
Report, assess, handle and follow up incidents, including the decision on the reporting obligation where personal data is involved.
Time-limited deviations with a linked risk, approval workflow and a reminder before they expire.
From Starter: take over risks, measures, exceptions, assets, findings and custom catalogues with a preview, conflicts and undo.
Lists as CSV, reports such as the SoA, treatment plan and management review printable as PDF.
From Pro: several organisations under one account, such as subsidiaries, sites or departments, with strictly separated data.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.