Requirements & SoA
How applicability, implementation and evidence fit together.
ISO/IEC 27001 defines what an information security management system has to achieve. Varmo maps the requirements for the management system in its modules and includes Annex A as a centrally maintained framework.
Annex A as a platform framework from the Starter plan
All 93 controls from Annex A, grouped into organisational, people, physical and technological controls. Each requirement comes with our own explanation of its meaning and implementation guidance with possible evidence.
The requirements for the management system itself are not a checklist to tick off, but processes. There are dedicated modules for them.
The SoA is built from applicability, justifications, implementation and evidence. Every version is frozen and approved under the four-eyes principle.
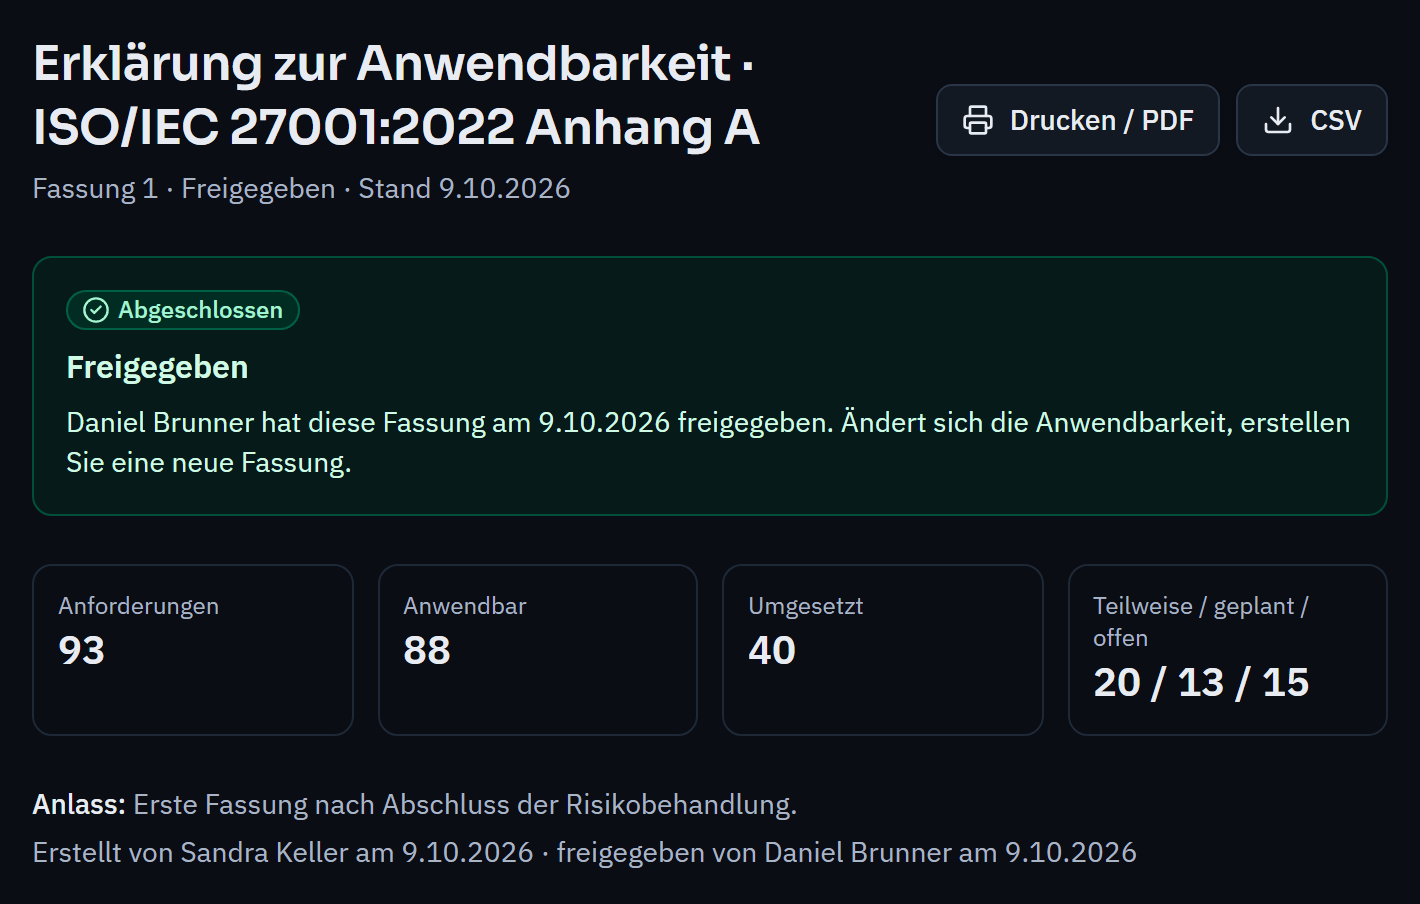
Mappings to NIST CSF 2.0, NIST SP 800-53 and NIS2 show where one implementation also covers requirements of other frameworks; equivalent or included requirements count as fulfilled. The coverage view compares frameworks by CSF function. Both are included from the Pro plan.
The ISO/IEC 27001 readiness check reviews clauses 4 to 10 including Annex A against your data and shows the gaps with a traffic light per chapter. It is a self-assessment and included from the Starter plan.
How applicability, implementation and evidence fit together.
How close you are to certification.
No. Number and short title correspond to the standard; explanations and implementation guidance are our own wording. For certification, you need the standard itself.
The framework covers ISO/IEC 27001:2022. The transition period for certificates under the 2013 version ended on 31 October 2025.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.