Public sector
Information security for municipalities, cantons and the Confederation.
Directive Si001 sets out the minimum requirements of the baseline protection security level under the Information Security Act (ISA) for the Confederation’s IT resources. Varmo includes it as a framework and applies it per system in the security procedure.
Platform framework from the Pro plan
64 requirements from chapter 4 of the directive, grouped into organisation, personnel, technology, information, IT systems, clients, peripherals, applications and zones.
Organisation, personnel, technology and information apply to every protection object, the other chapters only to matching systems. For each asset category, Varmo suggests the chapters based on its position in the dependency chain; you confirm or adjust them. The owner answers the requirements and evidences the implementation.
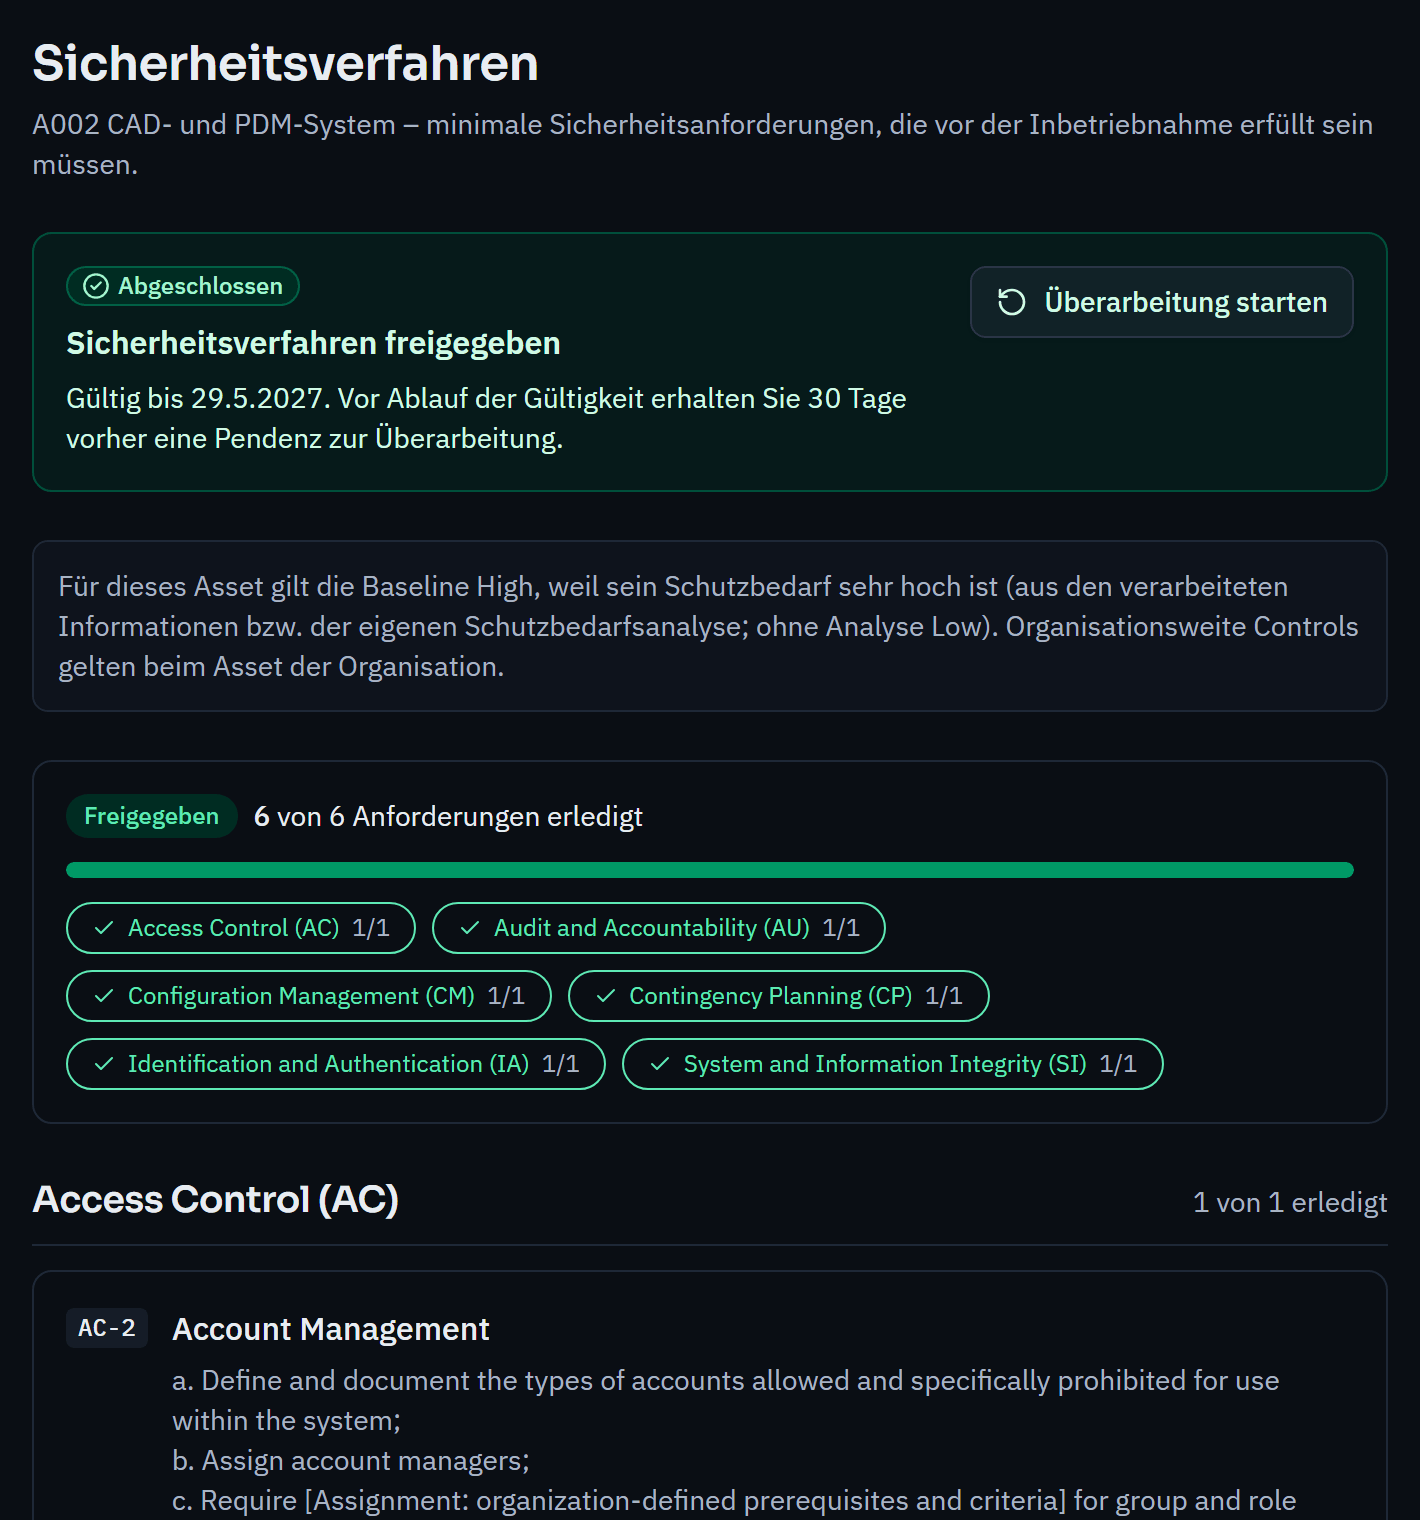
External service providers that operate IT resources for the Confederation must also implement the requirements that apply to them. Other organisations use ICT baseline protection as a concrete minimum per system; requirements that only concern the Confederation’s networks are set to not applicable with a justification.
ICT baseline protection is mapped to ISO/IEC 27001 Annex A, NIST CSF 2.0 and NIS2. This shows where one implementation also covers requirements of the other frameworks, and the coverage view shows it by CSF function. Mappings and coverage are included from the Pro plan.
Information security for municipalities, cantons and the Confederation.
Protection requirements analysis and security procedures in detail.
No. ICT baseline protection (directive Si001) is the mandatory requirement for the IT resources of the Federal Administration. The ICT Minimum Standard is a voluntary recommendation of the Confederation for critical infrastructure and measures the maturity of the whole organisation. Varmo includes both.
No. It sets technical and organisational minimum requirements per system. Leadership, risk management, audits and improvement are governed by a management system; Varmo has dedicated modules for them.
ICT baseline protection covers the baseline protection security level. For elevated protection requirements, the Confederation additionally requires a risk analysis and a security concept; in Varmo, the risk analysis follows, optionally to BSI Standard 200-3.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.