Financial services
FINMA, DORA and reporting obligations in one ISMS.
FINMA Circular 2023/1 requires banks and securities firms to manage operational risks, ICT and cyber risks, critical data and operational resilience. Varmo includes it as a framework, split so that each obligation can be evidenced on its own.
Platform framework from the Pro plan
100 requirements from the margin numbers on operational risks, ICT and cyber risks, critical data, business continuity management and operational resilience. Margin numbers that combine organisation-level and system-level obligations are split into sub-requirements.
You evidence the obligations of the board of directors and executive board, strategy, testing programme and reports once for the whole organisation. Access, hardening, vulnerabilities, logging and backup are checked by the owner of each system, and contractual obligations per service provider. Varmo suggests the relevant chapters for each asset category.
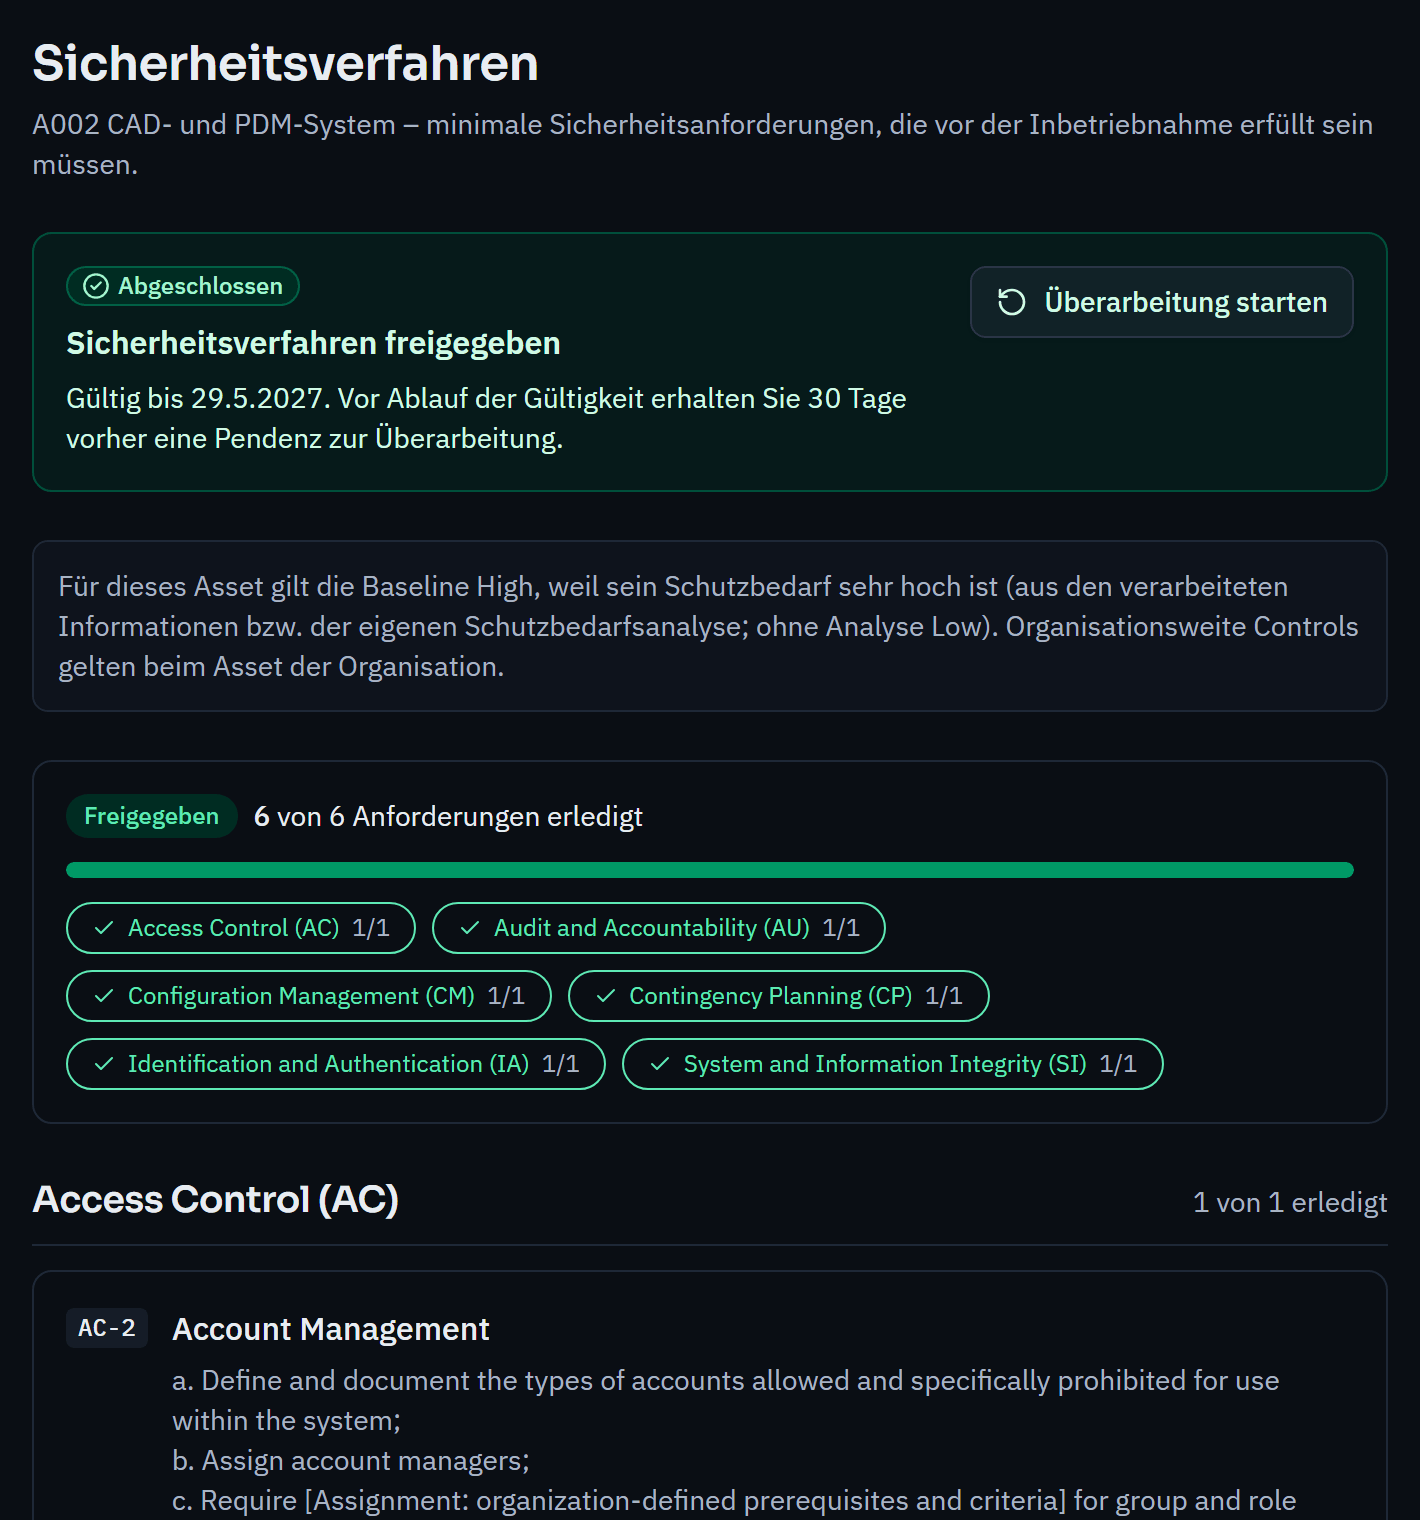
For cyberattacks on critical functions, FINMA requires an initial notification within 24 hours and a report via its survey and application platform within 72 hours. Once you specify the reporting obligation for your organisation, the responsible person decides for each incident and receives tasks with the deadlines.
The circular is mapped to NIST CSF 2.0, ISO/IEC 27001 Annex A and DORA. This shows where an existing implementation already applies, for example for groups operating in both Switzerland and the EU. Mappings and coverage are included from the Pro plan.
FINMA, DORA and reporting obligations in one ISMS.
Digital operational resilience in the EU.
Banks and securities firms in Switzerland, graduated by supervisory category. IT service providers of banks are affected indirectly through contracts and audits. Varmo helps with implementation but does not replace the audit by the audit firm.
No. Reports are submitted through FINMA’s channels. In the incident, you record deadlines, time and reference of every report.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.