ISO/IEC 27001 readiness check
Know your gaps before the certification audit.
Context, objectives, training, internal audits, findings and the management review work hand in hand. Management sees at a glance where the ISMS stands and what needs attention.
Internal and external issues with their impact on the ISMS, interested parties with their requirements and an approved scope. Whether climate change is a relevant issue is assessed with a justification, as ISO/IEC 27001:2022/Amd 1:2024 requires.
Information security objectives with a key figure, baseline and target value, measurement interval and due date. Training with a target group, mandatory participation and evidence; the participation rate appears on the dashboard.
Plan internal and external audits with scope, criteria and period. The lead auditor confirms their independence, and the audit report is filed as a PDF.
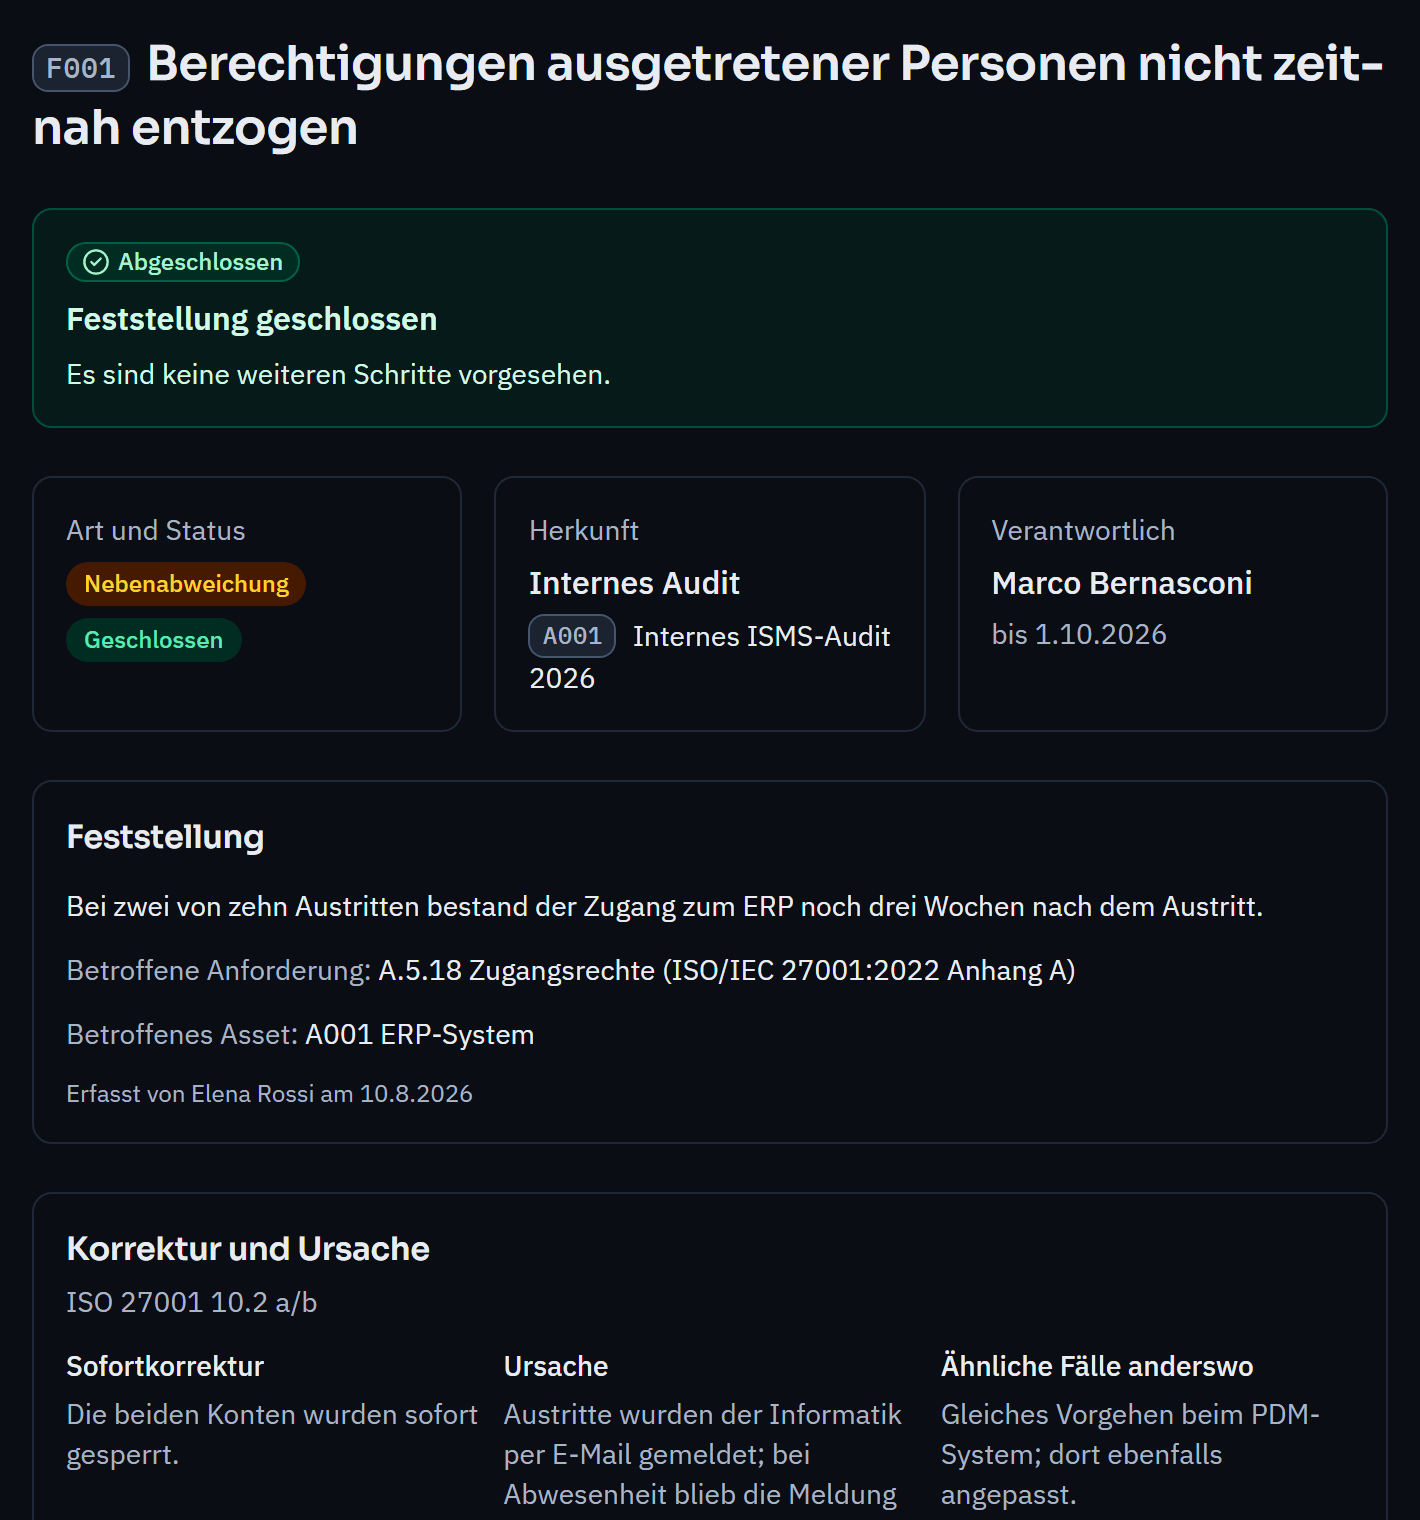
Nonconformities, observations and opportunities for improvement from audits, incidents and internal controls in one register. The cause, corrective actions and effectiveness are reviewed, by someone other than the responsible person.
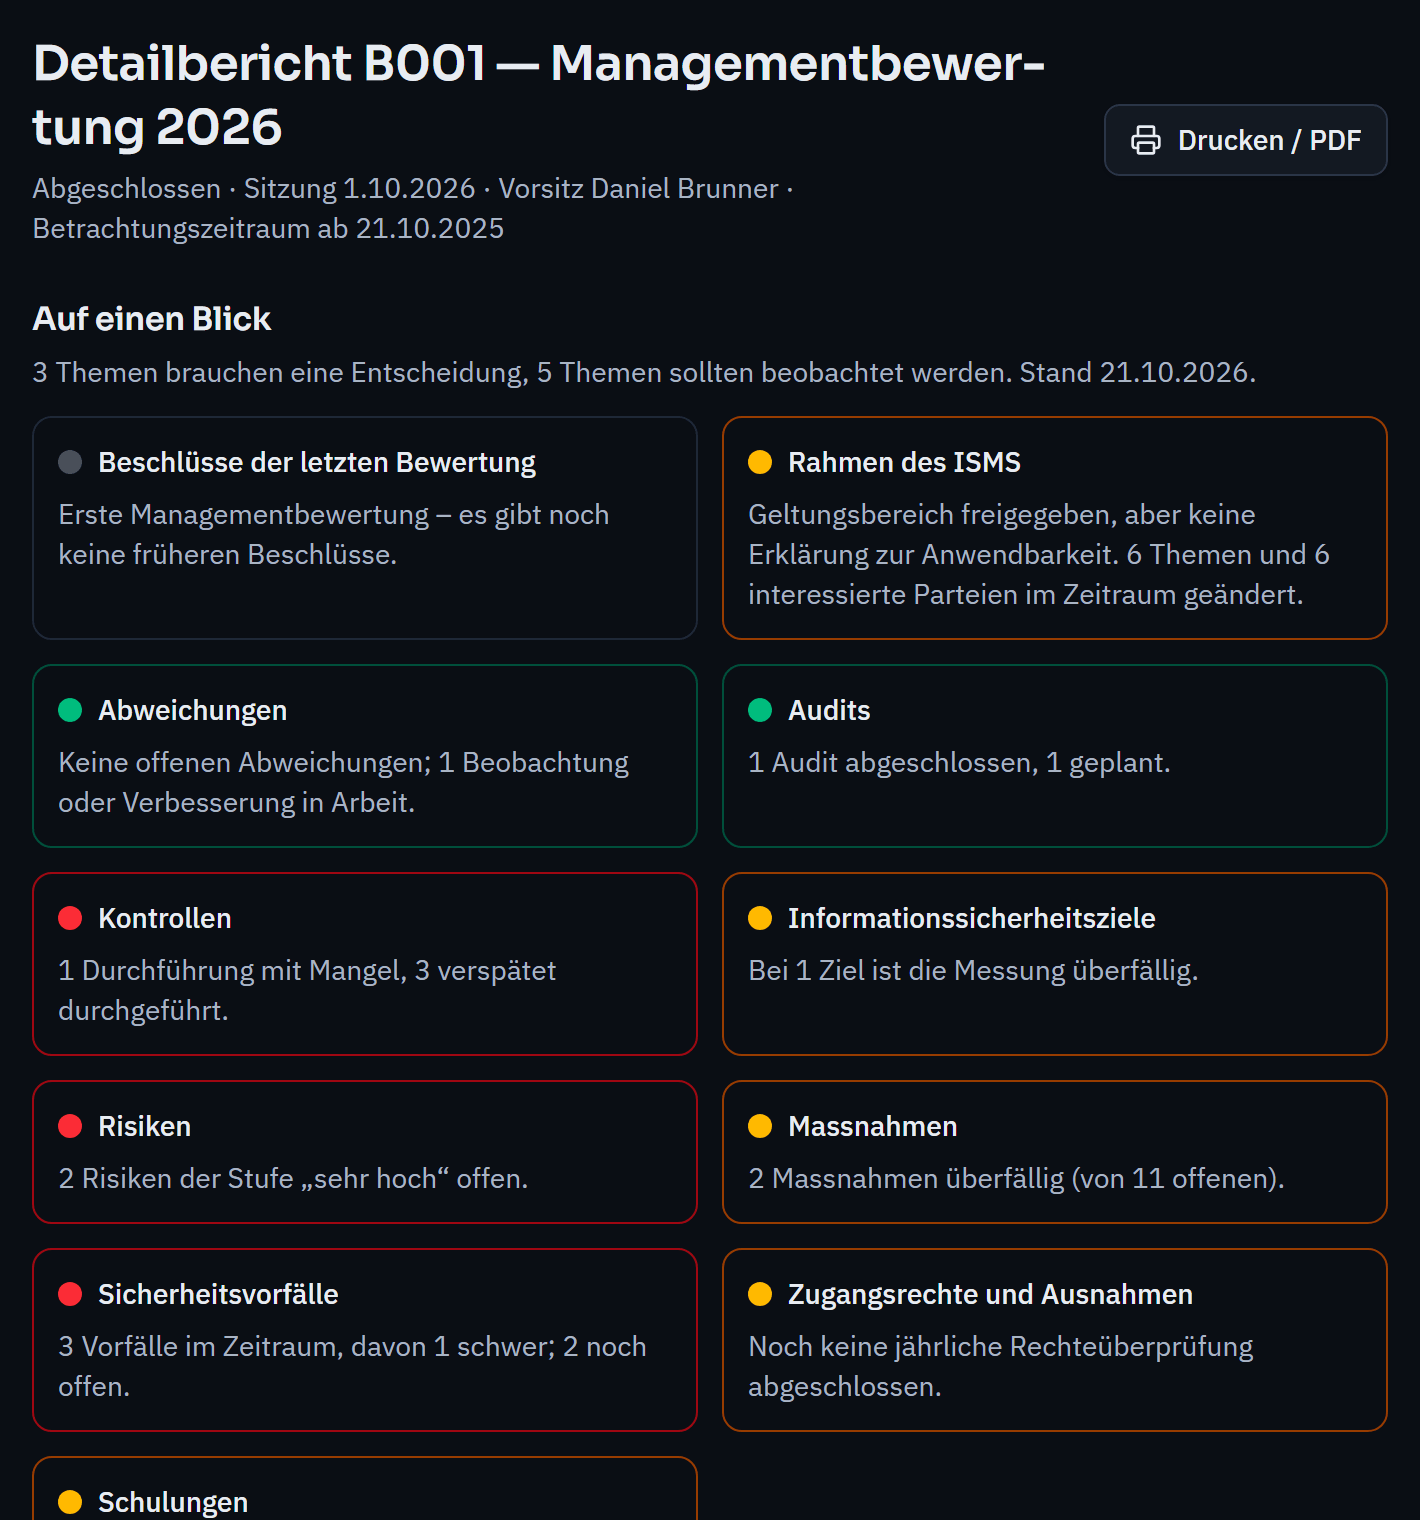
The inputs under ISO/IEC 27001 9.3 are compiled from the system and frozen: findings, audits, risks, objectives, incidents, exceptions, context and more. Management receives an overview with a traffic light per topic.
Know your gaps before the certification audit.
Lessons learned from incidents as findings.
A person who confirms their independence from the area being audited. Varmo records the declaration of independence; the “Internal audit” role can read everything but change nothing.
ISO/IEC 27001 requires it at planned intervals, in practice usually once a year. Varmo compiles the inputs as of the reference date and freezes them so that the report remains traceable.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.