Financial services
FINMA, DORA and reporting obligations in one ISMS.
Regulation (EU) 2022/2554 (Digital Operational Resilience Act) has applied to financial entities in the EU since 17 January 2025. Varmo includes its obligations as a framework, split so that each obligation can be evidenced on its own.
Platform framework from the Pro plan
ICT risk management (Art. 5–16), management, classification and reporting of ICT-related incidents (Art. 17–23), digital operational resilience testing (Art. 24–27), ICT third-party risk (Art. 28–30) and information sharing (Art. 45). Paragraphs containing several obligations are split into sub-requirements.
Obligations of the management body, strategy, incident management and testing programme apply to the organisation. Protection, detection and backup are checked by the owner of each system, and contractual provisions under Art. 30 per ICT service provider. Varmo suggests the relevant chapters for each asset category.
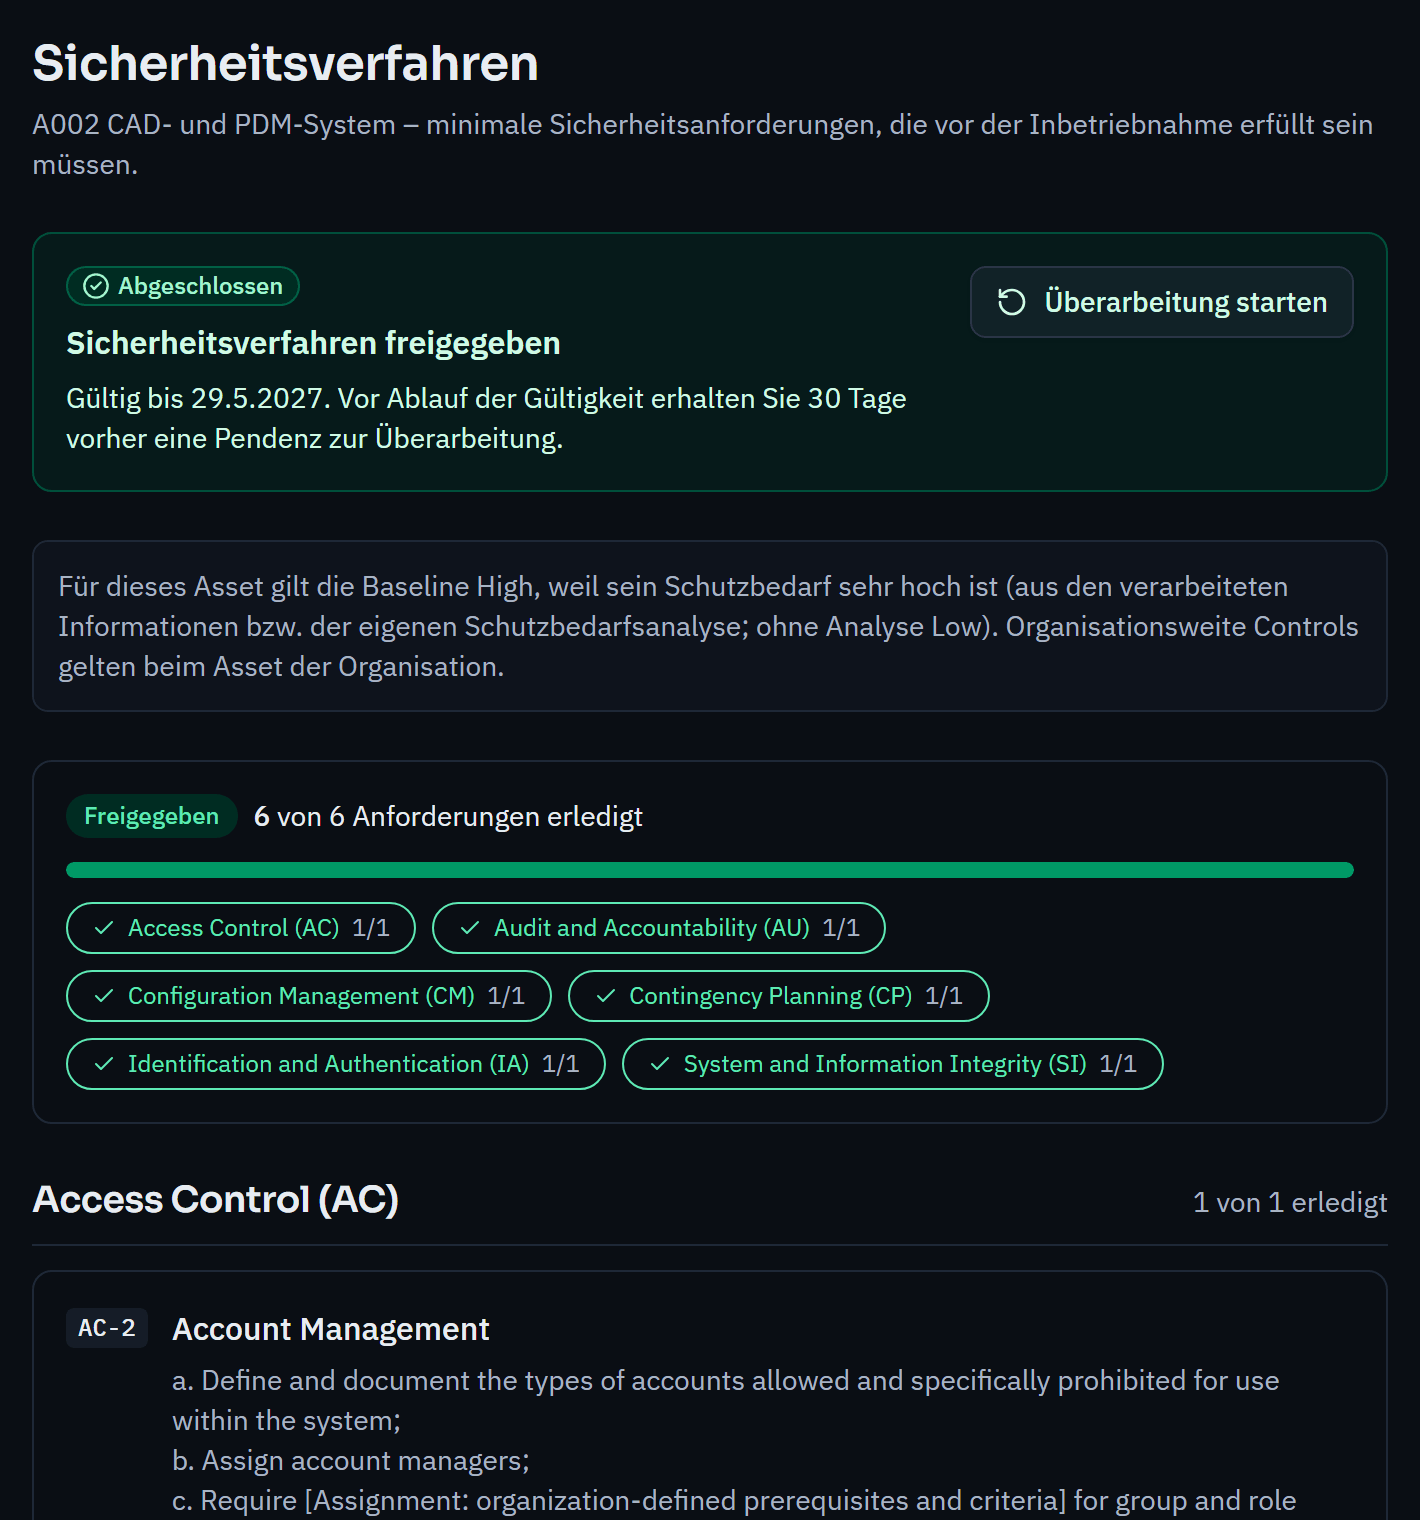
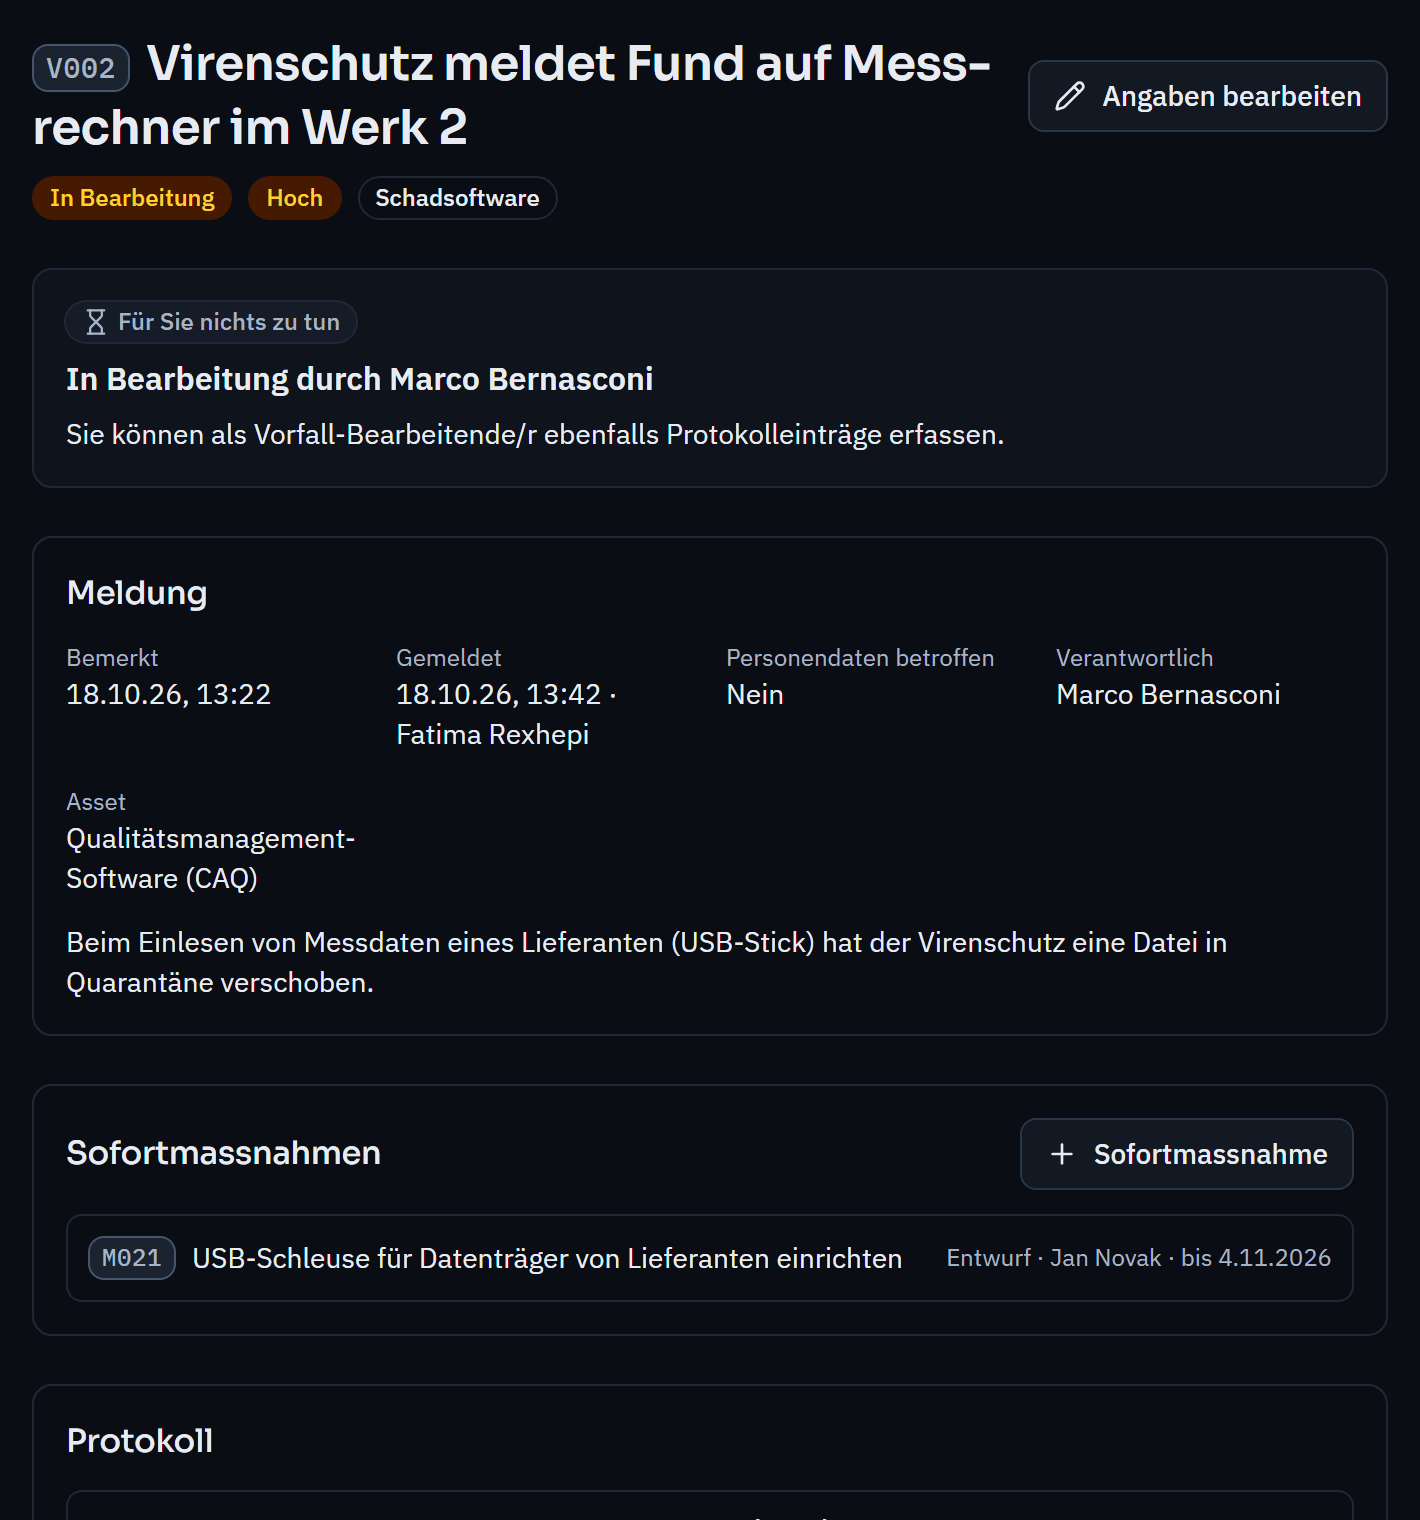
For major ICT-related incidents, DORA requires an initial notification, an intermediate report and a final report with fixed deadlines. Once you specify the reporting obligation for your organisation, the responsible person decides for each incident and receives tasks with the deadlines.
DORA applies to financial entities in the EU. It affects Swiss companies if they operate in the EU or provide ICT services to financial entities in the EU: these entities have to agree the contractual provisions under Art. 30 with their service providers.
FINMA, DORA and reporting obligations in one ISMS.
The obligations of entities in the EU.
No. For financial entities, DORA takes precedence over NIS2 as the more specific law. Many obligations correspond; the mappings show where one implementation covers both.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.