ISO/IEC 27001:2022
The international standard for an ISMS.
The Cybersecurity Framework (CSF) of the National Institute of Standards and Technology organises cyber security into six functions. In Varmo, it also serves as a common yardstick for comparing frameworks.
Platform framework and coverage from the Pro plan
All 22 categories and 106 subcategories from NIST’s official export, in the original wording, with the official implementation examples as guidance.
Every requirement of other frameworks is assigned to the CSF functions, through the mappings or manually. A radar chart shows how well a framework covers each function, and a list names the gaps.
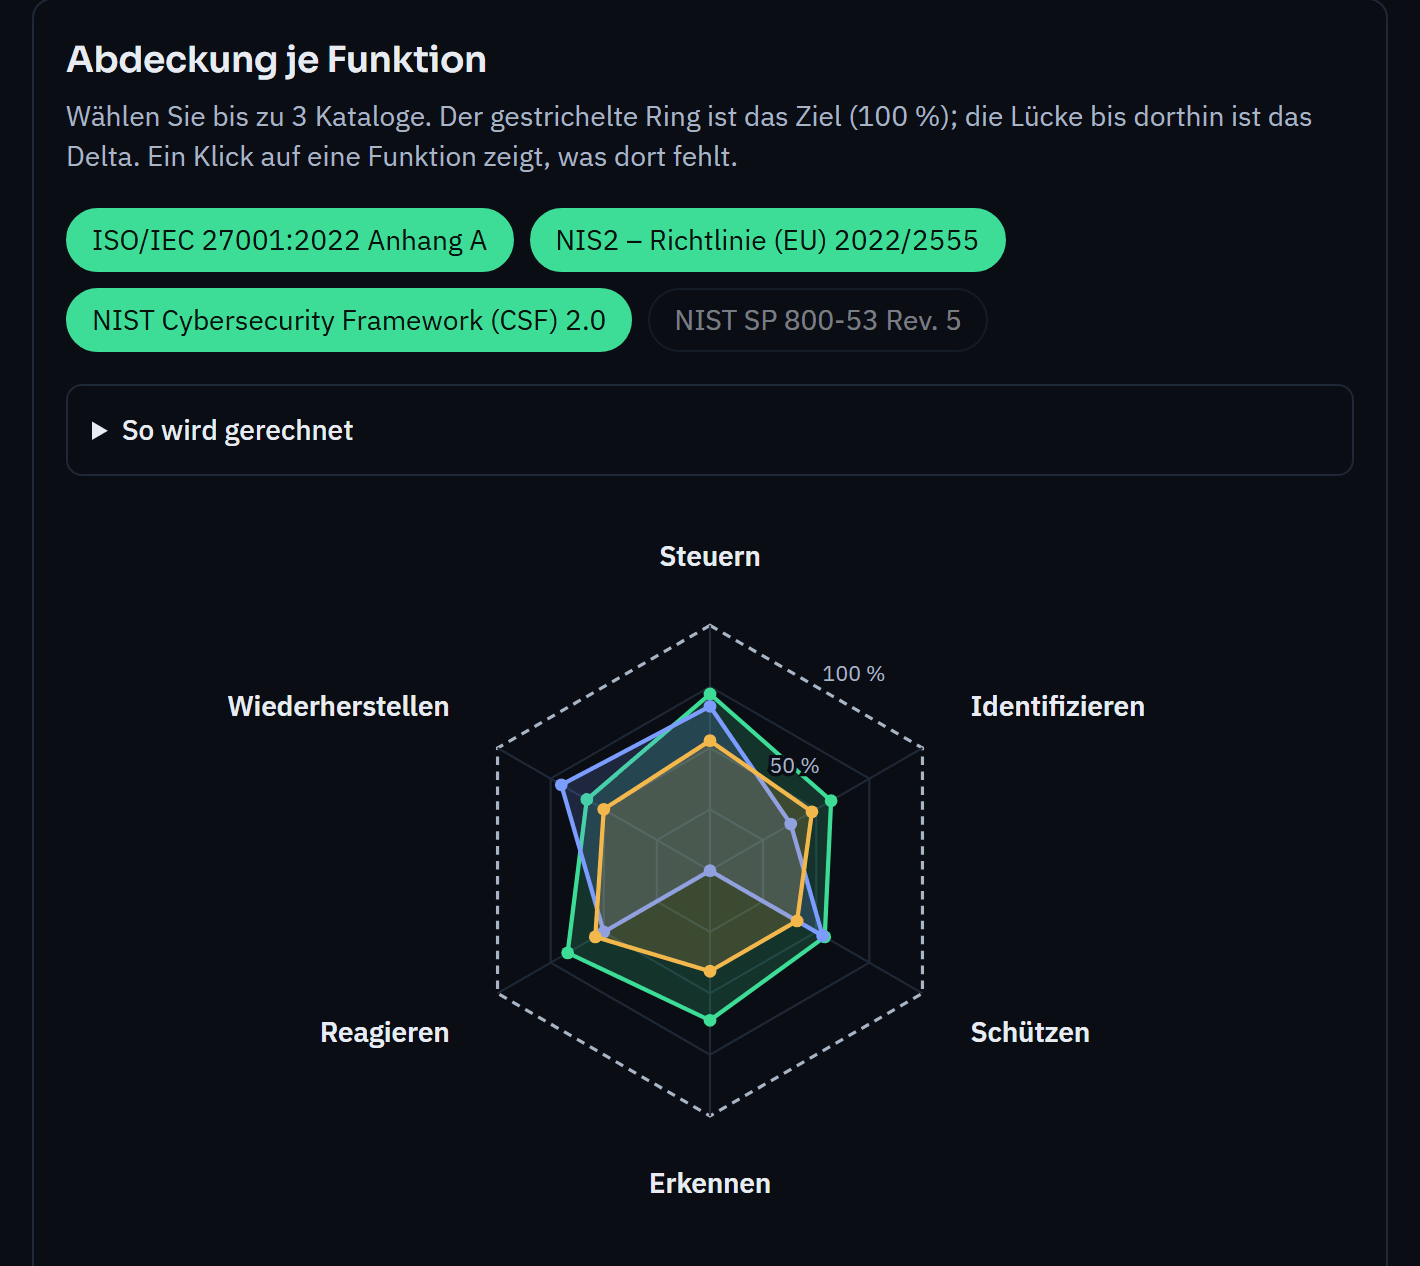
Mappings to ISO/IEC 27001 come from NIST’s public catalogue of Online Informative References, those to NIST SP 800-53 from the Informative References of NIST CSF 2.0, supplemented by our own mapping of almost all controls that NIST does not map (a few without any relation to the CSF remain unmapped); only reviewed mappings count as equivalent or included. NIS2 is mapped to the CSF, too.
The international standard for an ISMS.
The obligations of the EU directive.
No. NIST texts stay in the original English so that no meaning is lost in translation, even when you use the interface in German.
ISO/IEC 27001 is a certifiable standard for a management system. NIS2 is an EU directive with legal obligations for certain entities. The NIST CSF is a voluntary framework that organises cyber security into six functions. In Varmo, it serves as a common yardstick for comparing the coverage of the other frameworks.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.