ICT Minimum Standard (Switzerland)
The 108 measures with maturity levels 0–4.
Energy, water, health, transport or telecommunications: operators of critical infrastructure have to prevent outages, detect attacks and respond quickly. Varmo measures maturity against the Confederation’s ICT Minimum Standard and links it with risks, measures and incidents.
Each of the 108 measures receives a maturity level from 0 to 4 with a justification. Varmo suggests it based on your data: implementation and evidence, approved policies, regular controls. The evaluation follows the Confederation’s assessment tool, per category, per function and overall against the target.
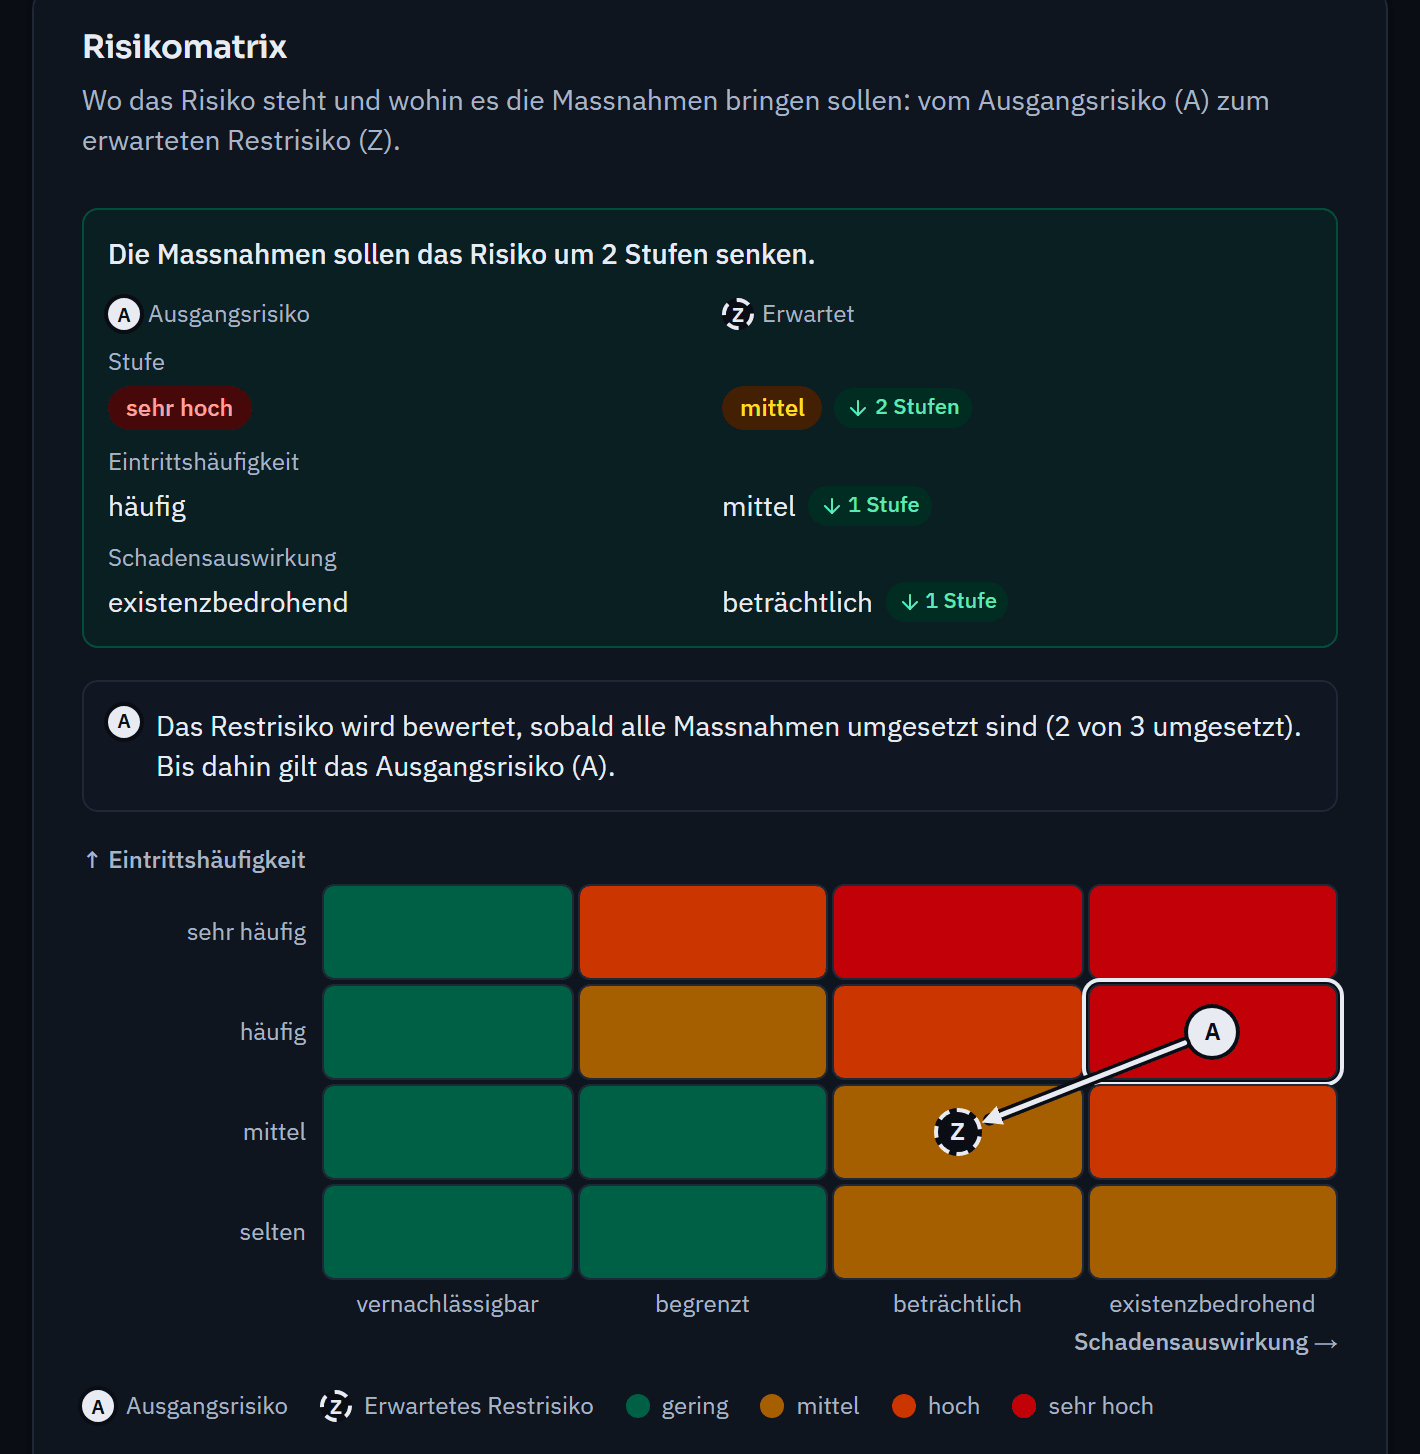
Critical services depend on systems, sites and service providers. You map these dependencies in the asset structure, and protection requirements are inherited along the chain. The risk analysis evaluates threats such as ransomware or the failure of a service provider, and for every risk it is clear who acts next.
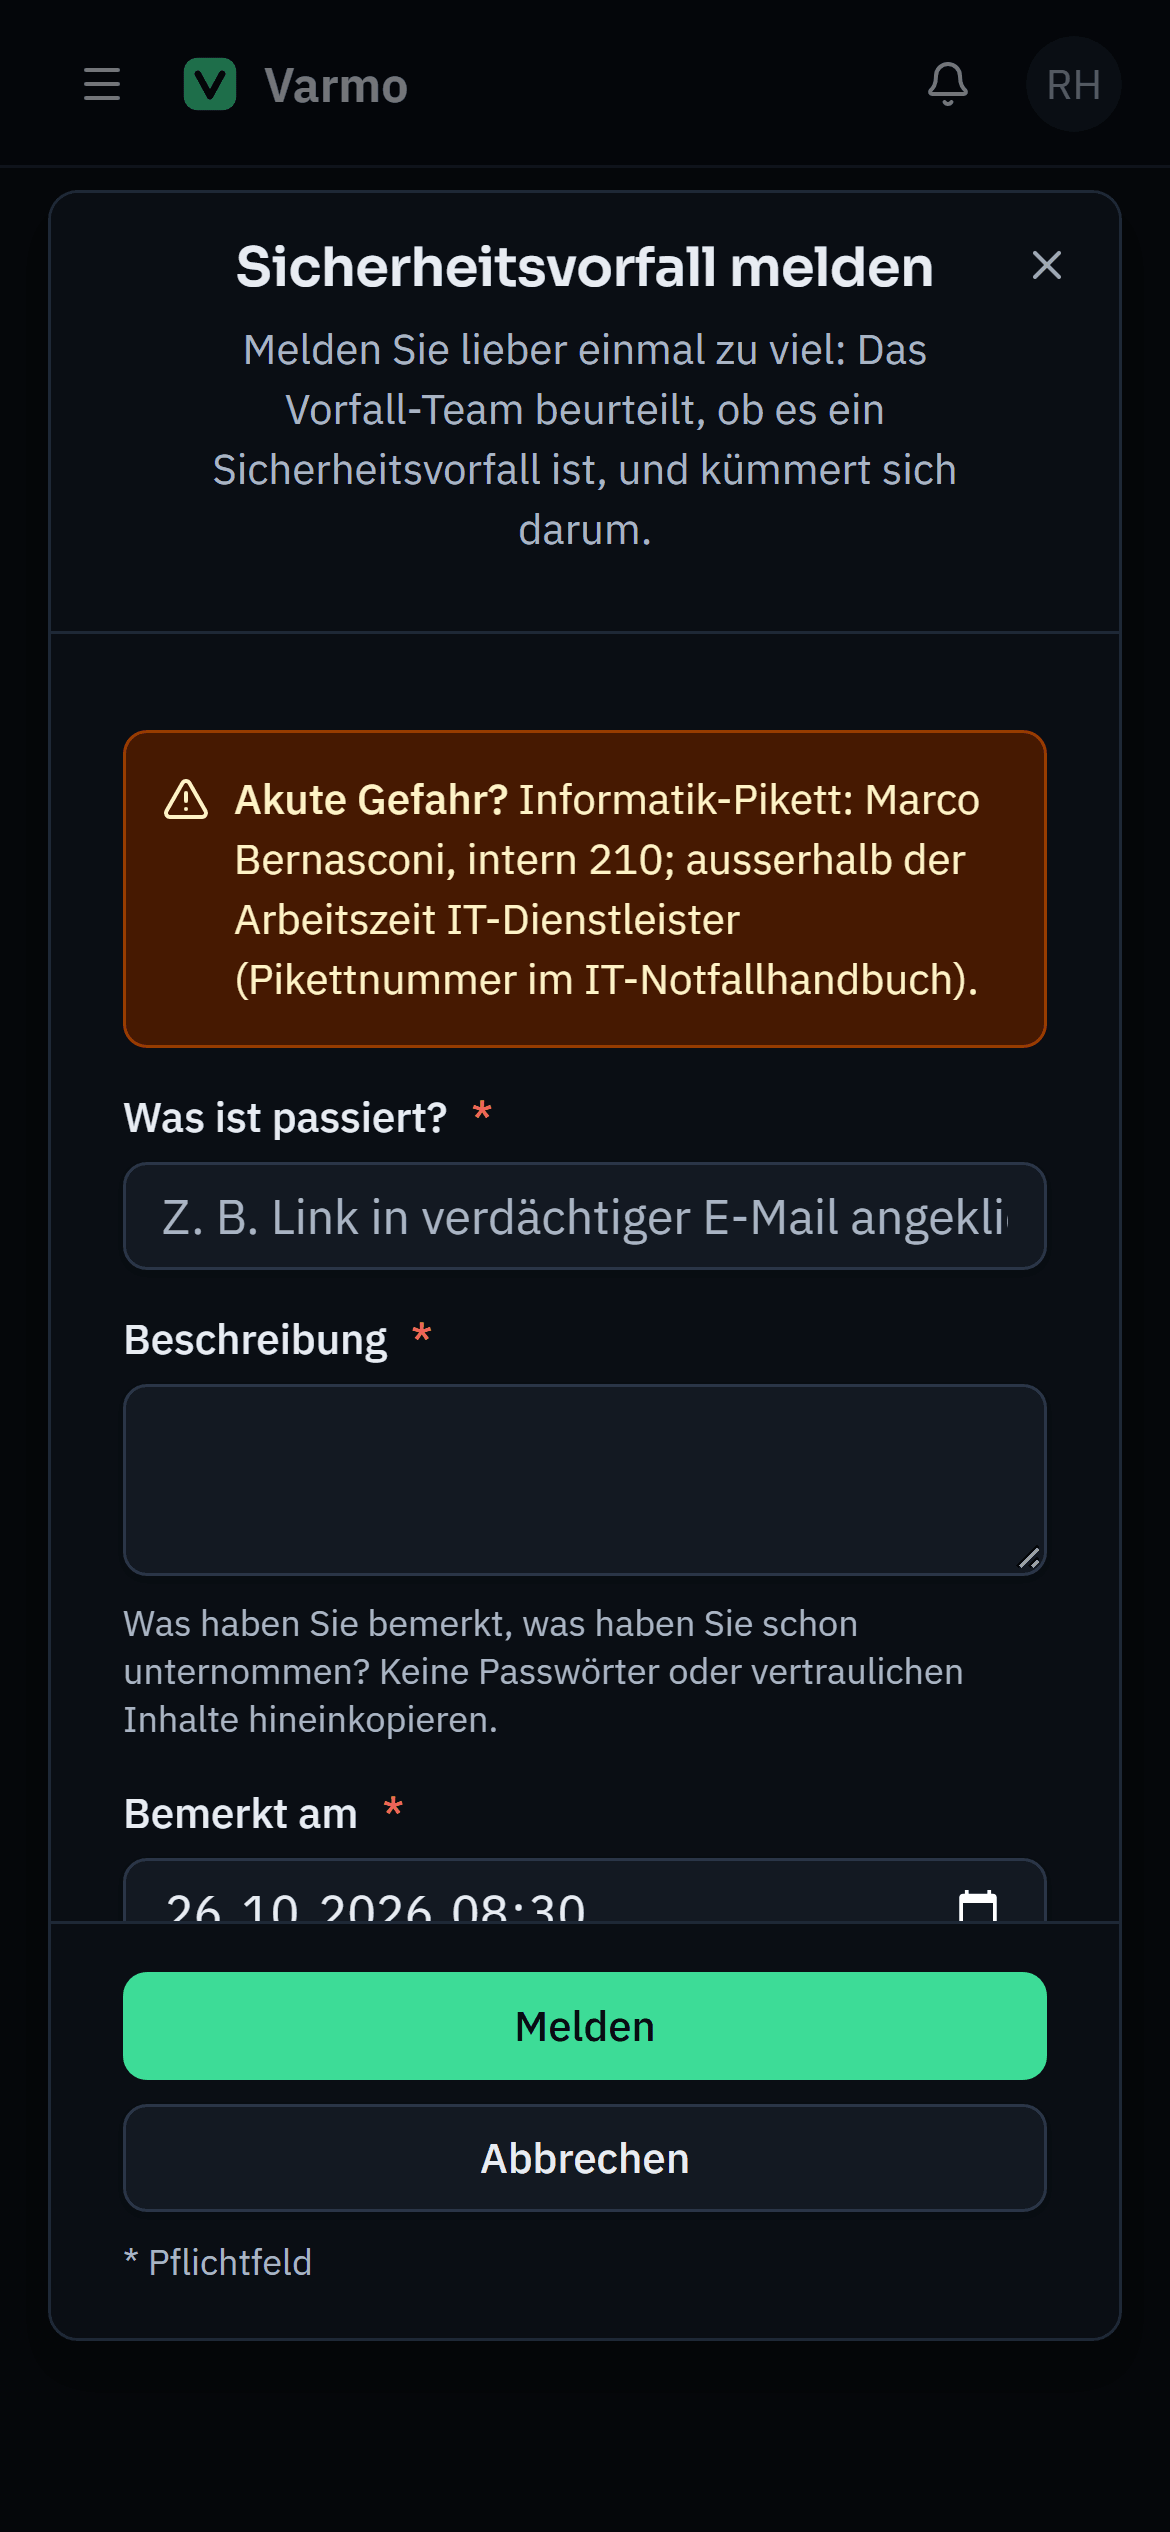
Employees report incidents from their phones, too. You record assessment, containment, communication and preservation of evidence in the incident history, and the follow-up closes it. Since 1 April 2025, critical infrastructure operators in Switzerland must report cyberattacks to the Federal Office for Cyber Security (FOCS, formerly NCSC) within 24 hours.
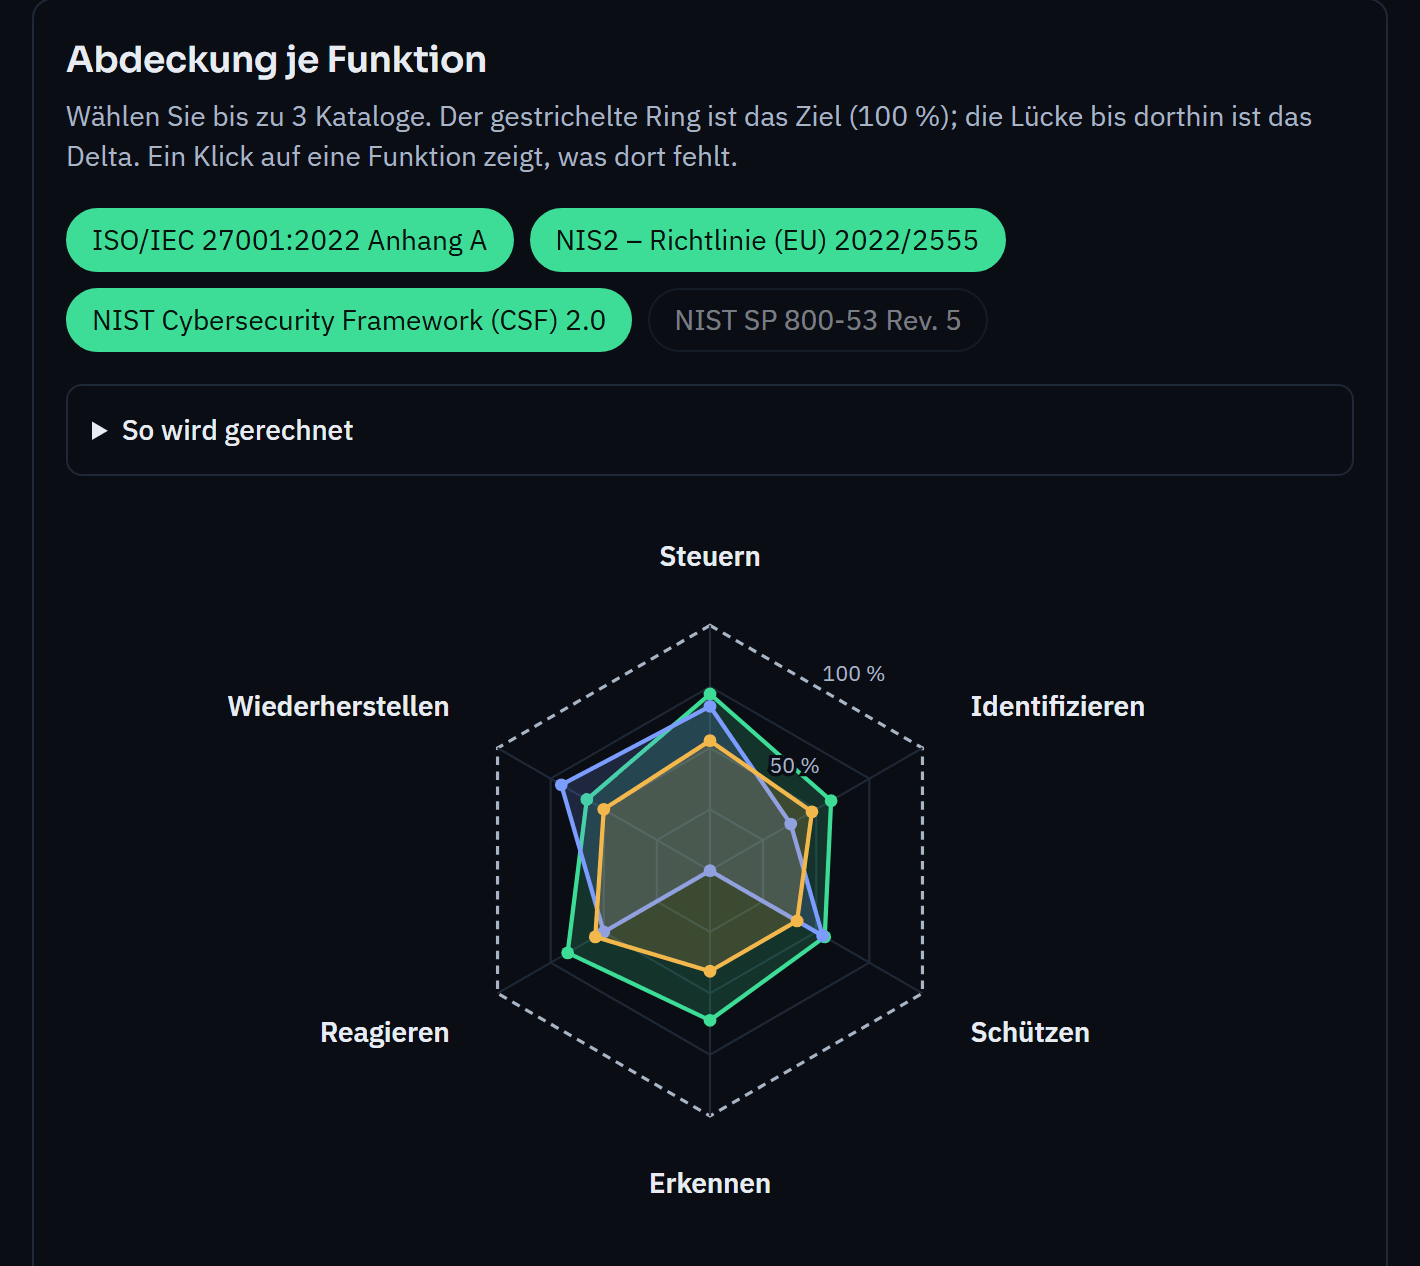
The ICT Minimum Standard is mapped to NIST CSF 2.0, ISO/IEC 27001 and NIST SP 800-53, and NIS2 to NIST CSF 2.0 and ISO/IEC 27001. This shows where one implementation covers several requirements; the coverage view shows the status by CSF function. Important for organisations that also operate in the EU.
Responsibility grants access: people see their own objects, and roles are only for overview tasks. The data is stored in Switzerland, and the operator only sees it with your time-limited approval. You can require a second factor for the whole organisation.
The 108 measures with maturity levels 0–4.
The obligations of entities in the EU.
Report, handle and follow up incidents.
Dependencies and protection requirements in detail.
Art. 74b ISA lists the authorities and organisations subject to the reporting obligation, for example in energy, water, health, transport, telecommunications and finance. Whether your organisation is one of them must be checked against the Act; Varmo does not replace a legal assessment.
For most organisations, it is a recommendation of the Confederation. Some industry rules are based on it, and it is regarded as the benchmark for the resilience of critical infrastructure in Switzerland.
No. Reports are made via the FOCS reporting form. In Varmo, you record the incident from the report through to the follow-up, including external communication.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.