Measures & internal controls
Implement the treatment and back it up with evidence.
From an employee’s first report to the formal acceptance of the residual risk: every step has a responsible role, and every decision is justified and traceable.
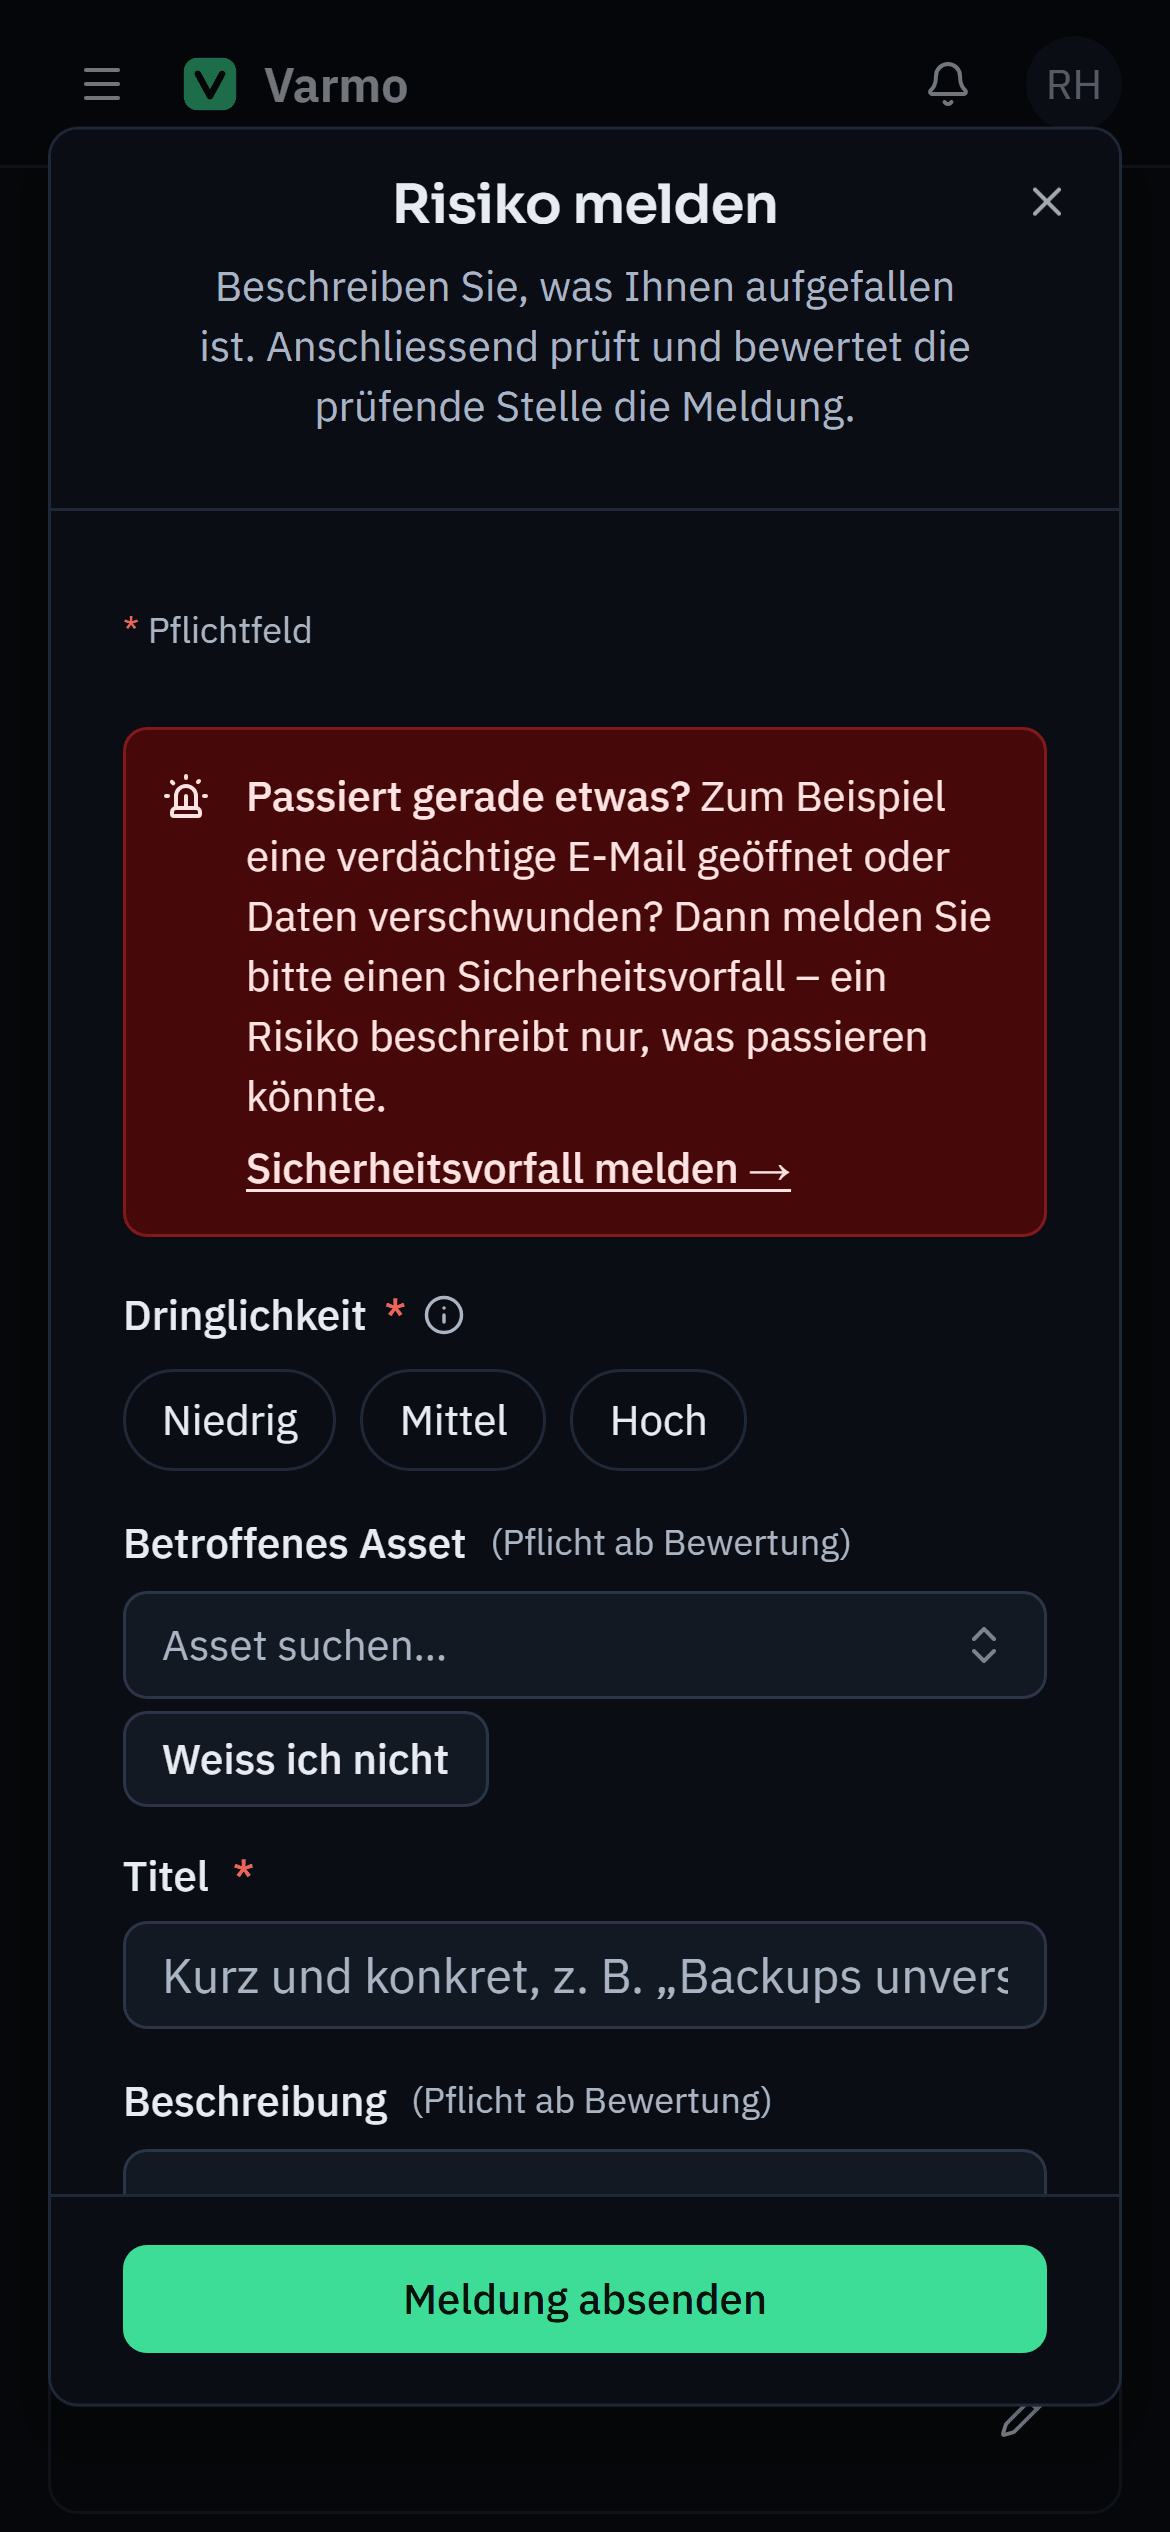
All employees can report risks, anonymously if they wish. A reviewer role assesses the report and assigns it to a risk owner.
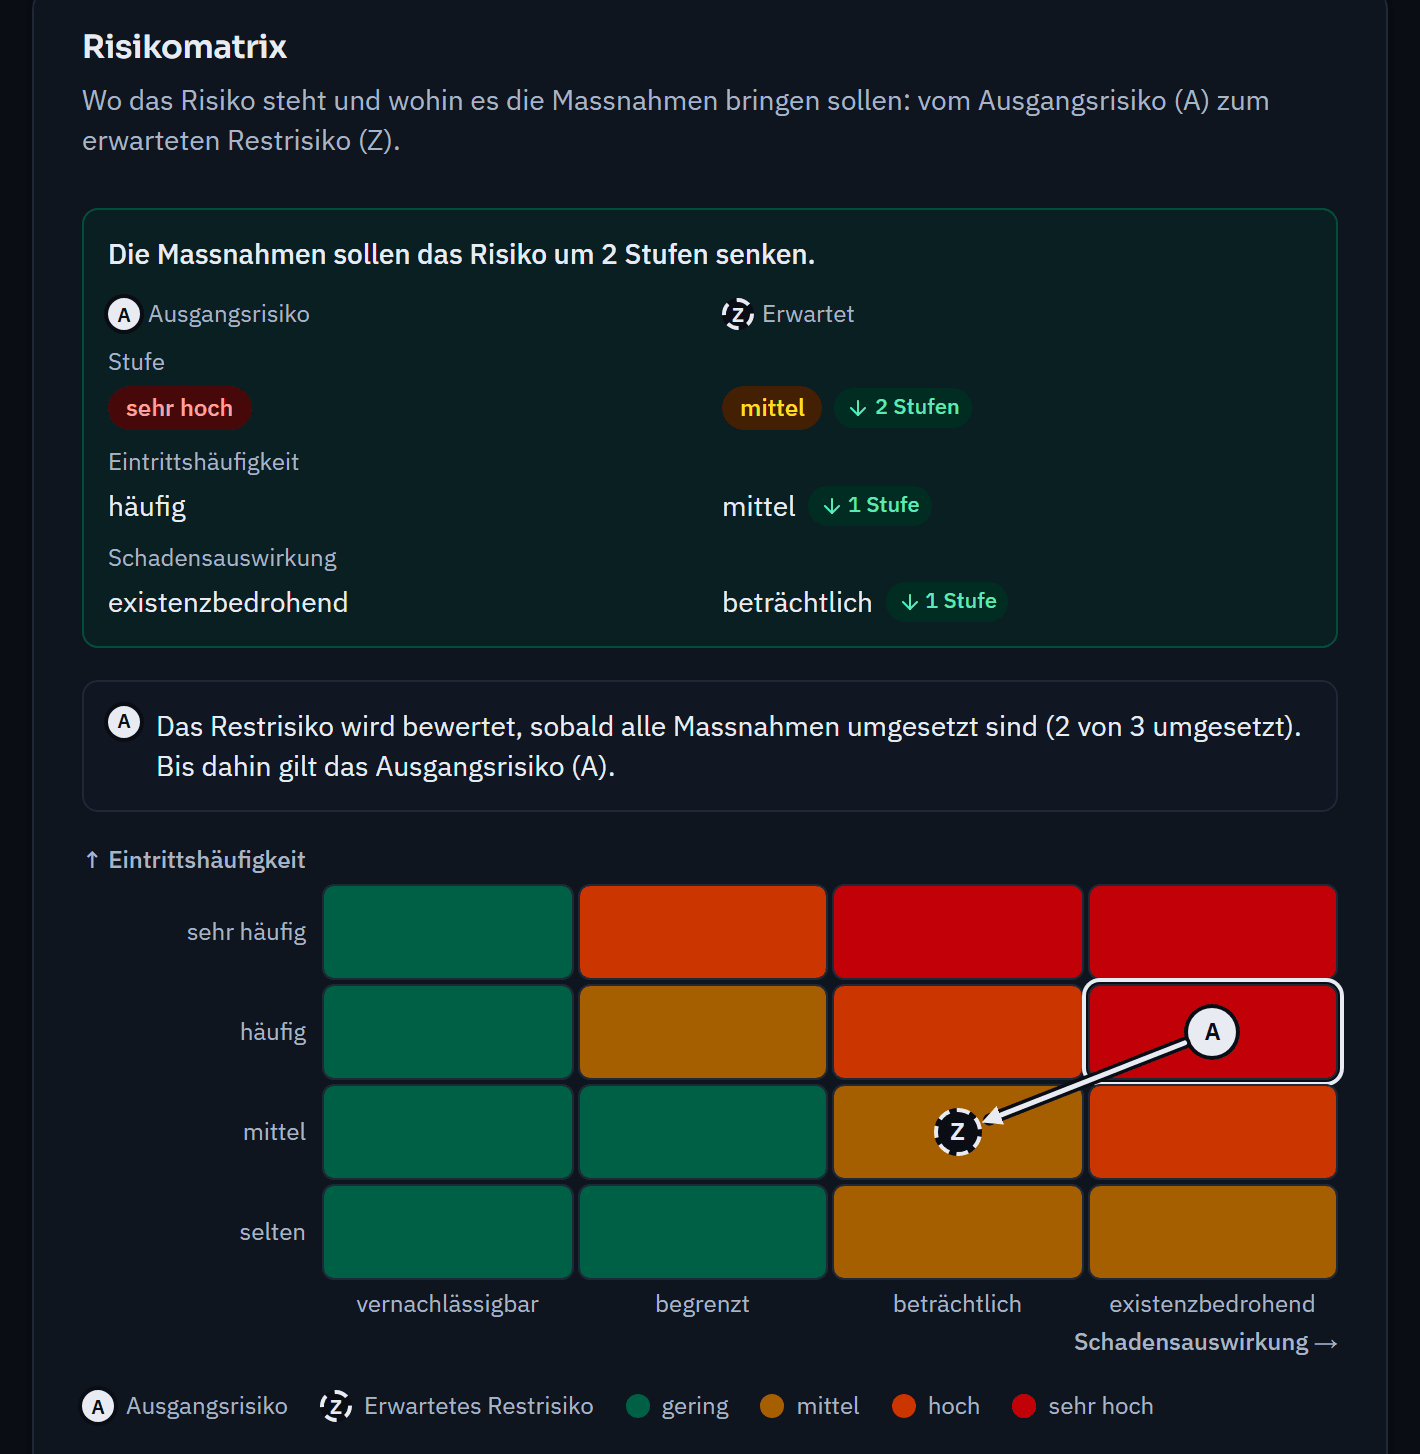
Assess risks following BSI Standard 200-3 or with your own 5×5 or 6×6 matrix, optionally with impact categories such as financial or reputational.
Each risk shows where it sits in the matrix and where the measures are meant to take it, who is up next and which steps follow: assessment of the residual risk under the four-eyes principle, the risk owner’s decision and regular reviews.
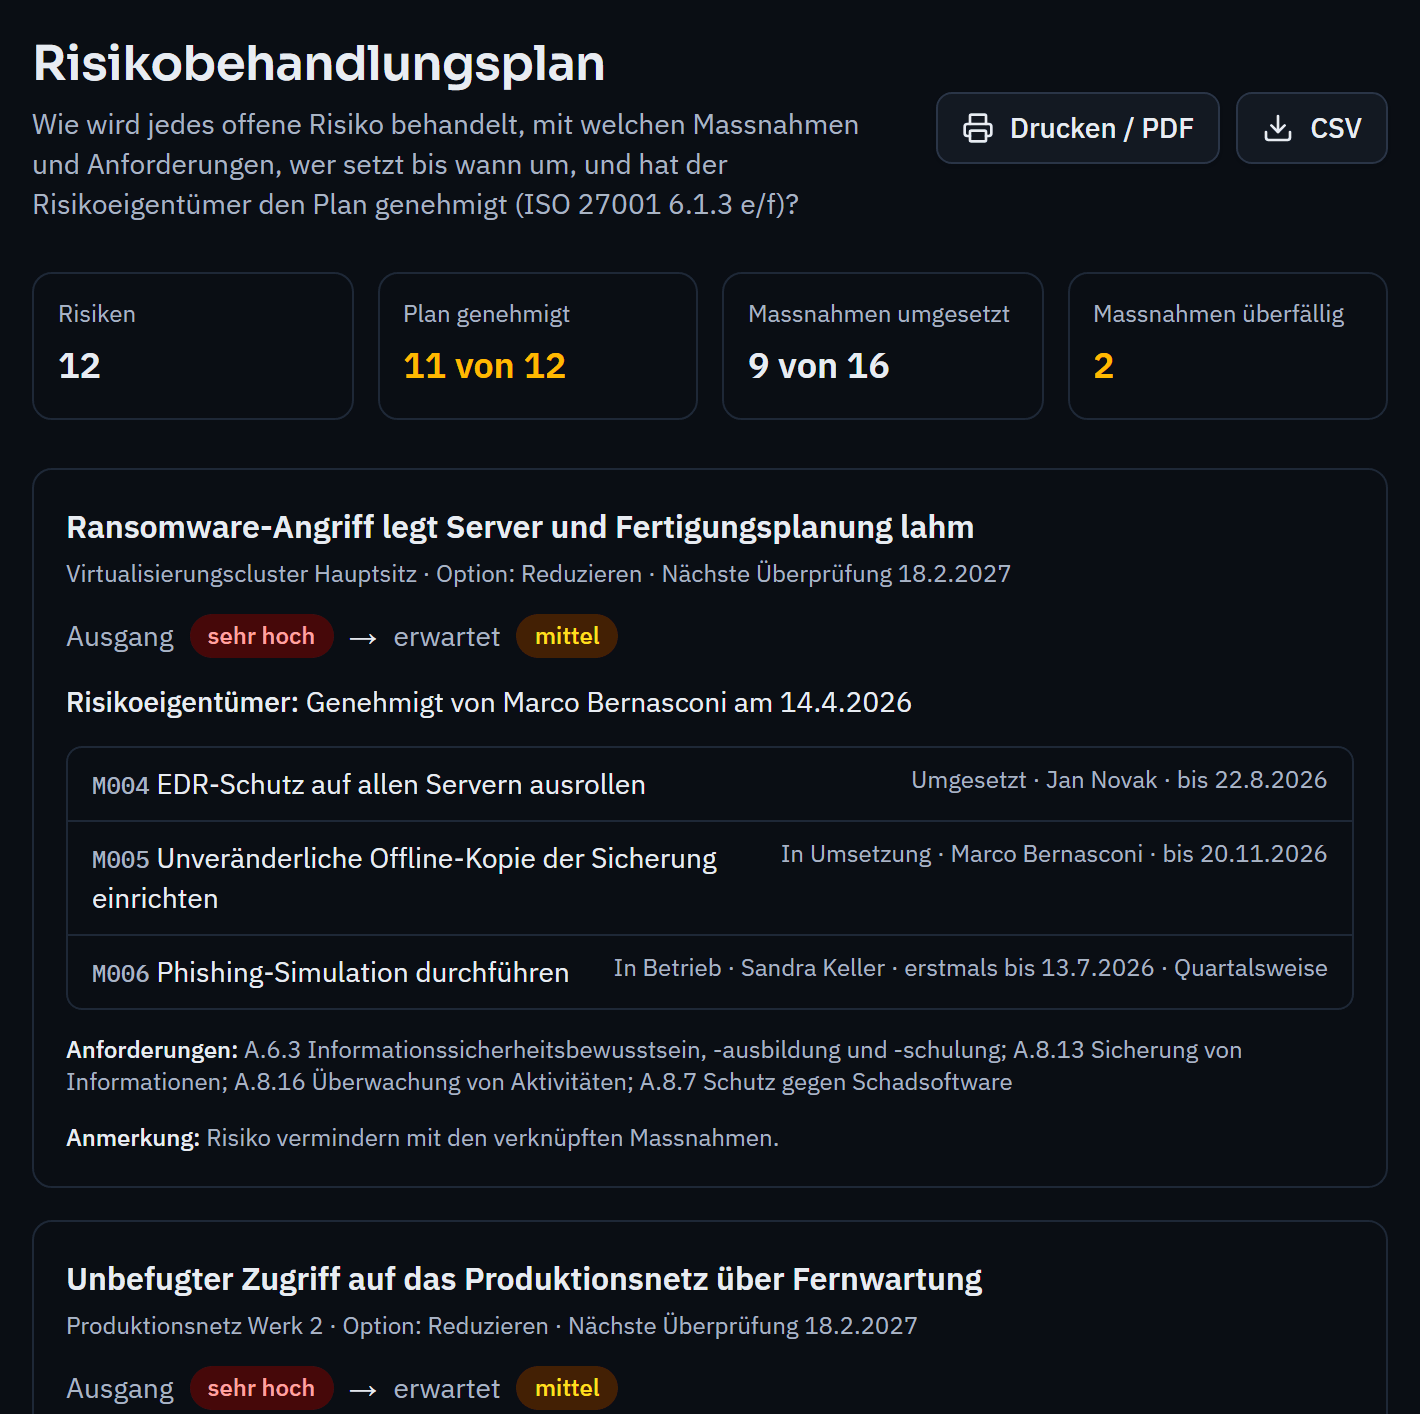
For every risk you decide: reduce, avoid, transfer or accept. Measures and the expected residual risk are set right away, and the risk owner approves the treatment plan.
For each risk level you define who may accept: the risk owner alone, with approval by a functional role such as top management, or nobody at all. Regular reviews keep the assessment up to date.
Implement the treatment and back it up with evidence.
The basis of every risk assessment.
Risk owner, residual risk and other terms.
Yes. Besides the BSI default, there are templates for 5×5 and 6×6 matrices whose levels, descriptions and colours you define yourself.
If recurring measures or internal controls are missed or carried out with deviations, the risk owner is prompted to have the risk reassessed.
From your data: for every risk, the treatment, measures, responsible people, due dates and expected residual risk are already defined. The plan can be printed and exported as CSV.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.