FINMA Circular 2023/1
Operational risks and resilience – banks.
Banks, securities firms and their IT service providers have to demonstrate how they manage operational risks, ICT and cyber risks and the resilience of critical functions. Varmo links FINMA Circular 2023/1 and DORA with risks, measures, service providers and incidents.
FINMA Circular 2023/1 applies to banks and securities firms in Switzerland, DORA to financial entities in the EU. Both are available as frameworks with their requirements and are mapped to each other: what you implement for one shows up in the other as fulfilment or a suggestion.
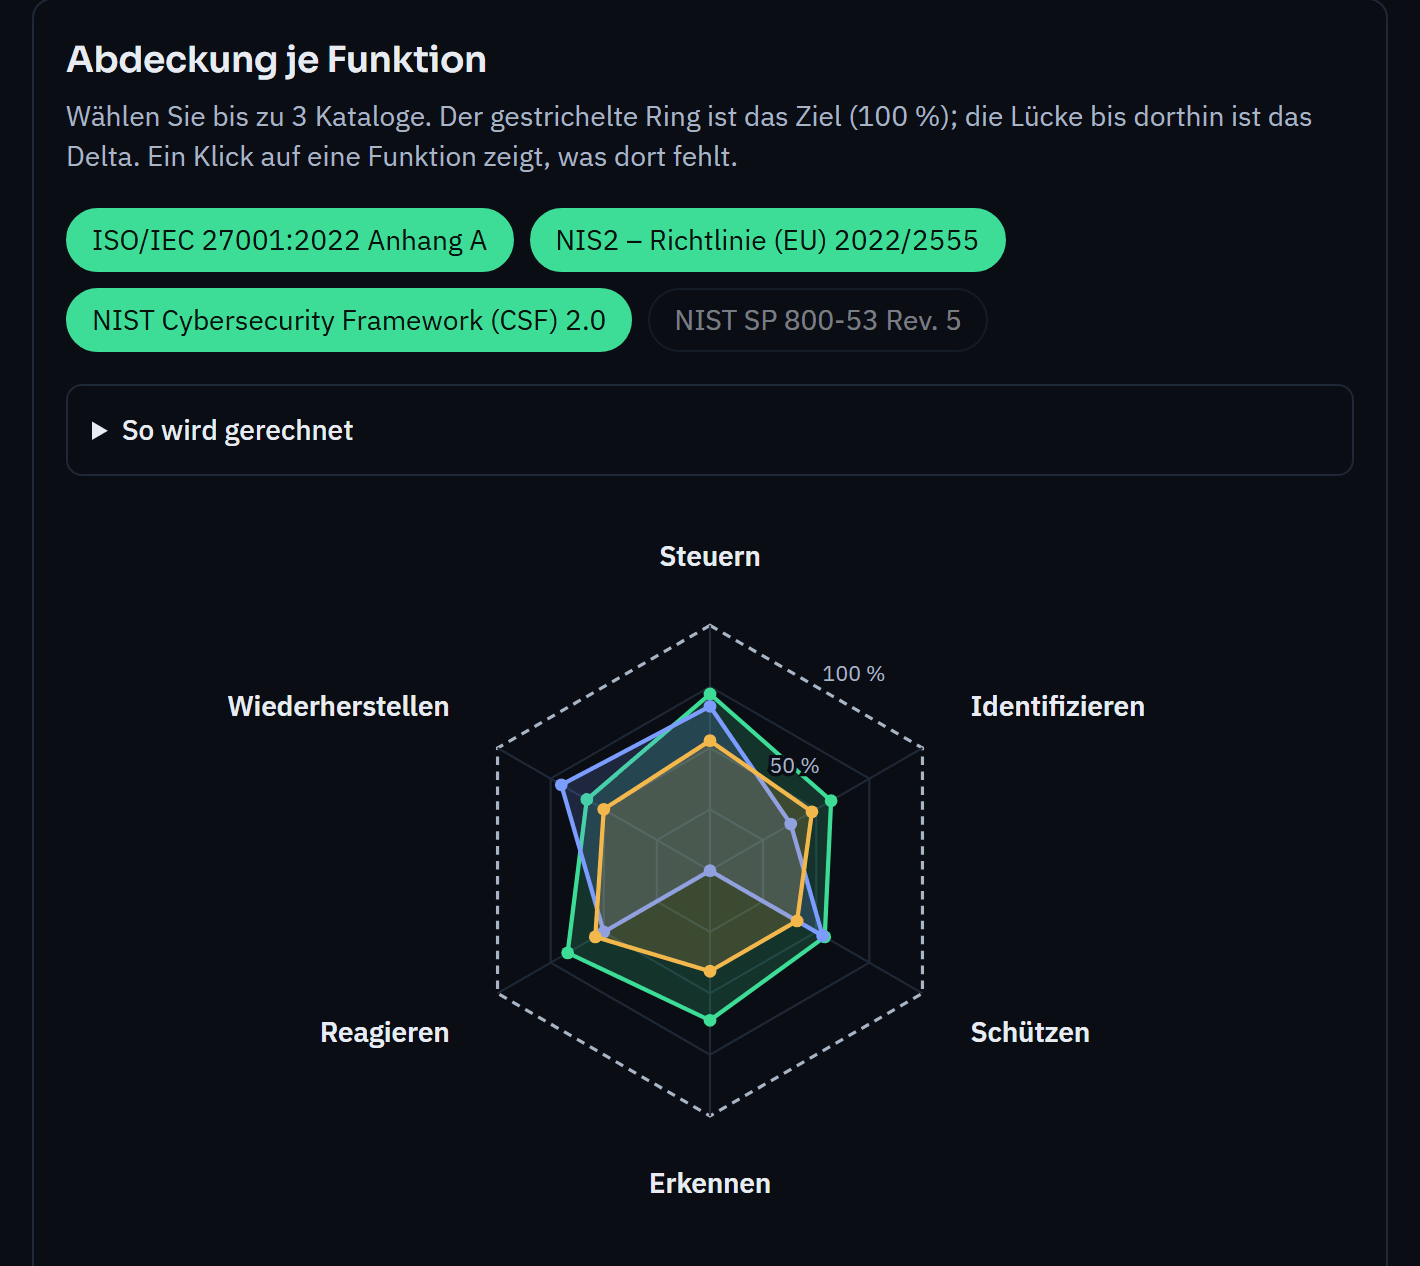
You document the obligations of the board of directors and executive board, strategy, testing programme and reports once on the organisation asset. Access, hardening, vulnerabilities, logging and backup are checked by the owner of each system, and contractual provisions per ICT service provider. Varmo suggests the relevant chapters for each asset category.
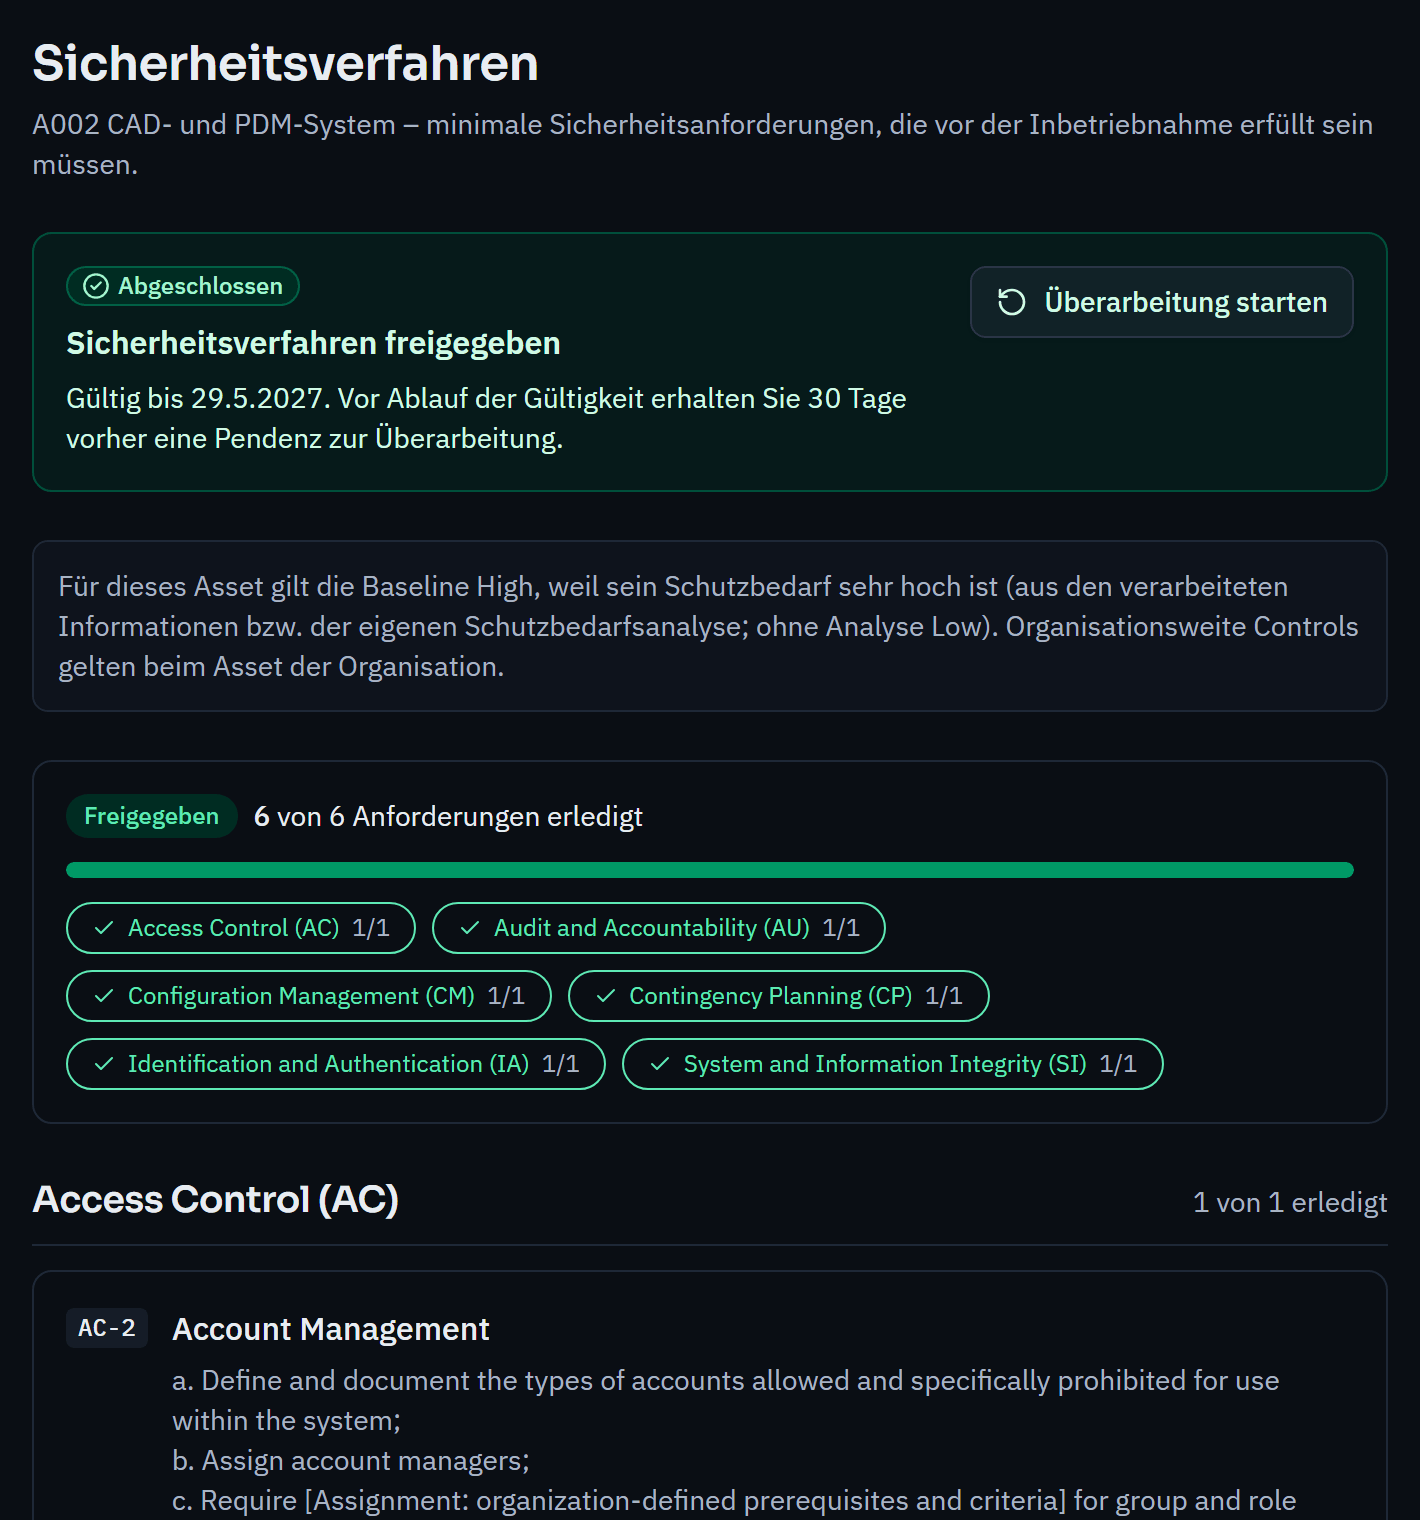
Specify which reporting obligations apply to your organisation: FINMA, DORA supervisor, FOCS or NIS2. For every incident, the responsible person decides whether a report is required and receives a task with the statutory deadline for each report, for example 24 and 72 hours for FINMA.
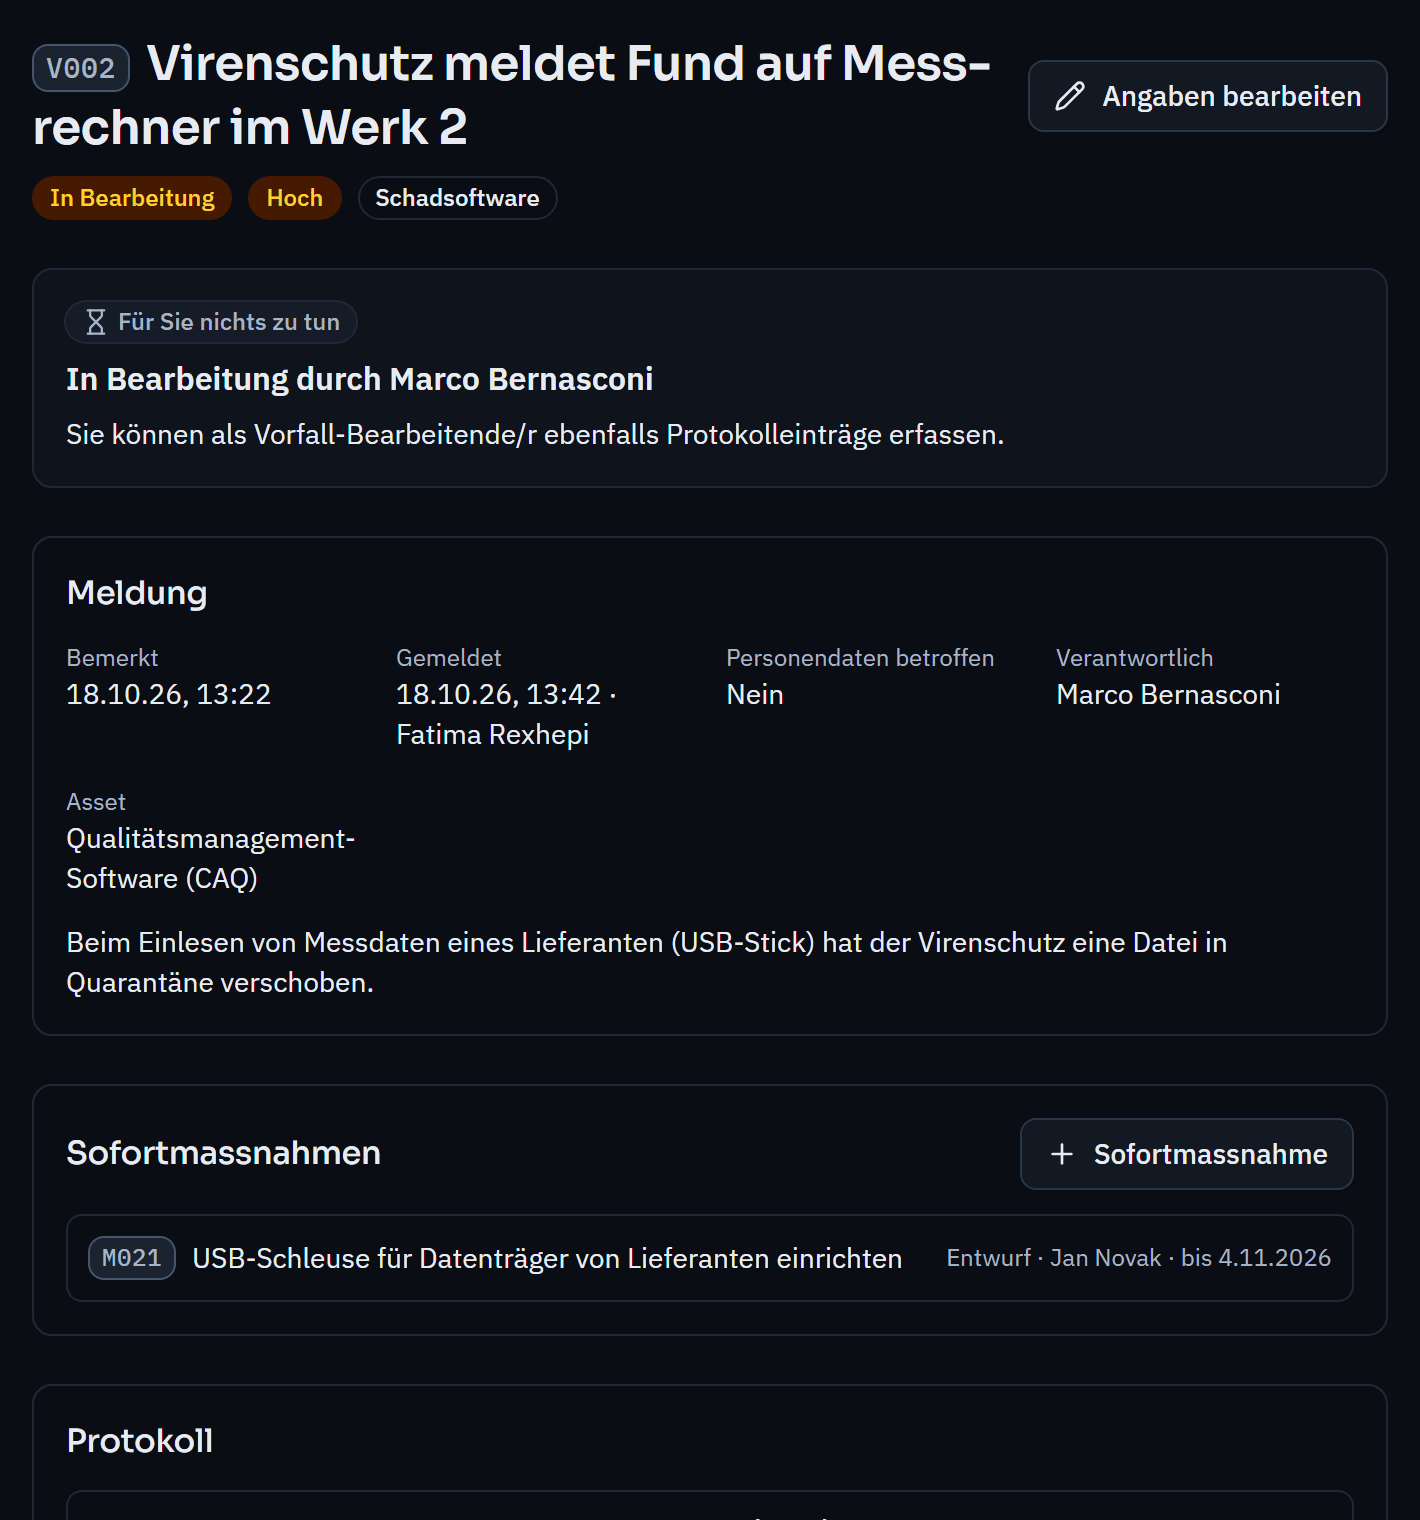
Risk analysis, measures, internal controls, audits and management review are all in the same system. For every risk and every finding, it is clear who acts next.
Responsibility grants access: people see their own objects, and roles are only for overview tasks. The data is stored in Switzerland, and the operator only sees it with your time-limited approval. You can require a second factor for the whole organisation.
Operational risks and resilience – banks.
Digital operational resilience for the financial sector.
Handle incidents and record reports.
Directly only to financial entities in the EU, for example subsidiaries in the EU. Swiss IT service providers of EU financial entities are affected by DORA through the contractual provisions under Art. 30.
No. Varmo structures implementation and evidence and shows gaps; the regulatory audit remains with the audit firm.
No. Reports are submitted through the channels of FINMA or the supervisor. In the incident, you record deadlines, time and reference of every report.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.