Assets & protection requirements
Protection requirements analysis and security procedures in detail.
Public bodies have to justify and document their decisions. Varmo maps protection requirements analysis, security procedures, approvals and logs so that every step remains traceable.
First the protection requirements of the information, then the systems that process it. Owners answer check questions for each protection goal, and the analysis is approved through a defined approval workflow.
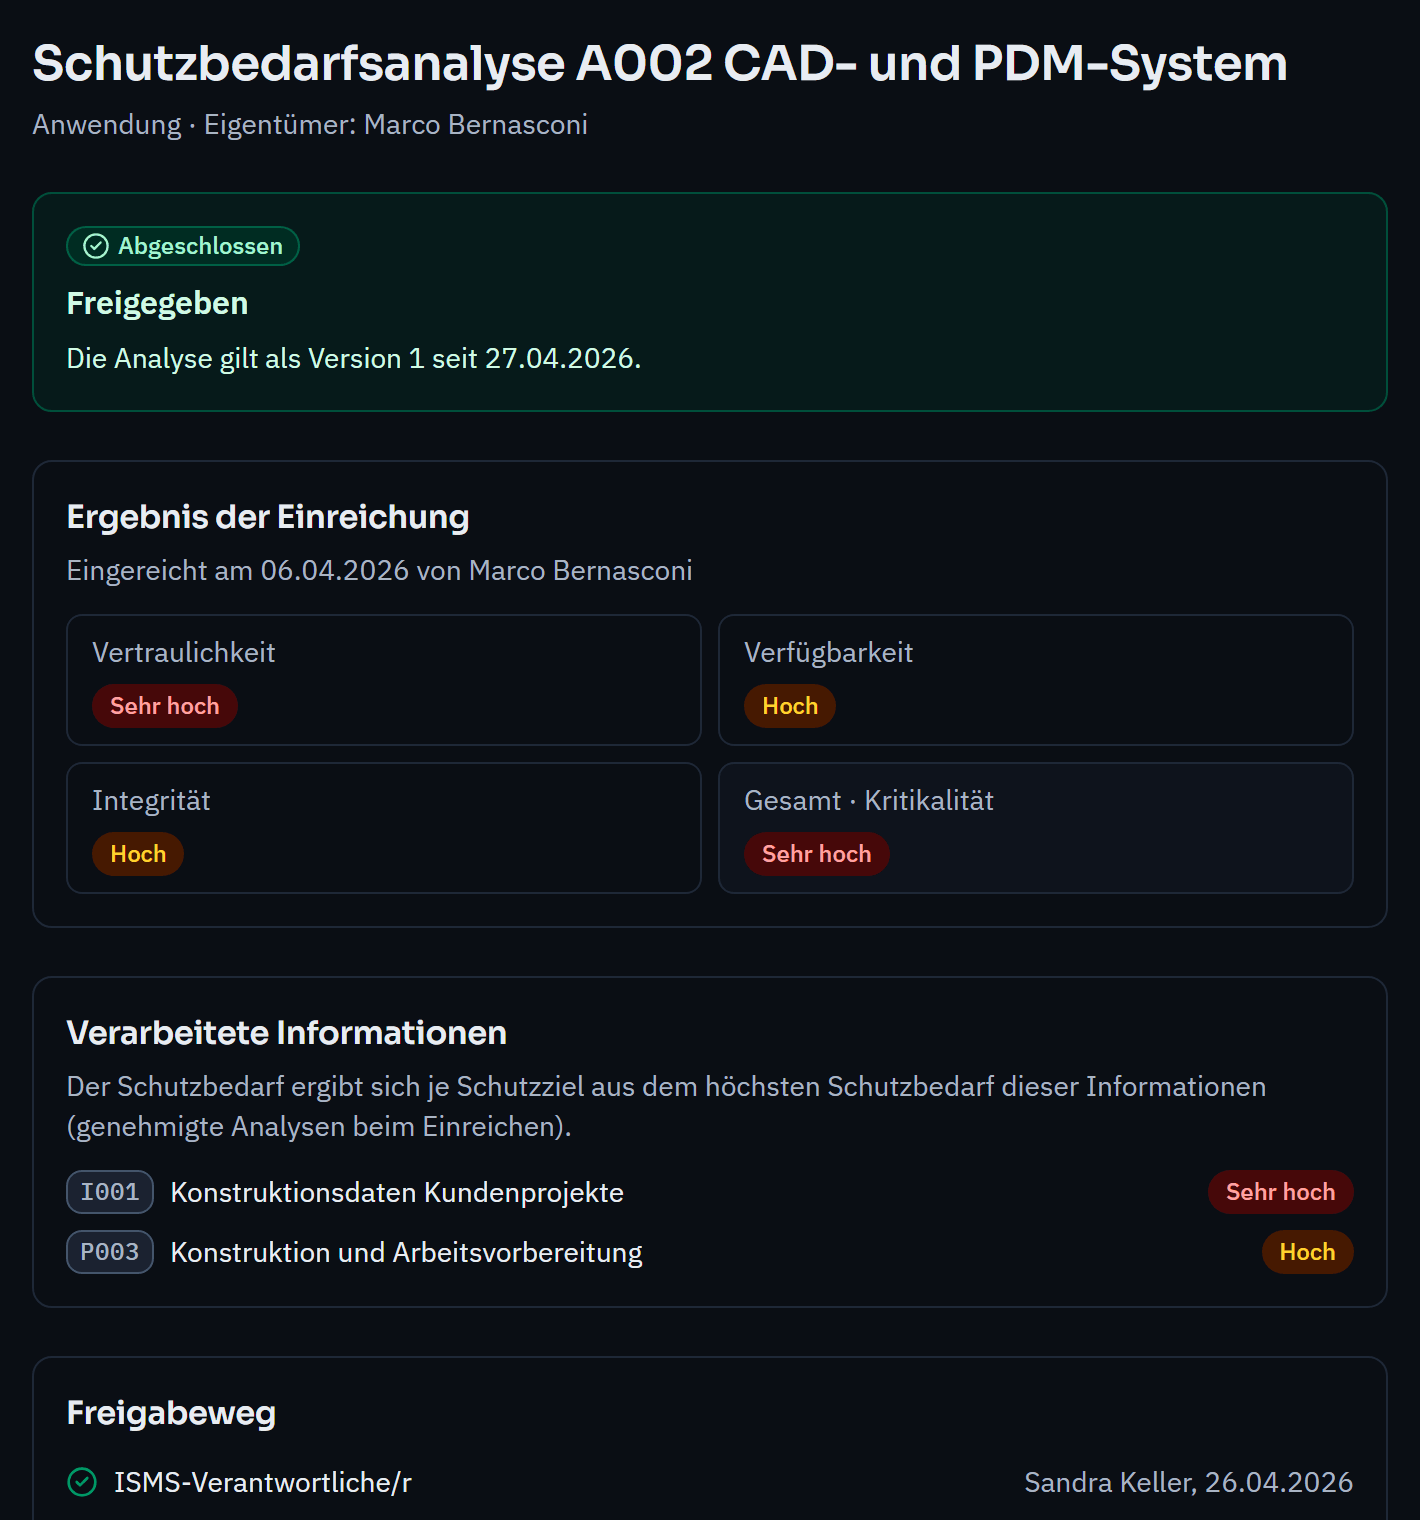
Each system is subject to the requirements that match its protection requirements. The owner documents implementation with evidence; deviations are handled with a measure or a time-limited exception. Where requirements are elevated, a risk analysis follows, optionally to BSI Standard 200-3.
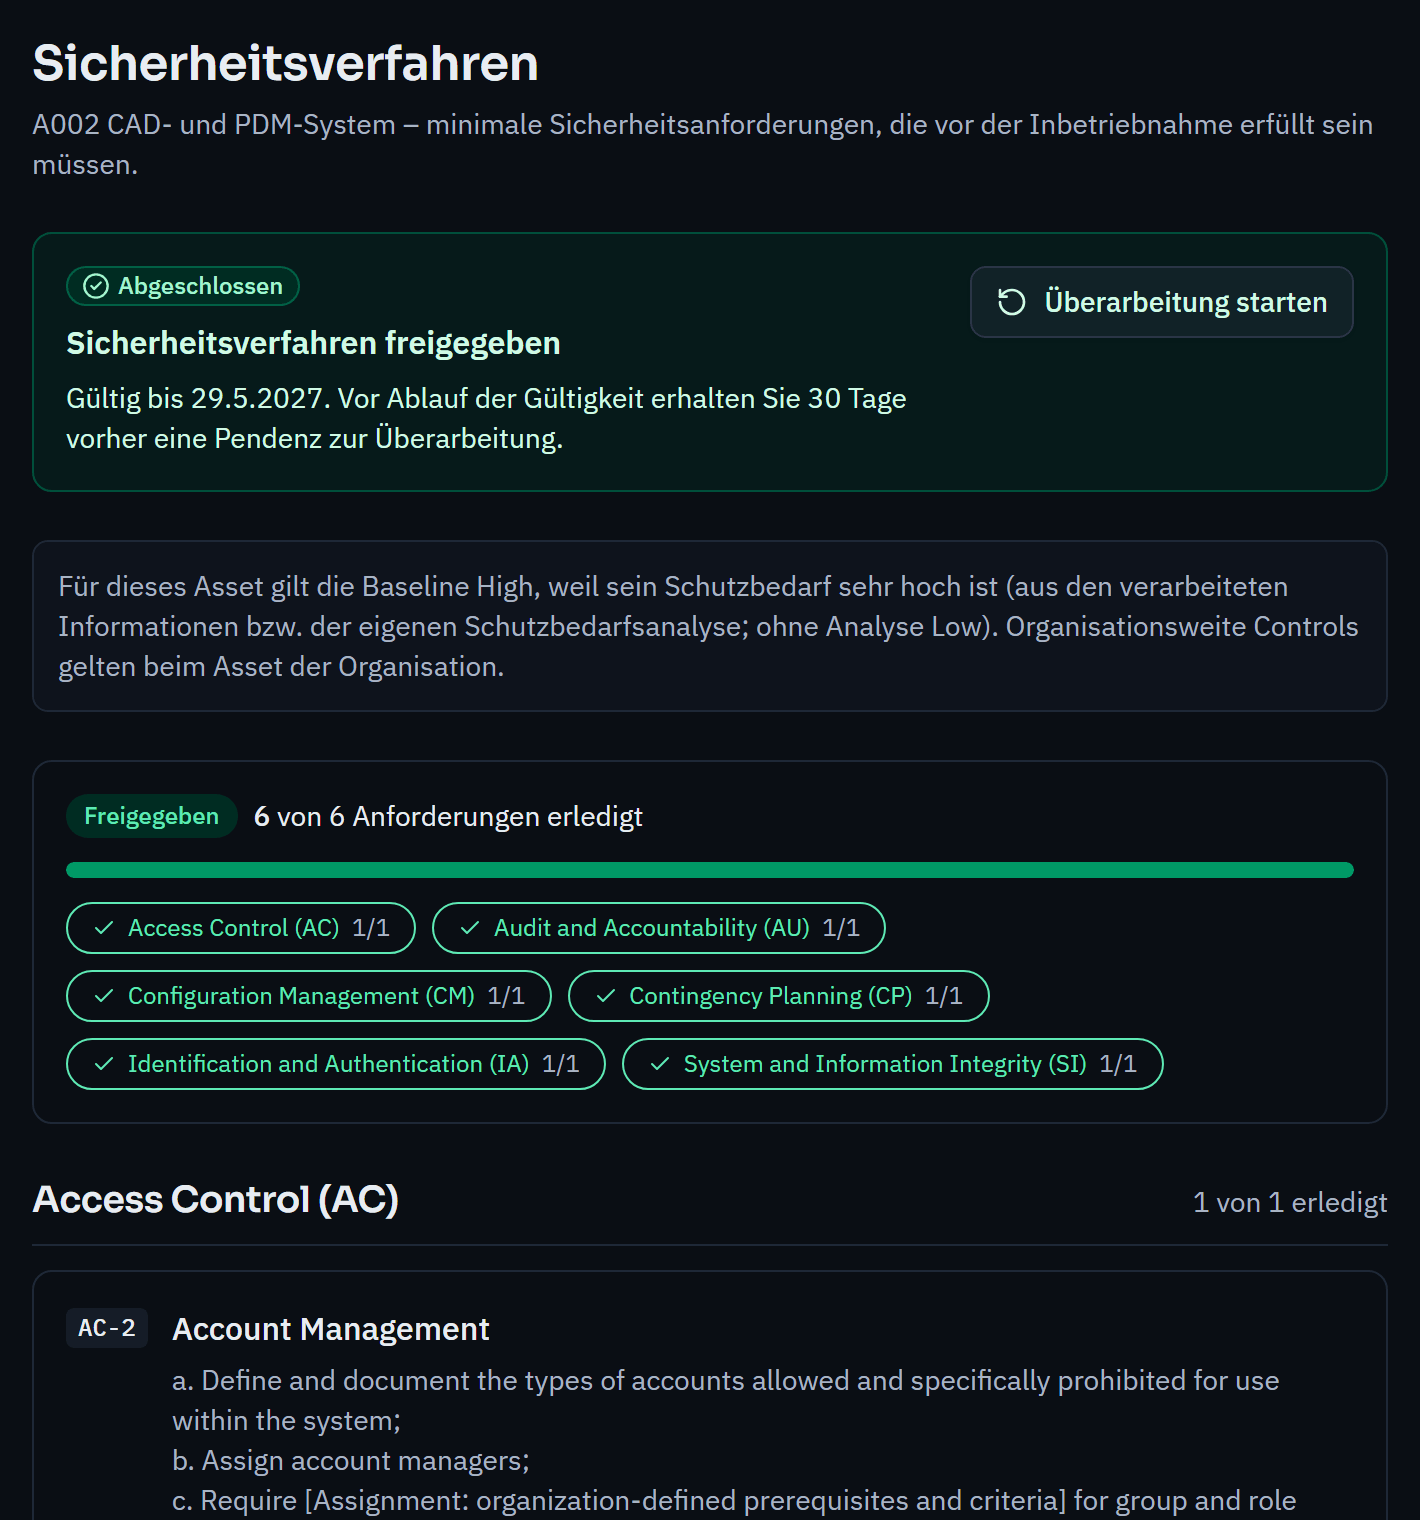
In the organisation profile, you specify whether your organisation is a federal body. For federal bodies, Varmo checks the legal basis for the processing and the obligations under the Data Protection Ordinance, such as logging; you create the data protection impact assessment directly in the system.
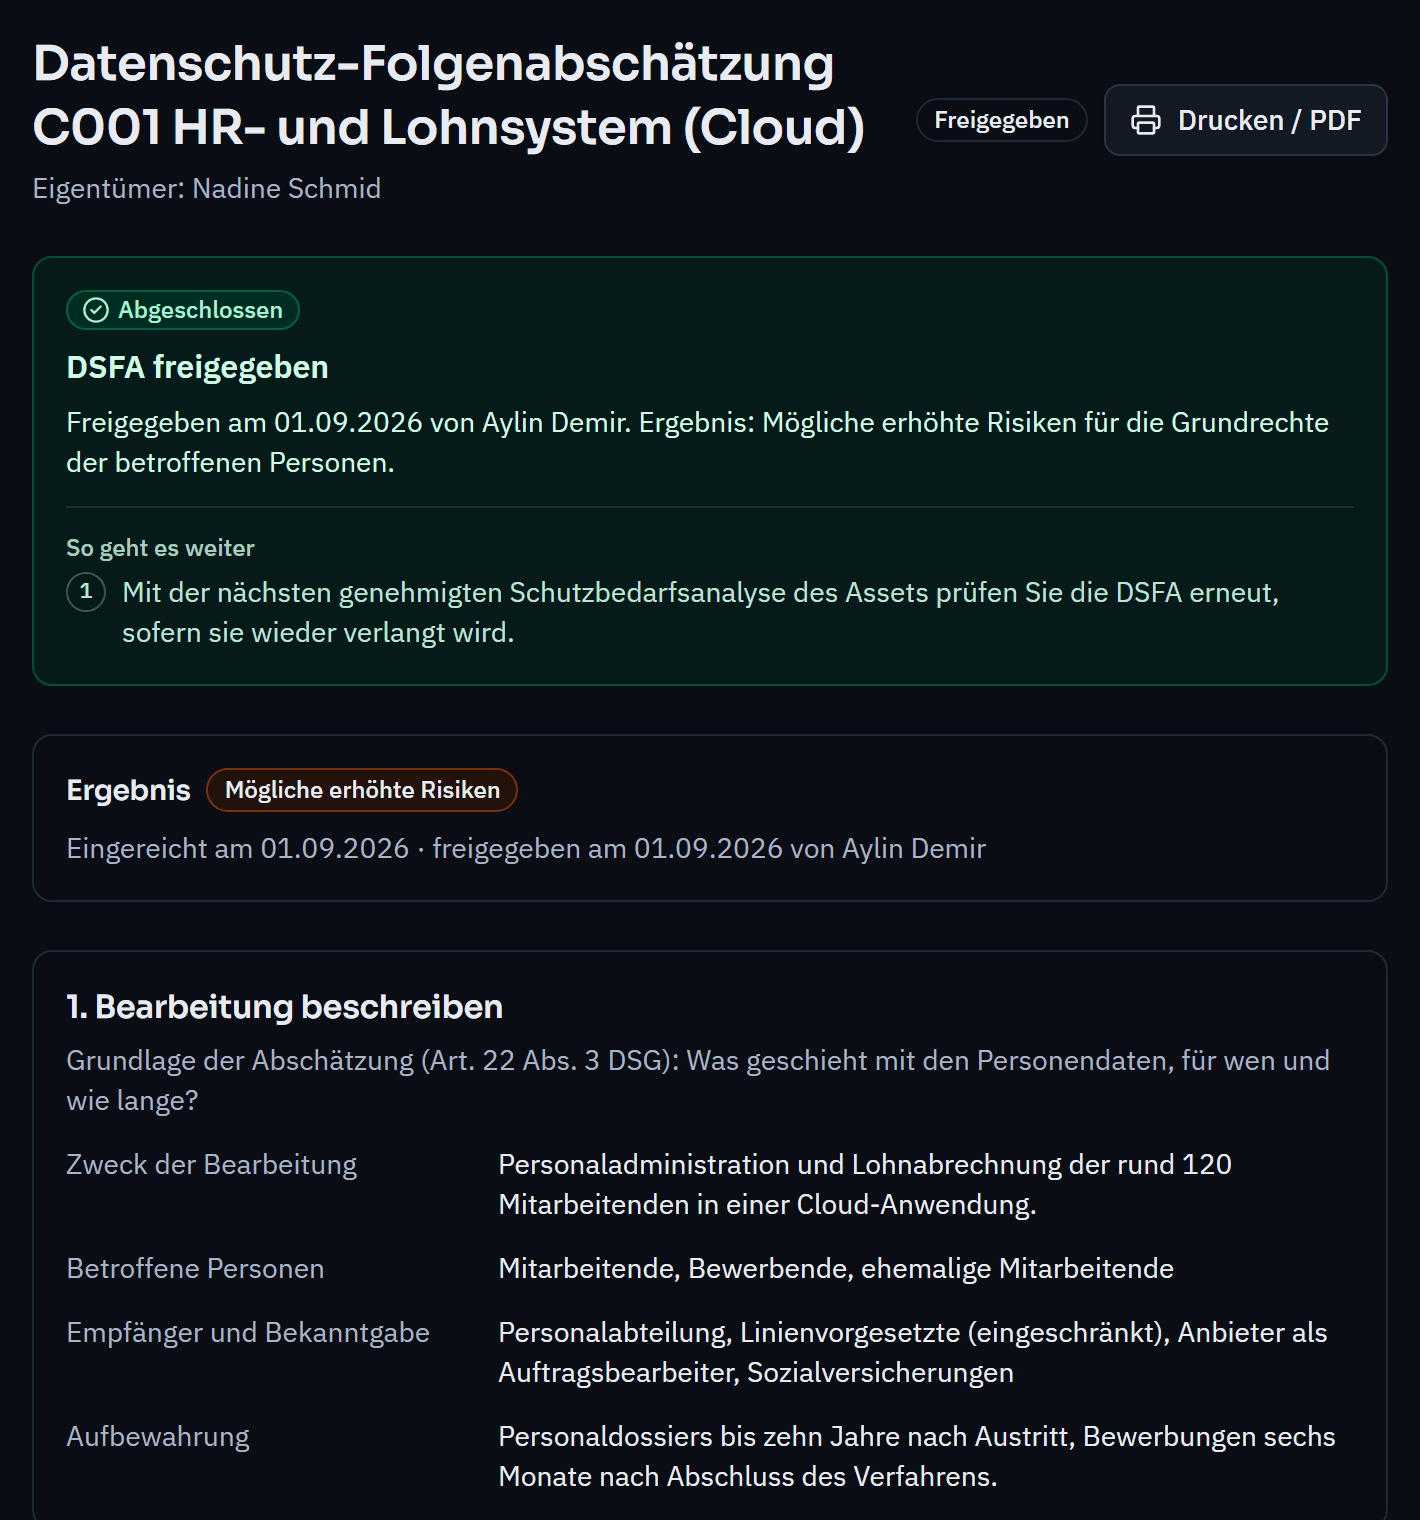
Approvals follow defined approval workflows under the four-eyes principle. Completed analyses, audits and reviews cannot be changed, and every change is logged without gaps.
Responsibility grants access: people see their own objects, and roles are only for overview tasks. The data is stored in Switzerland, and the operator only sees it with your time-limited approval. You can require a second factor for the whole organisation.
Protection requirements analysis and security procedures in detail.
FADP obligations and the data protection impact assessment.
The Confederation’s minimum requirements per system.
How we protect your data.
The ISA applies to federal authorities and to organisations that access federal information or systems; cantons and municipalities have their own rules. Regardless of that, data protection law requires appropriate technical and organisational measures. An ISMS is the usual way to manage them in a traceable manner.
For the baseline protection security level, Varmo includes the Confederation’s ICT baseline protection – directive Si001 “IT baseline protection in the Federal Administration”, based on the ISA and ISO – as a framework from the Pro plan. You record other rules of your body, for example for elevated protection requirements or cantonal regulations, as a custom framework (from Starter also via CSV import) and implement them like any other requirement.
Yes, from the Pro plan. Under one account you run several organisations, for example one per office; the data stays strictly separate.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.