ISO/IEC 27001
How Varmo maps the standard.
Customers ask for proof of information security, ISO/IEC 27001 certification is on the horizon, and the ISMS has to run alongside day-to-day business. Varmo guides you through the setup and keeps operations lean.
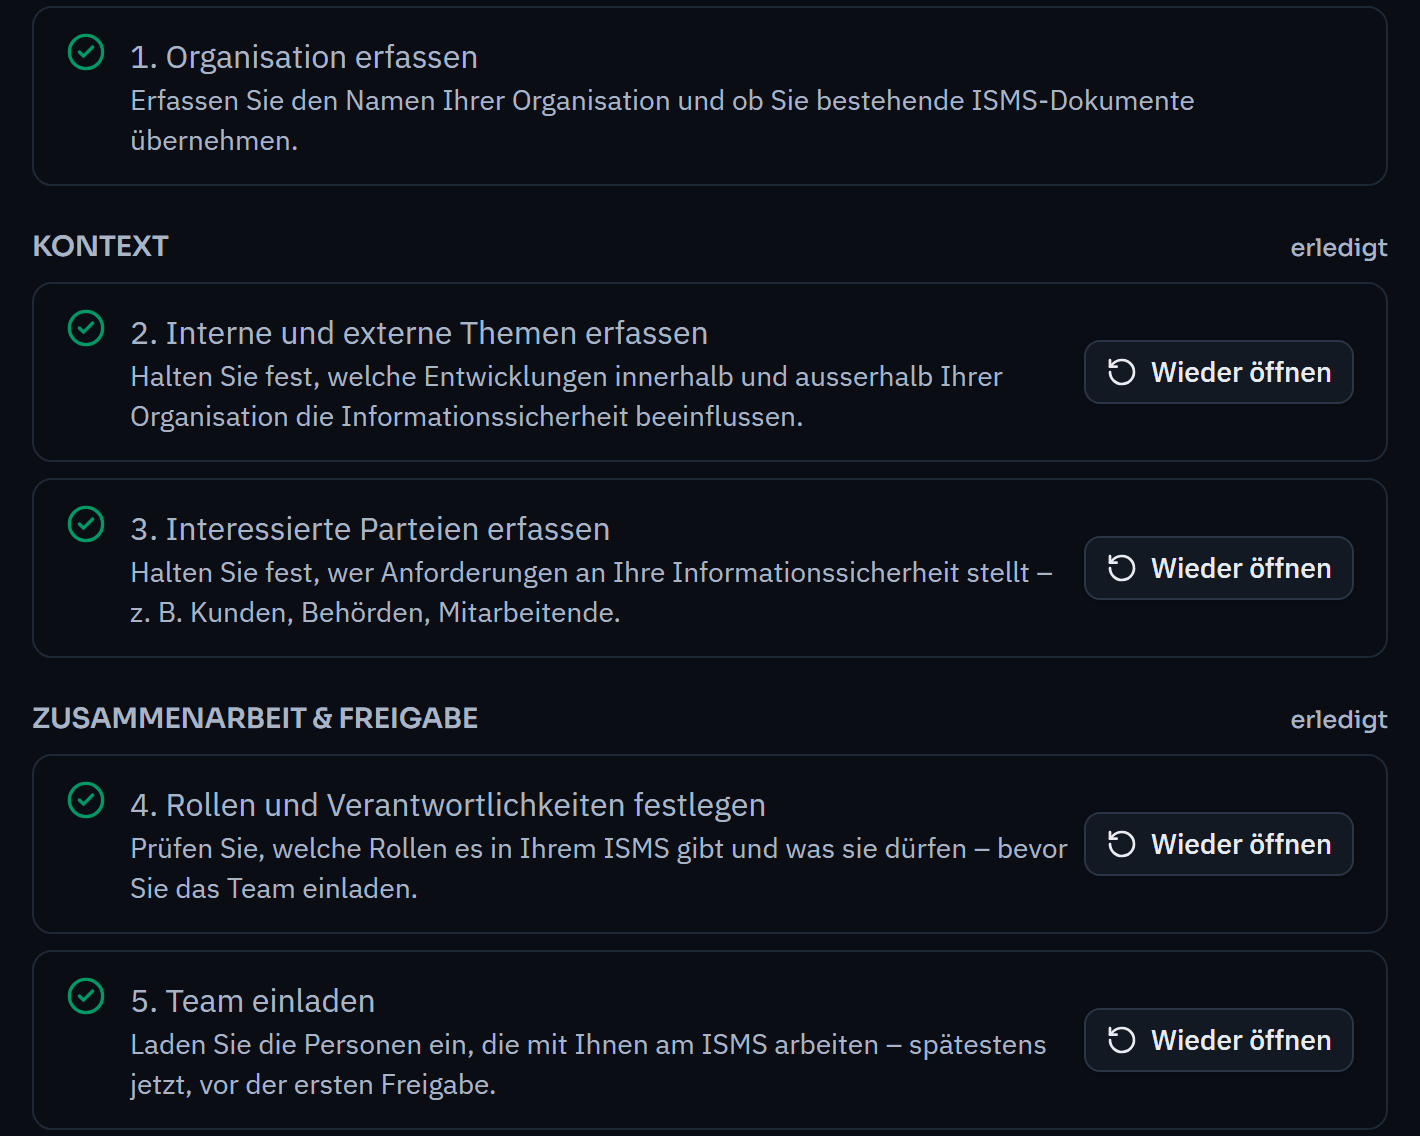
The setup wizard takes you step by step through the build: organisation, context, approvals, risk methodology, frameworks, asset structure and your first assets. Every step explains what it is about and why.
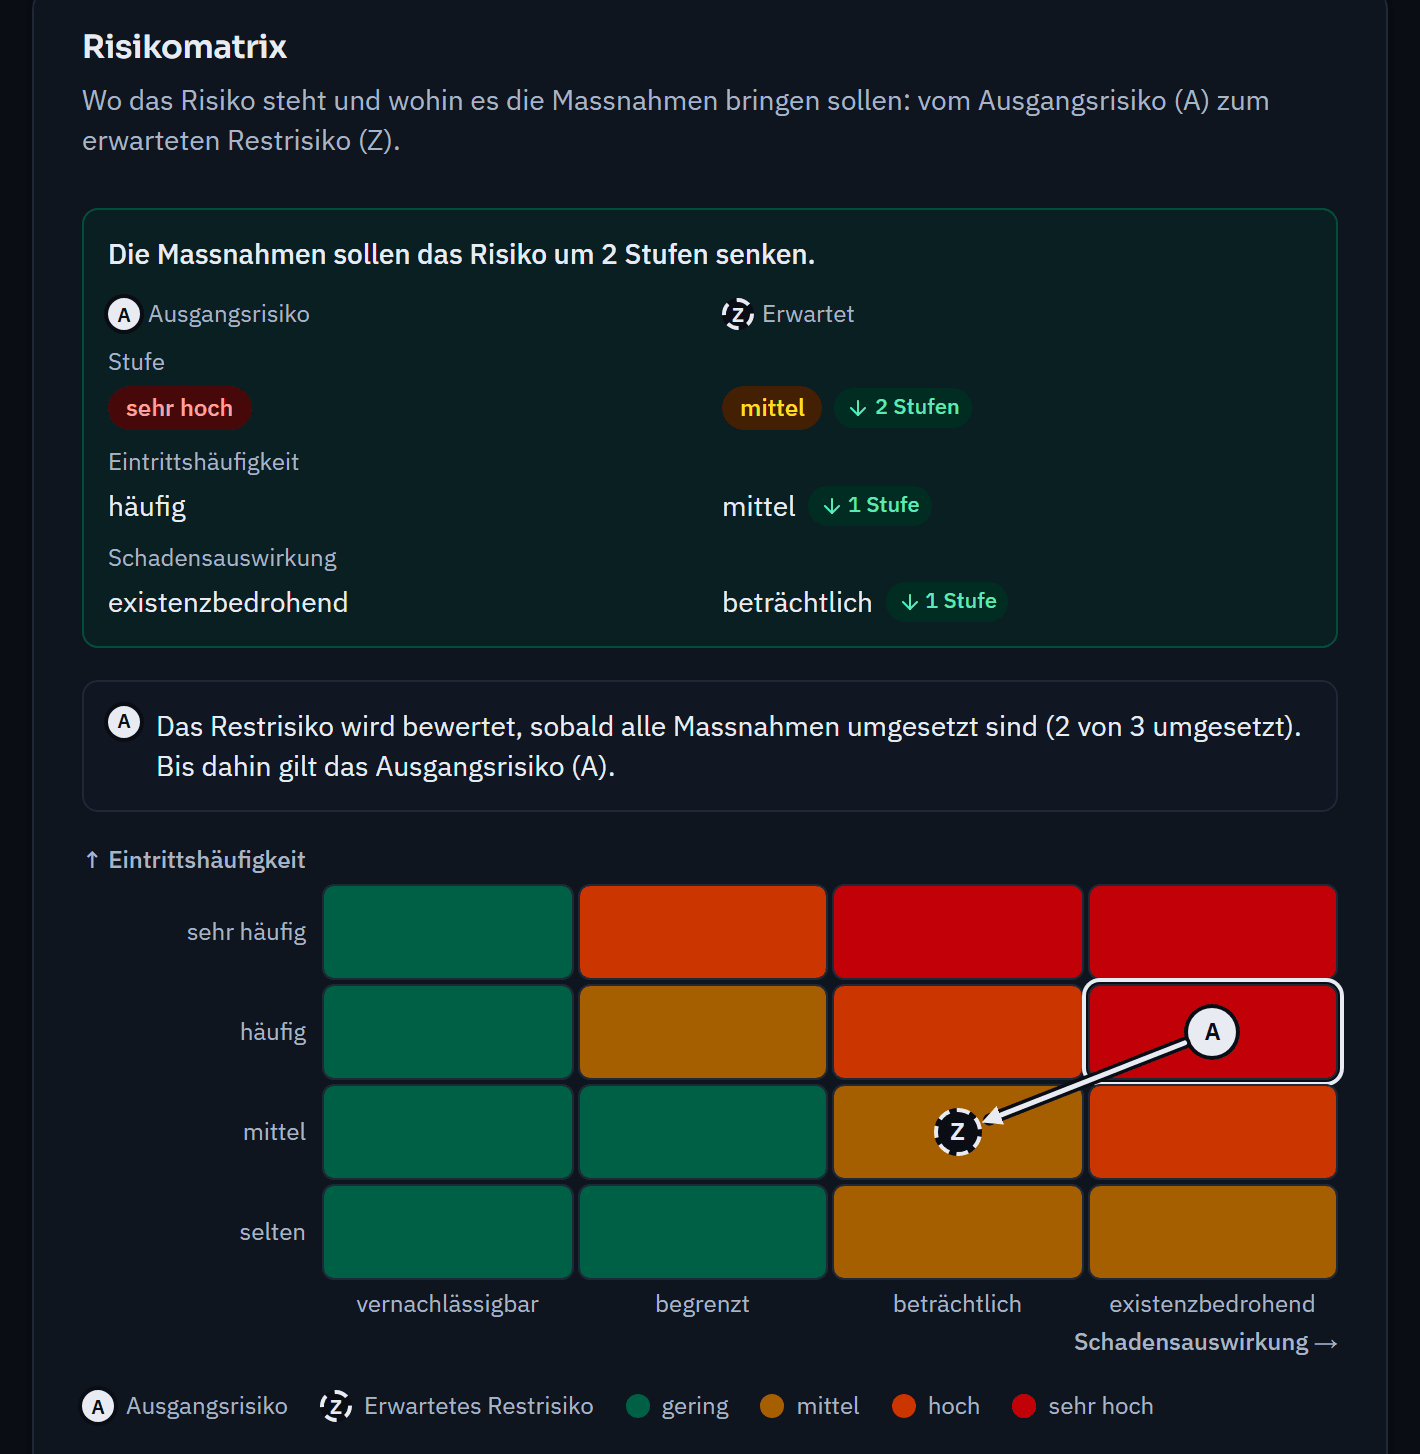
System owners assess the protection requirements, and the risk analysis evaluates threats such as ransomware or the failure of a service provider. For every risk, it is clear who has to act next.
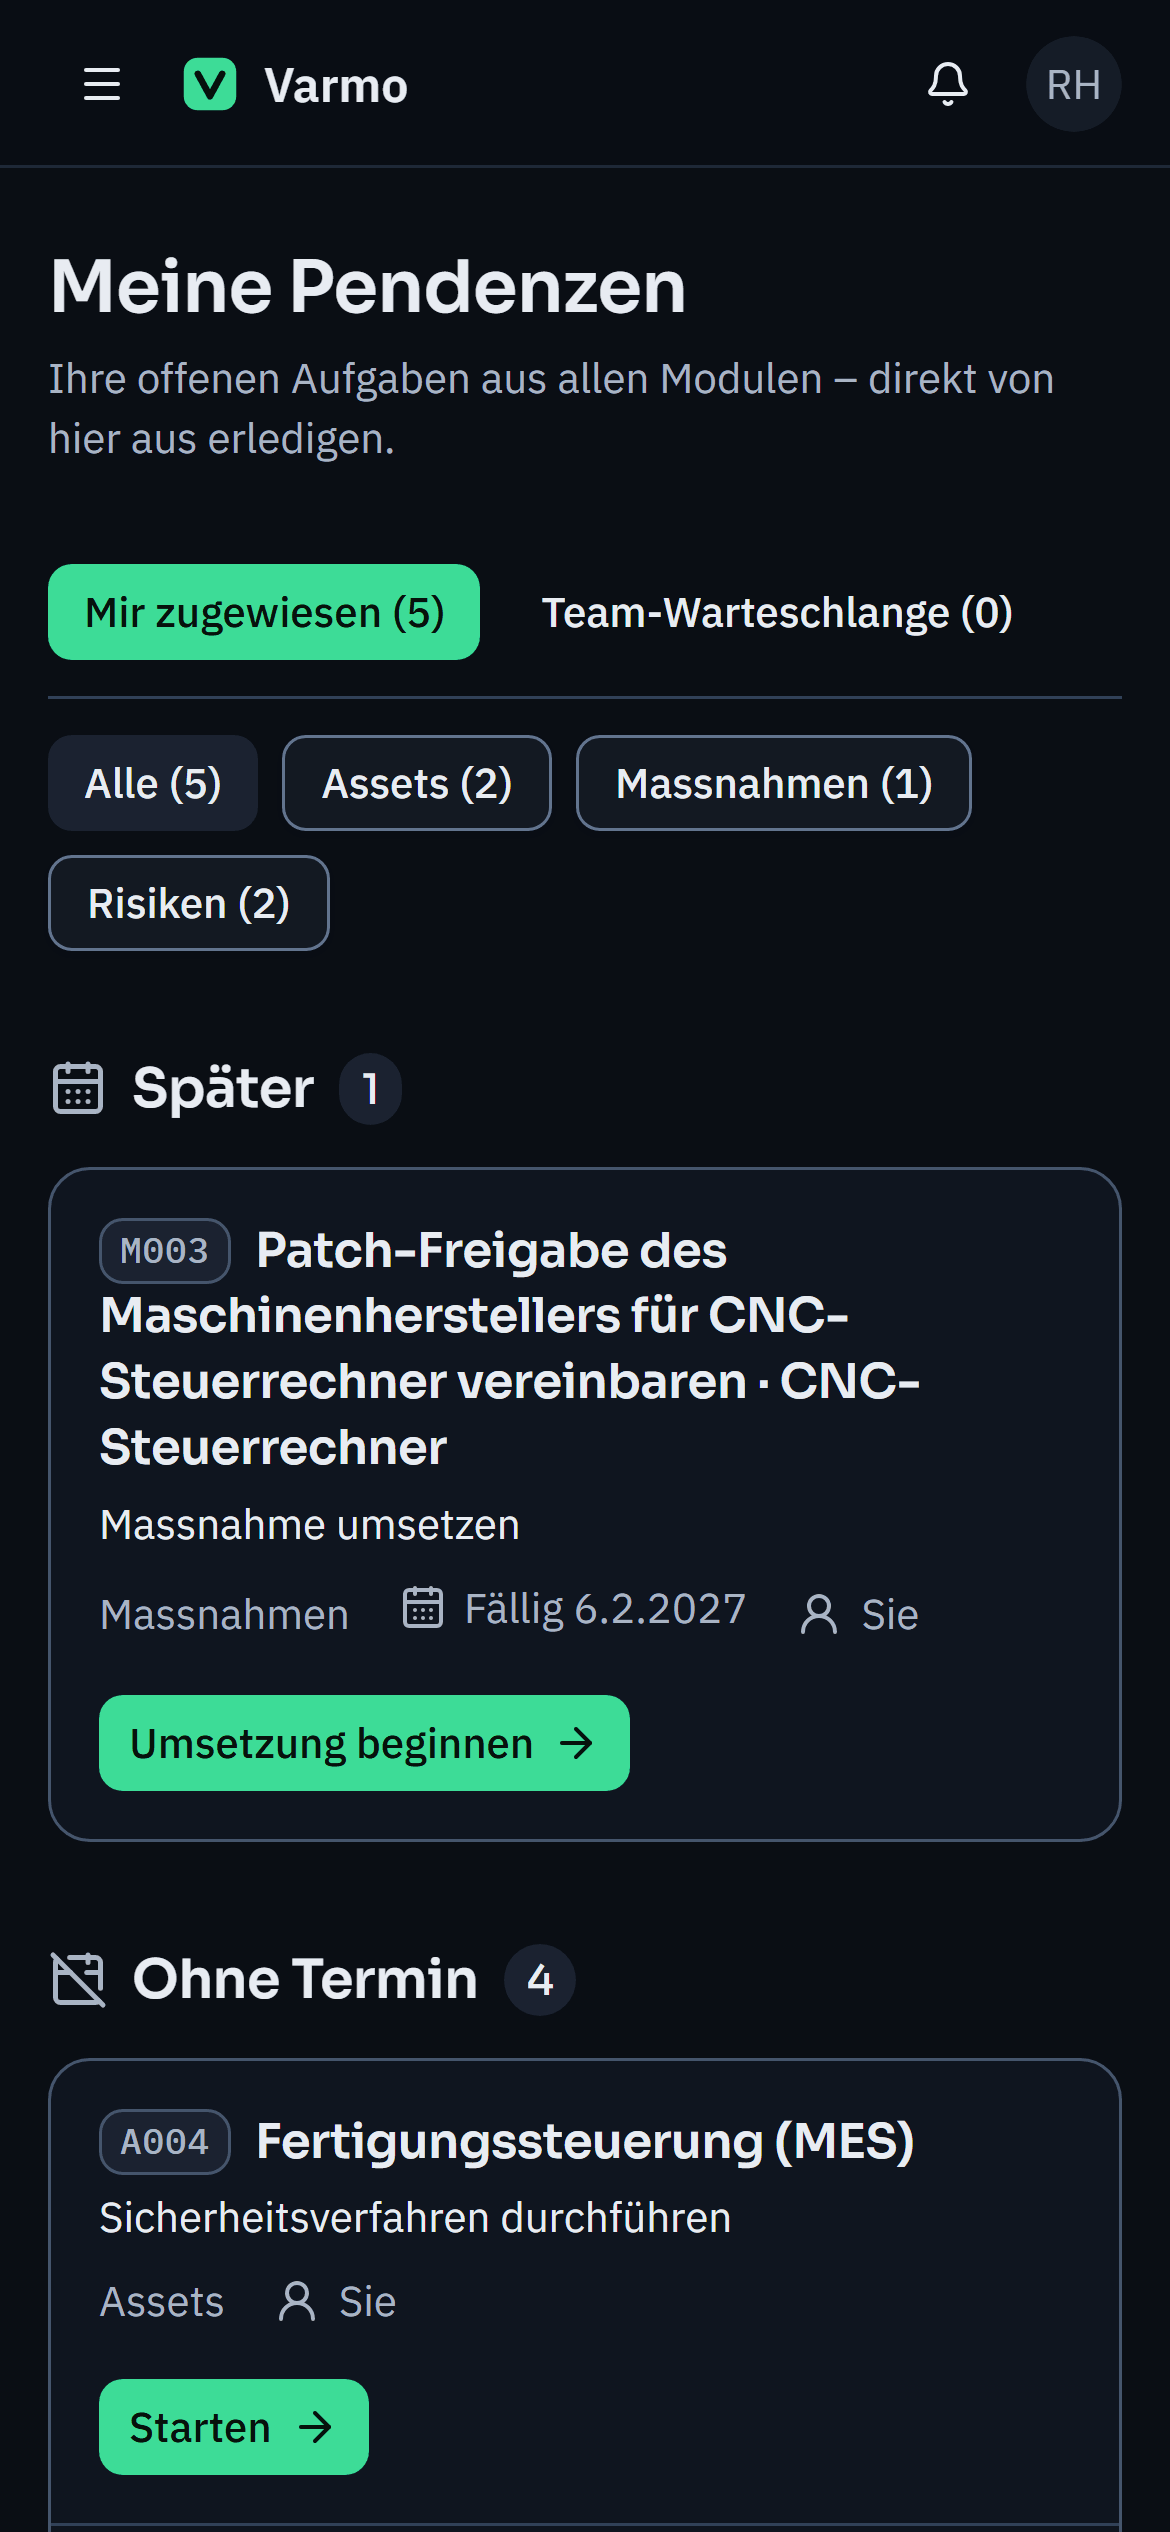
Everyone sees their own tasks: implement a measure, carry out a control, acknowledge a policy, review a risk. Anything overdue stands out, on mobile too.
In small organisations, one person often holds several roles. Where this conflicts with segregation of duties, it is recorded as a justified exception instead of being kept quiet. The four-eyes principle for approvals still always applies.
Statement of Applicability, evidence for each requirement, internal audit and management review are all in the same system. From the Starter plan, the readiness check shows where gaps remain before the certification audit.
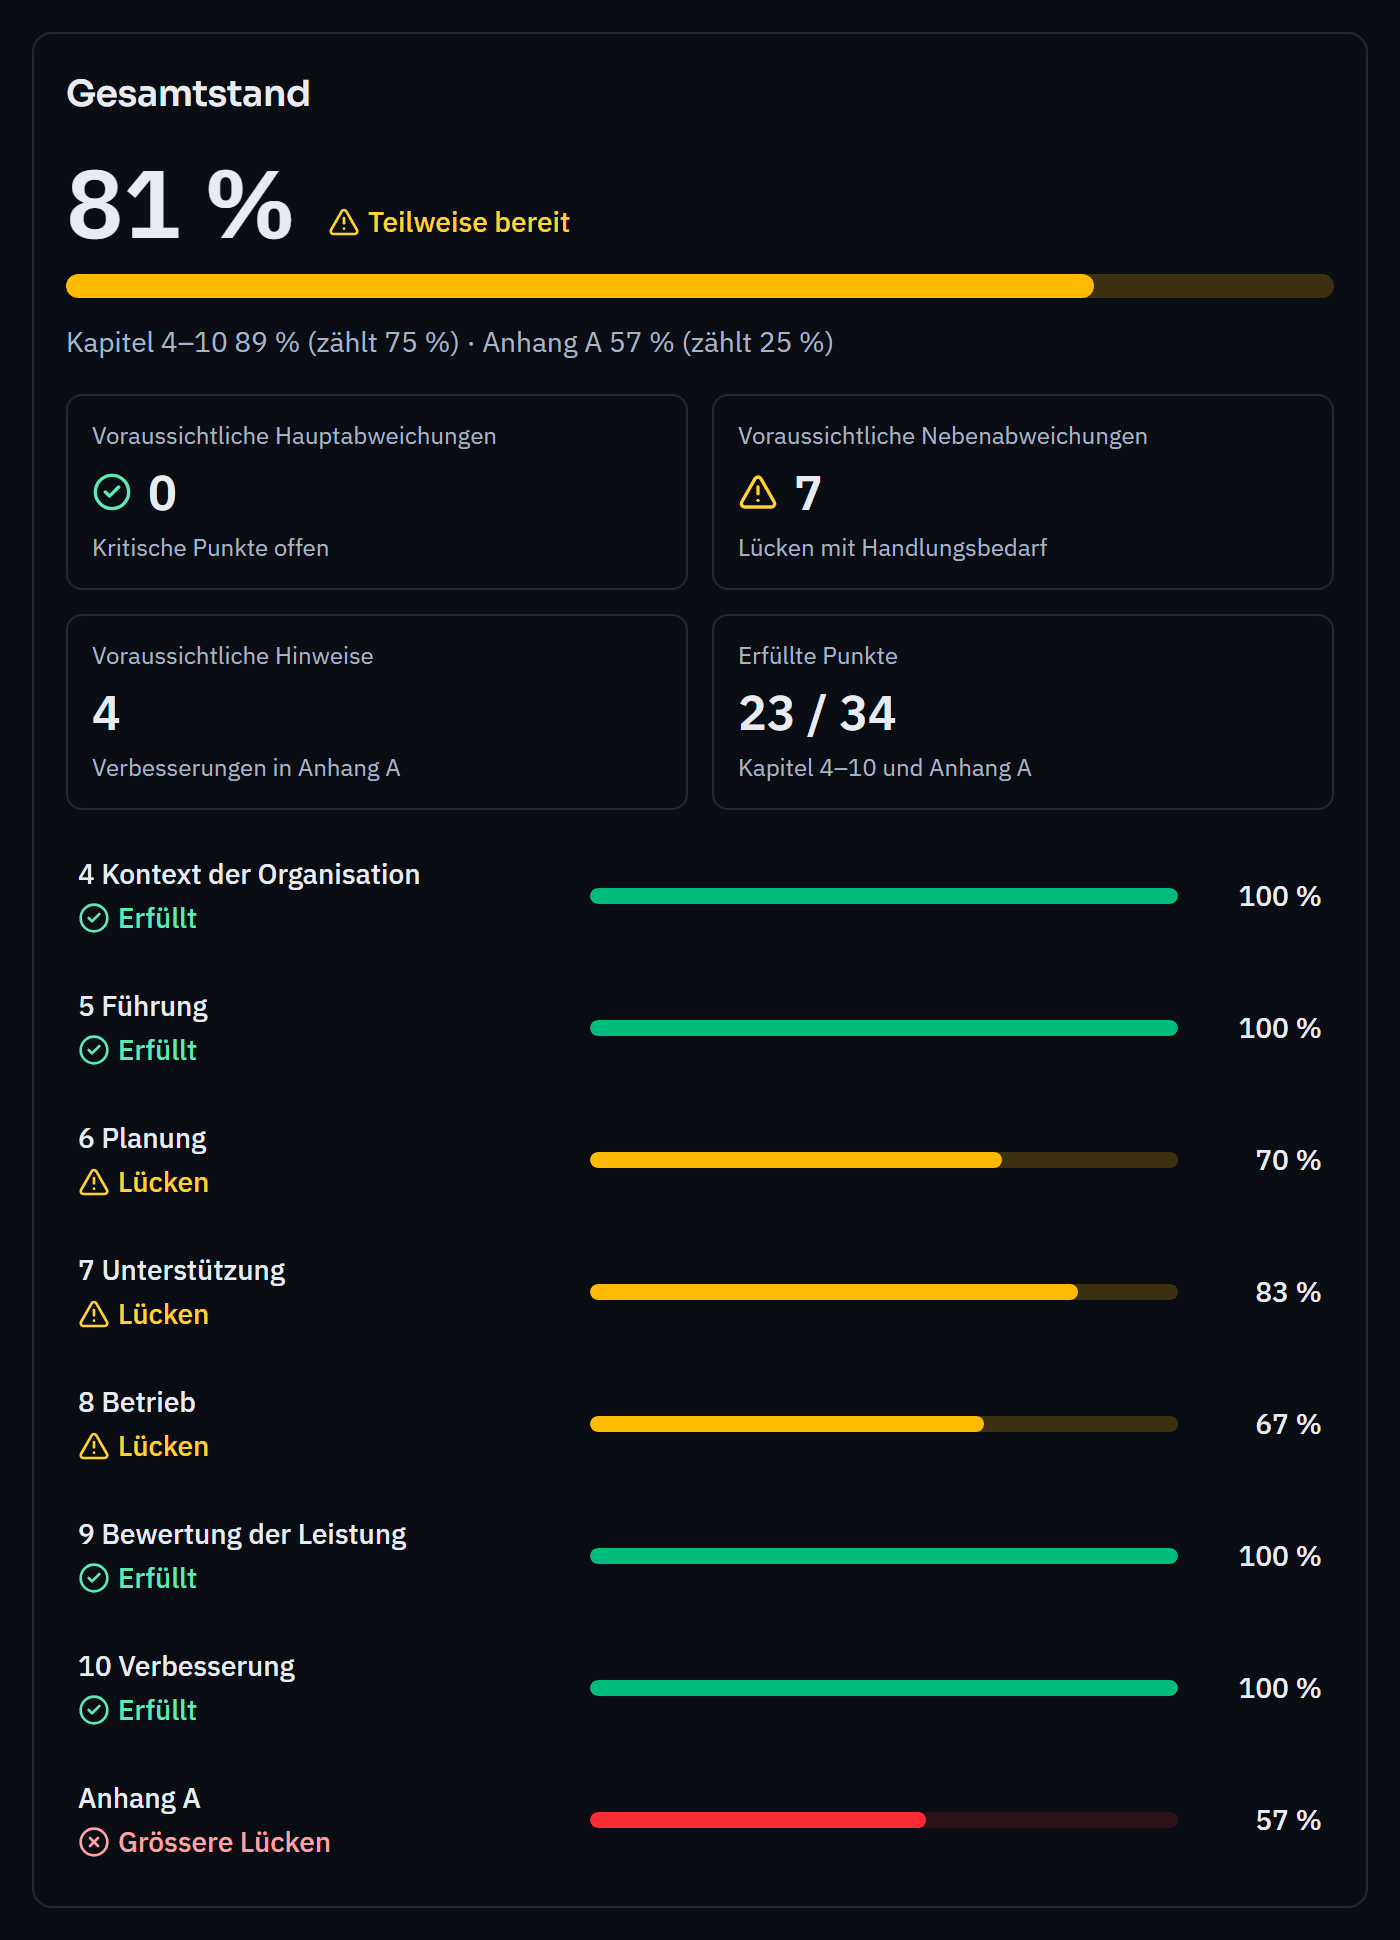
How Varmo maps the standard.
The wizard and the tasks in detail.
Plans from Starter to Ultimate, try it free for 30 days.
Yes. Small organisations in particular usually have one person looking after the ISMS alongside other duties. The guided process always shows them the next step. With the free trial, you can try every feature for 30 days.
That depends on your experience. The software structures the process and explains every step, but it does not replace a professional assessment of your risks.
The biggest cost is the working time of the people involved and, if you want them, consulting and the certification audit. Varmo reduces the effort for structure, evidence and reminders; plans and prices are on the pricing page, and the 30-day trial is free.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.