Assets & protection requirements
Protection requirements analysis and security procedures in detail.
Grundschutz++ is the successor of the IT-Grundschutz Compendium of Germany’s Federal Office for Information Security (BSI). Varmo takes the user catalogue directly from the BSI’s OSCAL format and applies it per asset in the security procedure – only where a requirement actually belongs.
Platform framework from the Business plan
All requirements of the user catalogue: methodology (governance, structure modelling, implementation, improvement, monitoring, risk) and the state-of-the-art kernel from information and assets through authorisation and detection to development, including sub-requirements.
For each requirement the BSI names the target objects. Varmo derives from them what it applies to: the organisation, applications, IT systems and networks, buildings and rooms, or service providers. Whoever is responsible for a server does not receive requirements about buildings or personnel.
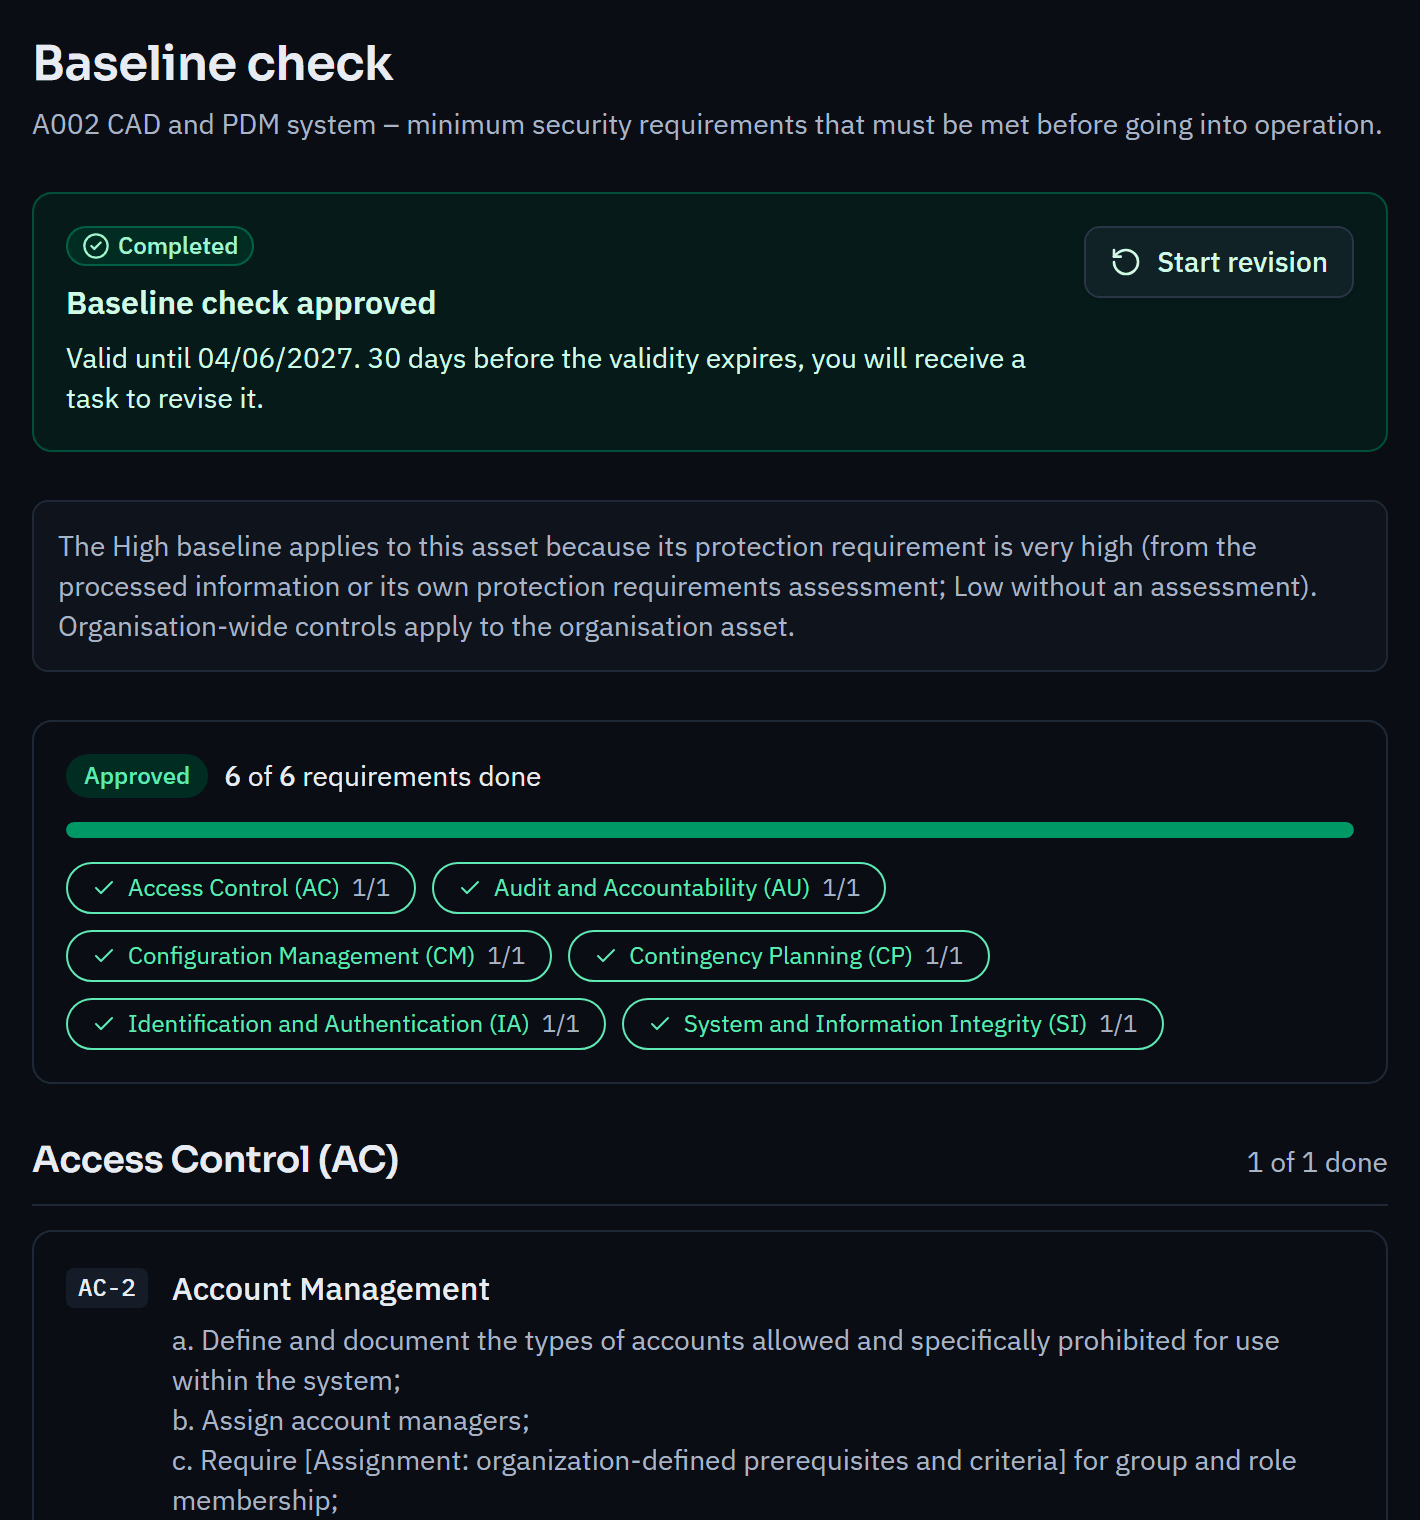
Requirements of the level “normal” apply at every protection requirement, those of the level “increased” only from a high protection requirement. The protection requirements analysis thus determines which requirements a system must meet; you can assign individual requirements in addition.
Grundschutz++ is mapped to ISO/IEC 27001:2022 Annex A according to the BSI’s official mapping and to NIST CSF 2.0 for coverage by function. Where the BSI records equivalence, fulfilment carries over to the other framework. In risk treatment, the requirements the BSI assigns to each elementary threat appear as suggestions. Mappings and coverage are included from the Business plan.
Protection requirements analysis and security procedures in detail.
Annex A as a framework, with the Statement of Applicability.
No. Grundschutz++ comes from Germany’s BSI and replaces the IT-Grundschutz Compendium. ICT baseline protection (directive Si001) is the requirement of the Swiss Federal Administration. Varmo includes both; they can be used side by side.
According to the BSI, the previous IT-Grundschutz Compendium remains valid until the end of 2028. New projects can start directly with Grundschutz++.
So far the BSI publishes Grundschutz++ in German only. In the English interface the requirements therefore remain in the German original; the framework and chapters are translated.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.