Readiness check
Gaps before the audit, from your data.
Certification to ISO/IEC 27001 is granted by an accredited certification body after an external audit. Varmo guides you to the evidence required there and shows beforehand where gaps remain.
You define and approve the scope, context, interested parties and the information security policy. The setup assistant guides you through these steps.
You assess risks according to your methodology and acceptance criteria, decide on treatment and select the Annex A requirements. This produces the Statement of Applicability (SoA), which you approve and record as a version.
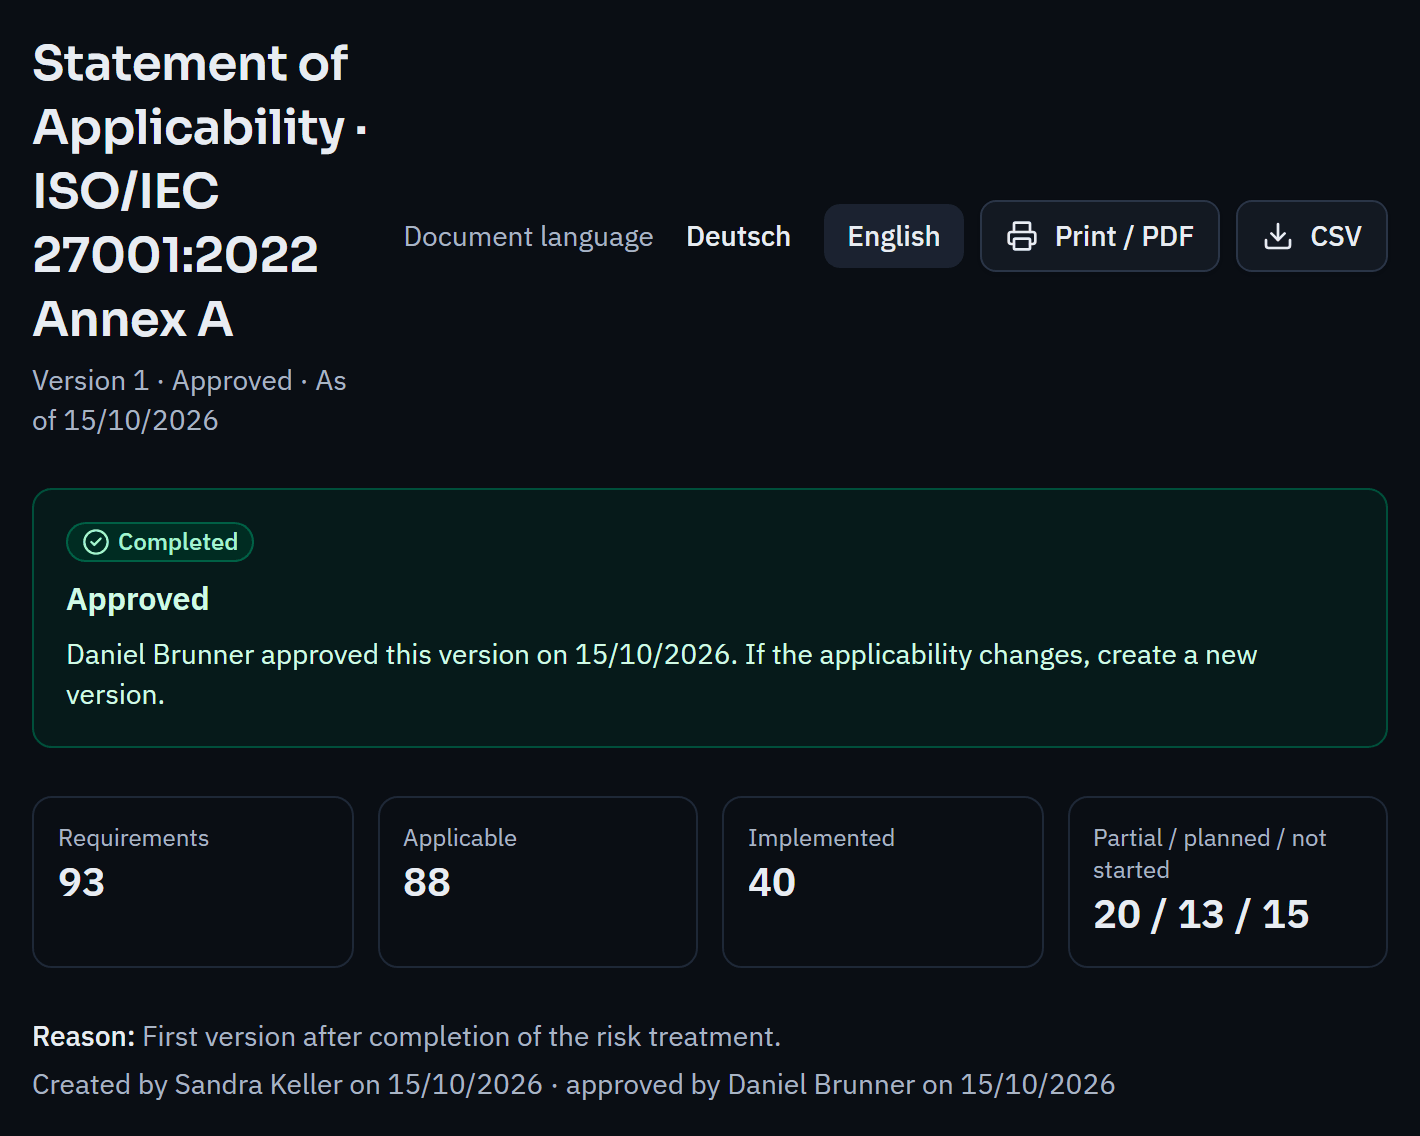
For each requirement you record how it is implemented and what proves it. Measures, controls and documents are linked to the requirements, and tasks remind you of due dates.
You run the internal audit with findings, corrections and effectiveness checks, and the management review with the inputs under ISO/IEC 27001 9.3, in the same system. Completed audits and reviews cannot be changed.
From the Starter plan, the readiness check uses your data to show where gaps remain before the certification audit and records each status as a report. The free self-assessment on the website gives a first impression.
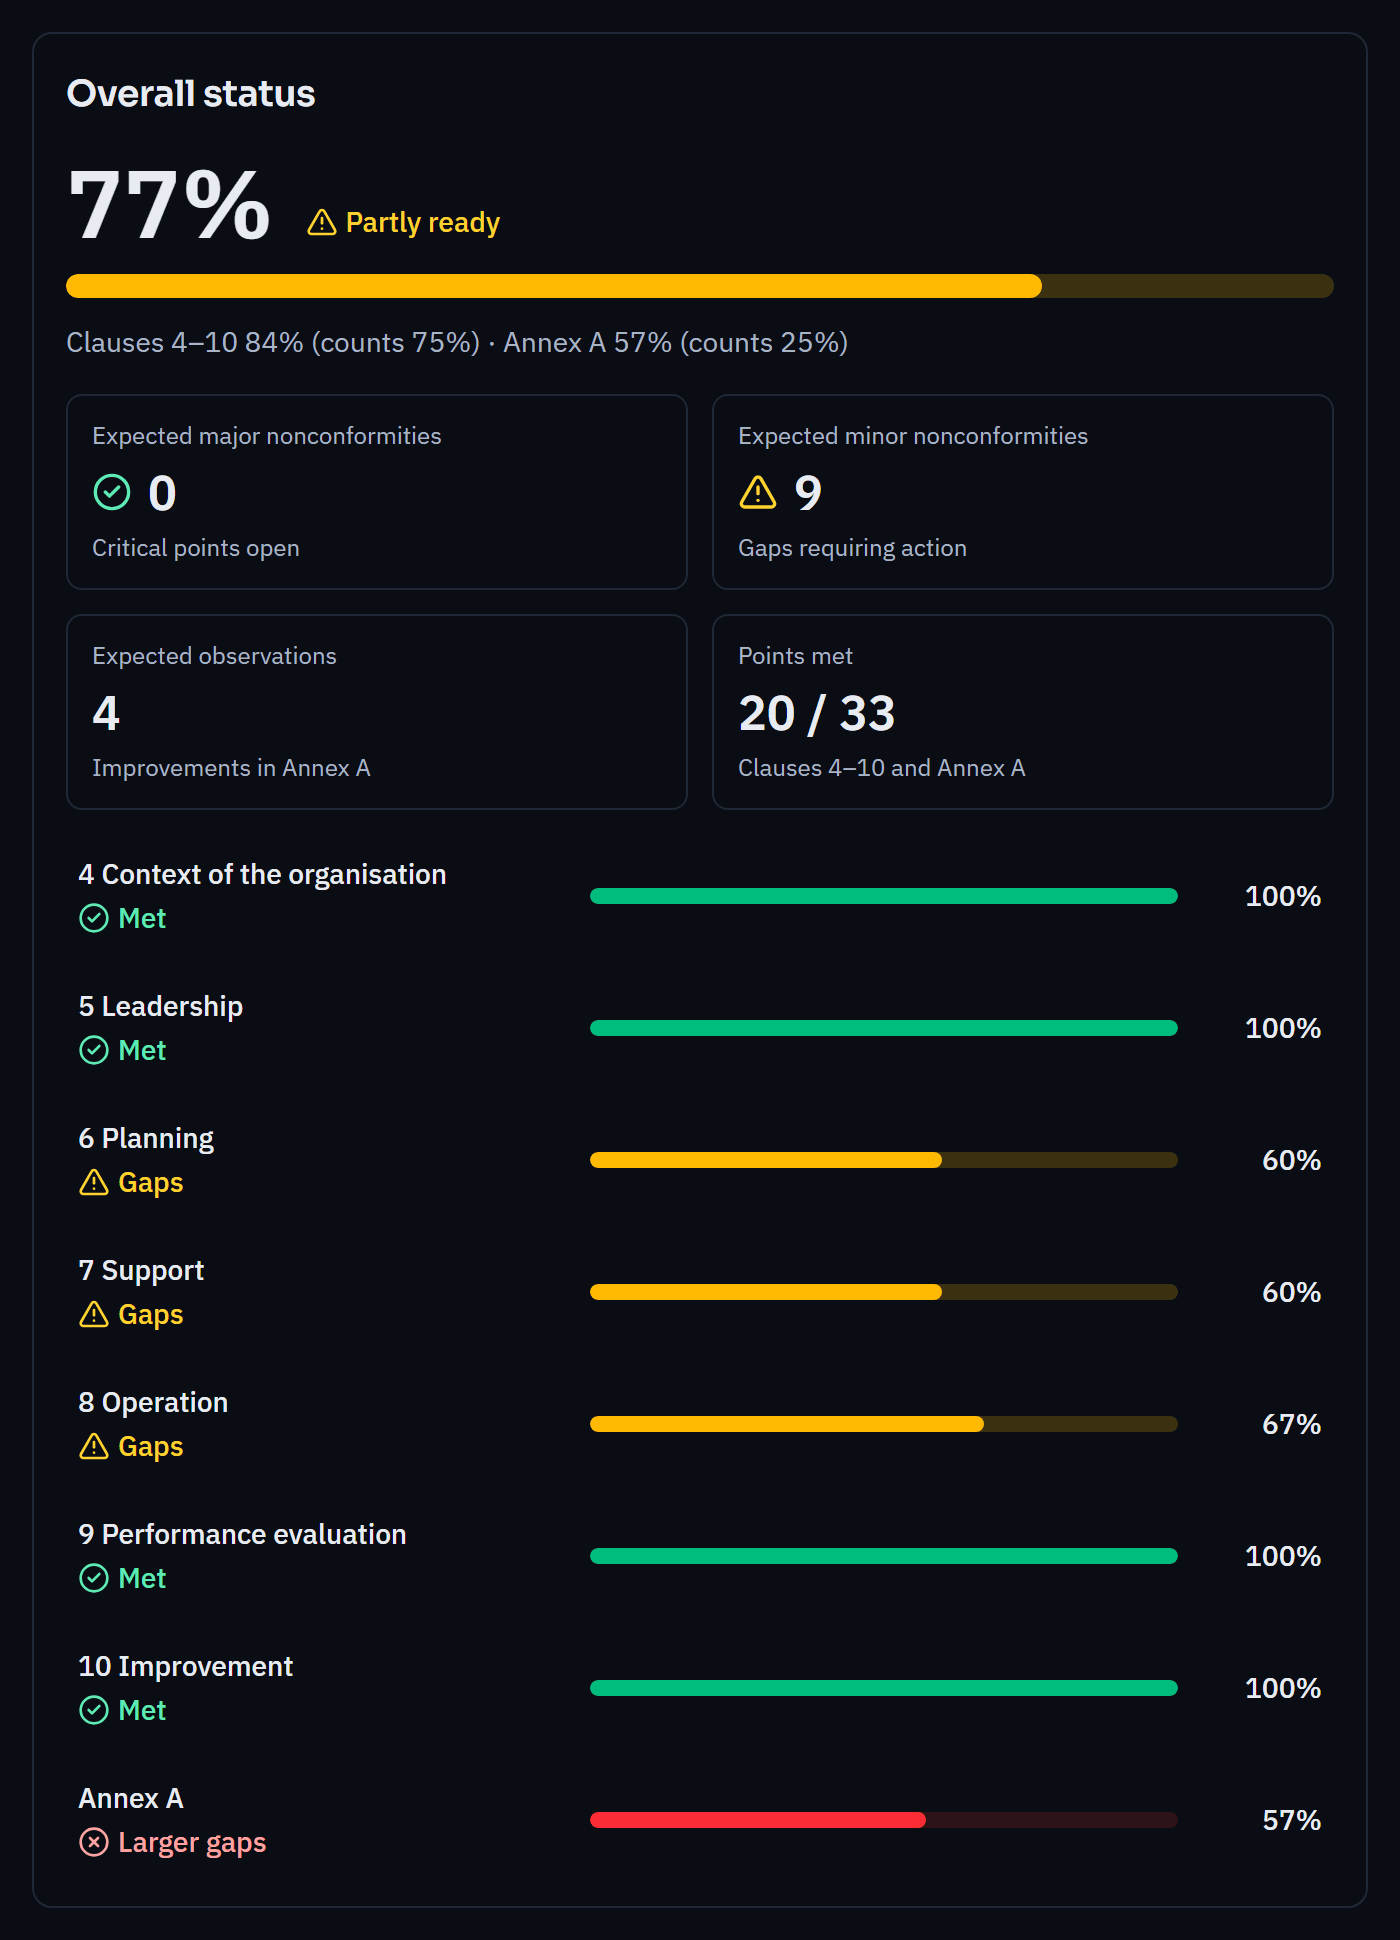
The certification audit is carried out by the certification body in two stages: first a review of the documentation, then a review of the implementation. Annual surveillance audits follow, and recertification after three years. Approvals under the four-eyes principle require at least two people.
Gaps before the audit, from your data.
The Statement of Applicability in detail.
Free, in about 5 minutes.
Build an ISMS step by step.
No. The certificate is granted by an accredited certification body after the certification audit. The software helps you build and run the ISMS and keep the evidence ready for the audit.
Among other things the scope, the policy, the risk assessment and treatment plan, the Statement of Applicability, objectives, evidence of competence, results of monitoring and internal audit, the management review and how nonconformities were handled. This evidence is created in the software as part of the workflow.
Yes. The free self-assessment on the website gives a first impression. In the software, the readiness check from the Starter plan uses your own data to show which points are still open before the audit.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.