Data protection & DPIA
Record of processing, FADP and GDPR obligations, impact assessment.
The GDPR requires appropriate technical and organisational measures to ensure a level of security appropriate to the risk (Art. 32). Varmo includes Art. 32 as a framework and links it with the protection requirements analysis of your systems. The record of processing activities, the notification of personal data breaches and the impact assessment under the GDPR are part of the modules.
Platform framework in all plans, for organisations that have selected the GDPR
7 requirements from Art. 32 GDPR: a level of security appropriate to the risk, assessment of the risks, regular review of effectiveness, processing only on instructions, and the examples of measures in paragraph 1 (pseudonymisation and encryption, confidentiality, integrity, availability and resilience, timely restoration).
The GDPR does not prescribe fixed measures but measures appropriate to the risk for the data subjects. The protection requirements analysis shows which systems need which measures; the examples in the guidance are suggestions, not obligations.
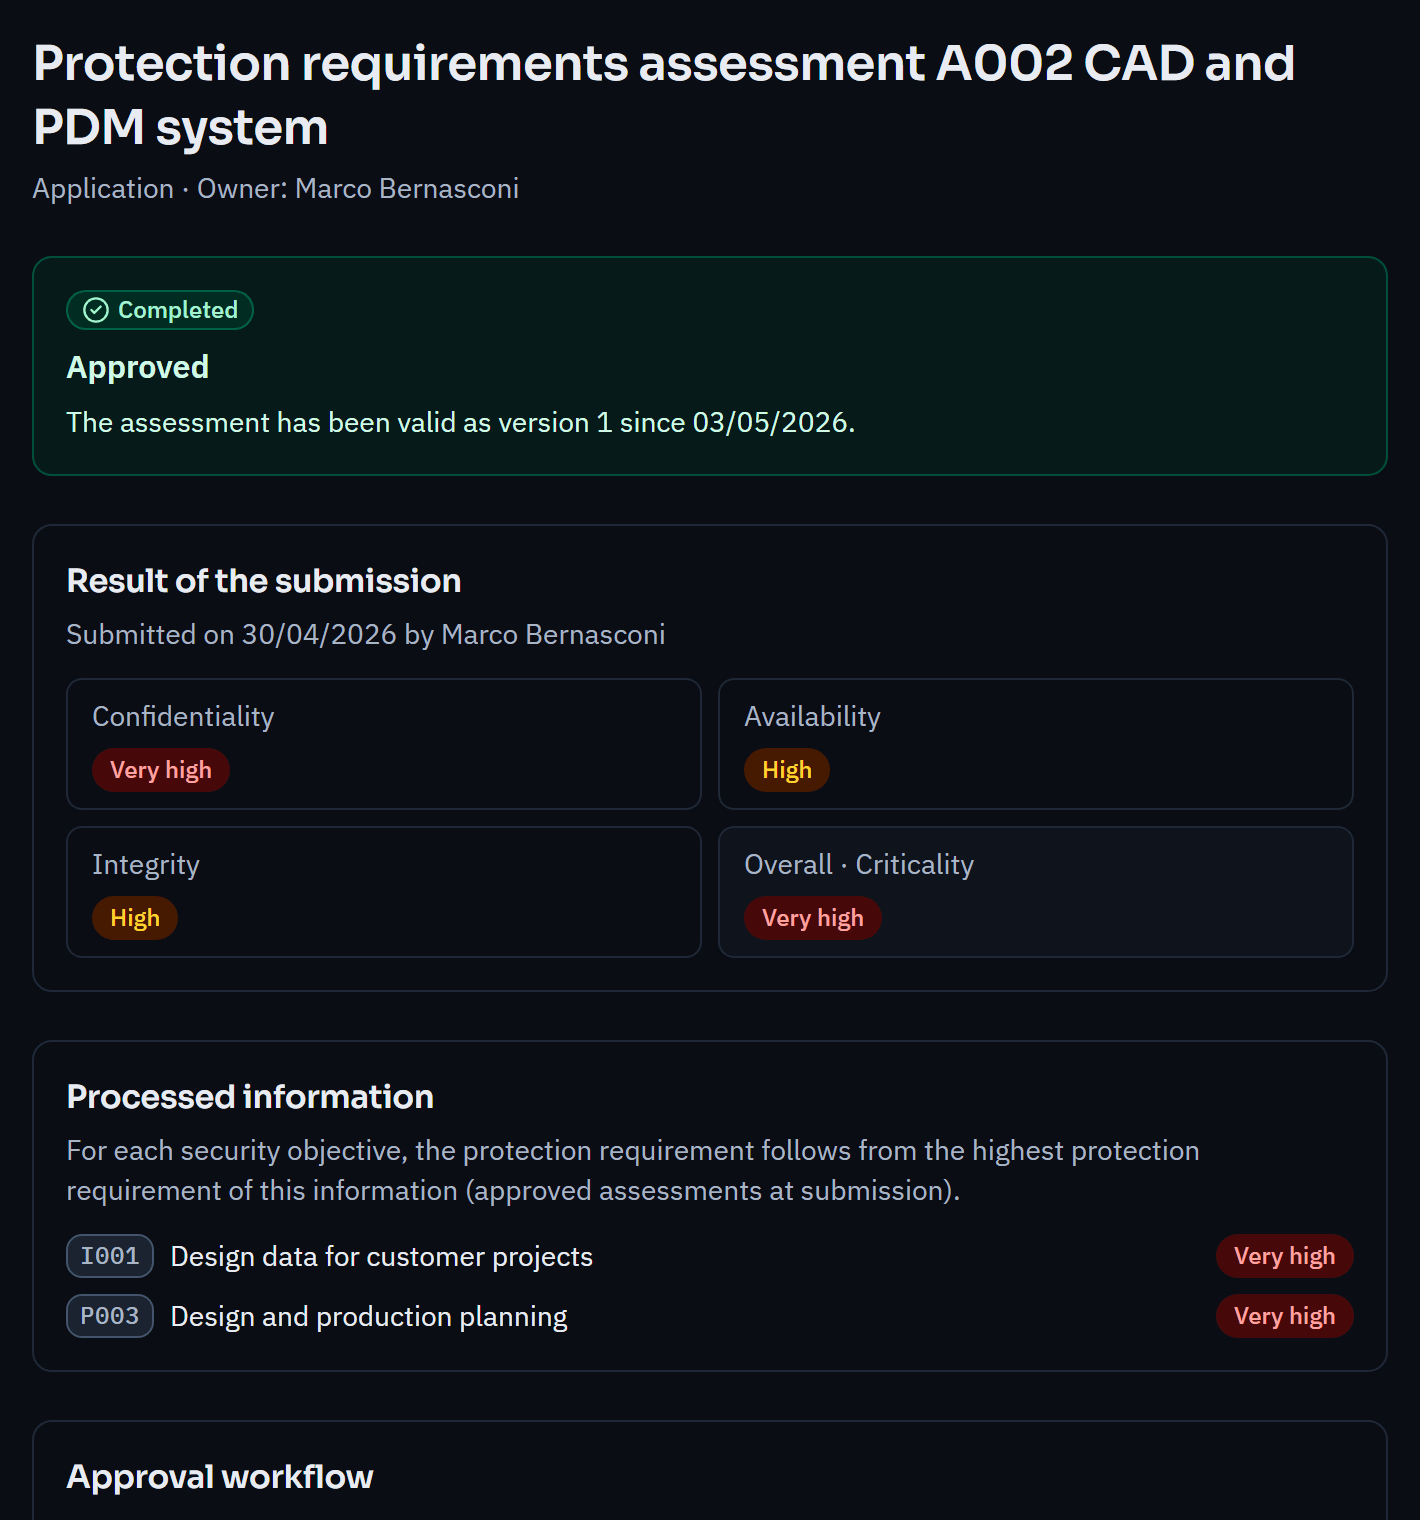
You choose whether the Swiss FADP, the GDPR or both apply to your organisation. With the GDPR, Varmo guides you through the further obligations:
The framework is deliberately not mapped automatically to any other framework: Art. 32 sets objectives, not fixed measures, and only concerns personal data. An implementation under ISO/IEC 27001 or the DPO therefore does not count as fulfilled by itself; you link requirements yourself where needed.
Record of processing, FADP and GDPR obligations, impact assessment.
Art. 1–6 DPO as a framework for the Swiss data protection act.
Organisations subject to the GDPR, for example because they are established in the EU or offer goods and services to people in the EU (Art. 3). Varmo offers the framework as soon as your organisation has selected the GDPR in the data protection settings.
If both laws apply to your organisation, yes: the frameworks sit side by side. Many measures serve both; in Varmo you link a measure with the requirements of both frameworks.
FREE · ABOUT 5 MINUTES
A traffic light per clause, your next steps and the right plan. No sign-up; your answers stay in your browser.
How close are you to ISO/IEC 27001?
In a personal demo, we show you the way to the readiness report, with no obligation. Or try it free for 30 days with every feature.